The AI Governance Tools Landscape: Platforms & Capabilities
The market for AI governance tools is expanding quickly as organizations face mounting pressure to manage artificial intelligence responsibly. The regulatory backdrop is the main driver. In the European Union, the AI Act is binding, with fines of up to 35 million euros or 7 percent of global annual turnover for the most serious violations, while in the United States federal policy has shifted toward innovation, which paradoxically makes voluntary frameworks and certifiable standards more important for any organization that wants a defensible AI governance posture. This guide walks through the AI governance software landscape: the principles these tools are built to support, the frameworks, standards, and regulations they help you satisfy, the leading platforms and what each does well, the organizational roles that make any of it work, and the maturity stages organizations move through on the way to automated governance. Core Principles of Responsible AI Governance Effective AI governance rests on four foundational pillars: transparency, accountability, security, and ethics. These principles keep AI systems understandable, owned, protected, and fair across their lifecycle, and every credible governance program maps back to them. Transparency: model cards and explainability Stakeholders need visibility into how an AI system works. Model cards have become the standard way to document a model, much like a nutrition label, capturing its architecture, training-data sources, performance, and intended use. Trust depends on accurate predictions, traceable processes, and enough human-readable explanation that practitioners can spot bias or justify a decision. Accountability: role-based ownership An AI system cannot face consequences, so the organization must define who is responsible when something goes wrong. A 1979 IBM training document made the point that endures today: a computer can never be held accountable, therefore a computer must never make a management decision. In practice, leading organizations run cross-functional governance committees, often led jointly by the CIO, CISO, and legal, that approve high-risk cases and assign oversight, splitting accountability between the teams that use AI and the teams that build and maintain it. Security: data protection and model integrity A reliable AI system needs protection from both deliberate and accidental interference, covering data sources, algorithms, and stored information. Practical steps include anonymizing and encrypting sensitive data, granting AI systems only the access they need, signing sensor and input data cryptographically, and verifying regularly that a system has not been compromised and still serves its intended purpose. Ethics: bias mitigation and fairness audits Ethical AI starts with addressing bias, which can enter through training data, algorithm design, or poor sampling. Mitigations include representative training data, fairness checks built into development, techniques such as re-sampling and re-weighting, and diverse teams. Regular fairness audits have become a primary way to surface and reduce risk, and in fields like hiring, lending, and healthcare, explainability is increasingly a legal expectation rather than a nicety. Teams should keep detailed records of fairness tests and remediation as governance evidence. Frameworks, Standards, and Regulations One common source of confusion is treating every governance reference point as a “framework.” They are not the same kind of instrument, and the difference matters for how you use them. The three most important are a voluntary framework, a certifiable standard, and a binding regulation. If you are weighing which to anchor on, it helps to see how the major options compare directly. NIST AI Risk Management Framework (a voluntary framework) The NIST AI Risk Management Framework is a voluntary framework, launched in January 2023, that helps organizations identify, assess, and reduce AI risk across the lifecycle through four functions: Govern, Map, Measure, and Manage. NIST added a Generative AI Profile in July 2024 to address risks specific to generative AI. The framework is being revised under current US policy, but its core structure remains the most widely used voluntary baseline, and any organization of any size can adapt it to its own risk profile. ISO/IEC 42001 (a certifiable standard) ISO/IEC 42001:2023 is the first international standard for AI management systems, and unlike a framework it can be independently certified. Built on the Plan-Do-Check-Act method, it requires AI risk management processes, AI system impact assessments, lifecycle management, third-party supplier oversight, and continuous improvement. Certification lets an organization signal its commitment to responsible AI to customers and regulators; Microsoft, for example, has pursued ISO/IEC 42001 certification for Microsoft 365 Copilot. For SaaS providers selling into the enterprise, ISO 42001 and the EU AI Act are quickly becoming a procurement gate. EU AI Act (a binding regulation) The EU AI Act is the world’s first comprehensive AI law, and unlike the voluntary instruments above it imposes binding obligations based on a risk classification: Unacceptable risk (prohibited practices): banned outright, including social scoring and subliminal manipulation. High risk: subject to strict requirements covering conformity assessment, risk management, data governance, transparency, and human oversight. Limited risk: specific transparency obligations, such as telling users they are interacting with AI. Minimal risk: no specific restrictions beyond existing law. Violations of the prohibited-practice rules can draw fines of up to 35 million euros or 7 percent of global annual turnover. The Act applies in phases: prohibited practices took effect in early 2025 and obligations for general-purpose AI models in August 2025. The high-risk timeline is currently in flux. Under the EU’s Digital Omnibus package, EU institutions reached a provisional political agreement in May 2026 to defer high-risk obligations, moving Annex III use cases such as biometrics, critical infrastructure, education, and employment to December 2, 2027, and AI embedded in regulated products to August 2, 2028. Treat the new dates as provisional. The Digital Omnibus reschedule is a political agreement, not yet settled law. It takes legal effect only on formal adoption and publication in the EU’s Official Journal, and if it is not adopted before August 2, 2026, the original high-risk deadline of August 2, 2026 still applies. Organizations planning EU activity should keep preparing against the original deadline and track formal adoption closely. Enterprise AI Governance Tools and Their Capabilities As the number of models grows, organizations need better ways to oversee them, and the leading platforms have specialized around distinct governance challenges.
AI Governance and Legal Liability: What Changed in 2026
AI governance is the set of frameworks, policies and controls that determine who answers for an AI system when it causes harm, and in 2026 the answer to that question moved twice. The European Union deferred its high-risk obligations by sixteen months. Colorado repealed the first comprehensive state AI law in the United States before it ever took effect. Legal officers who built compliance roadmaps against the 2025 regulatory picture are now pointing resources at deadlines that no longer exist and at a statute that no longer exists. This guide restates where liability actually sits as of September 2026, what the current obligations are, and what a defensible program looks like when the ground keeps moving. Why AI Governance Liability Changed in 2026 Three developments between December 2025 and July 2026 rewrote the compliance calendar. None of them reduced exposure. All of them changed where the exposure sits and when it arrives. The EU Deferred Its High-Risk Deadline The EU AI Act entered into force on August 1, 2024 with a staggered rollout. The core high-risk obligations were originally set to apply from August 2, 2026 for standalone Annex III systems and August 2, 2027 for AI embedded in products already covered by EU product safety law. By late 2025 it was clear the supporting ecosystem was not ready: harmonised standards from CEN-CENELEC were behind schedule, Commission guidelines were still in draft, and many Member States had not designated national competent authorities. The European Commission proposed the Digital Omnibus on AI on November 19, 2025. After a failed trilogue in April 2026, the institutions reached political agreement on May 7, 2026. The result, Regulation (EU) 2026/1744, was published in the Official Journal on July 24, 2026 and entered into force on July 27, 2026, six days before the original deadline would have bitten. The new dates are binding law, not a pending proposal. Standalone Annex III high-risk obligations now apply from December 2, 2027. Annex I embedded systems move to August 2, 2028. What did not move matters just as much: the Article 5 prohibitions and the obligations for providers of general-purpose AI models were already in force and were untouched, and the Article 50 transparency obligations applied from August 2, 2026 as originally scheduled. The Omnibus also added a new prohibition covering AI systems that generate non-consensual intimate imagery and child sexual abuse material. Treat the deferral as a resourcing window, not a reprieve. The obligations did not get lighter. Organizations that paused their Annex III workstreams in August 2026 will face the same conformity assessment, the same technical documentation requirement and the same registration duty in December 2027, with sixteen fewer months of accumulated evidence. Colorado Repealed the Law Everyone Planned For Colorado SB 24-205, signed in May 2024, was the first comprehensive state AI law in the United States and the template most legal teams used to model state-level exposure. It imposed a duty of care aimed at preventing algorithmic discrimination, required detailed algorithmic impact assessments, mandated attorney general notification, and established a rebuttable presumption of compliance for organizations following the NIST AI Risk Management Framework. It never became operative. Its effective date slipped from February 1, 2026 to June 30, 2026. In April 2026 xAI sued to enjoin enforcement on constitutional grounds, the Department of Justice intervened in support, and a federal magistrate stayed enforcement. On May 14, 2026 Governor Polis signed SB 26-189, which repealed SB 24-205 outright and replaced it with the Automated Decision-Making Technology Act, effective January 1, 2027. The replacement is narrower by design. The duty of care is gone. The mandatory impact assessments are gone. The high-risk classification is gone. The rebuttable presumption for NIST AI RMF alignment is gone. What remains is a disclosure and rights framework built around automated decision-making technology that materially influences a consequential decision, with three-year record-keeping obligations and a sixty-day pre-enforcement cure period administered by the attorney general that sunsets on January 1, 2030. If a compliance roadmap still contains a Colorado high-risk workstream, it is aimed at a statute that was repealed before it activated. That is the single most common stale assumption in AI governance programs built during 2025. The Federal Preemption Push On December 11, 2025 the White House issued an executive order titled “Ensuring a National Policy Framework for Artificial Intelligence,” which seeks to establish a uniform federal AI policy that would displace state laws considered inconsistent with it. The order directs the Attorney General to establish an AI Litigation Task Force to challenge state AI laws on interstate commerce and preemption grounds, directs the Commerce Department to identify burdensome state laws, and conditions federal broadband funding on state compliance. An executive order does not carry statutory preemption force on its own. What it does create is sustained litigation risk around state enforcement, which is precisely what played out in Colorado. Elevate covers the operational consequences of this shift in its analysis of the 2026 AI executive order and what it means for cybersecurity and AI governance. Development Status as of September 2026 Practical effect on legal exposure EU AI Act Annex III high-risk Deferred to December 2, 2027 More preparation time, same obligations, no reduction in eventual scope EU AI Act Article 5 prohibitions In force, unchanged Highest penalty tier, applies now EU AI Act Article 50 transparency Applied from August 2, 2026 Live obligation, often overlooked in the deferral coverage Colorado SB 24-205 Repealed before taking effect Duty of care, impact assessments and NIST safe harbor all removed Colorado SB 26-189 (ADMT Act) Effective January 1, 2027 Disclosure and rights framework, narrower scope Texas TRAIGA Effective January 1, 2026 Intent-based liability, NIST AI RMF affirmative defense available Federal preemption EO Signed December 11, 2025 Litigation risk on state enforcement, no direct preemption The table shows a pattern worth naming: the obligations that remain firmly in force are the prohibitions and the transparency duties, not the risk-management duties. Programs built to satisfy risk-management mandates still have value, because those
AI Governance Program Documentation Kit for Legal Teams
AI governance matters more than ever as technology advances faster in organizations worldwide. Knowledge workers have embraced AI tools, with over 70% using them weekly. Yet only 30% of organizations have formal AI policies. Legal teams must address this governance gap that creates major legal and compliance risks. AI governance needs specialized frameworks and documentation approaches, unlike traditional IT governance. Legal professionals will find our complete toolkit helpful when establishing proper oversight. Our resources line up with recognized standards like NIST AI RMF 1.0 and ISO/IEC 42001:2023. This alignment ensures your framework meets international best practices. The EU AI Act creates specific obligations that need attention to risk classification, transparency, human oversight, and documentation. Your team can implement effective AI governance without enterprise-scale resources or dedicated ethics boards, and with good reason too. In this piece, we’ll share practical templates, tools and workflows that help legal teams build strong AI governance principles. The documentation kit covers everything from intake procedures to ongoing supervision. This helps you establish a legally defensible approach to AI governance while managing risks appropriately. Establishing a Legal-Grade AI Governance Framework Image Source: Elevate Consult Legal teams need well-laid-out frameworks to govern AI systems in their organizations. Two frameworks provide complementary approaches that build a solid foundation for legal oversight of AI technologies. Aligning with ISO 42001 and NIST AI RMF ISO 42001 and NIST AI RMF serve as the life-blood for establishing legally defensible AI governance. ISO 42001 delivers a complete AI Management System (AIMS) with clear accountability structures and continuous improvement cycles. This framework provides top-down governance that grows with organizational AI programs. NIST AI RMF takes a practical, bottom-up approach through four core functions: govern, map, measure, and manage. Companies using both frameworks gain efficient global compliance and better readiness for new regulations. Research shows this integration makes governance simpler, improves operational resilience, and connects high-level oversight with practical AI deployment. Defining AI governance responsibilities for legal teams Legal departments handle several key roles in AI governance. They ensure compliance with new AI-specific regulations and standards like the EU AI Act, Colorado AI Act, and NIST AI RMF. Legal teams must also develop complete policies that cover: Data governance and privacy protection Intellectual property strategy and risk management AI vendor assessment and contract management Risk controls and human oversight protocols Legal teams protect intellectual property by filing patents for AI innovations, copyrighting AI-generated works, and establishing clear ownership rights. They also negotiate and manage licensing agreements for third-party data, algorithms, and software used in AI systems. Mapping AI governance principles to legal risk domains Legal AI governance needs core principles mapped to specific risk domains. Five core principles shape AI use: fairness, transparency, accountability, privacy, and human oversight. Each principle tackles specific legal risks: Fairness addresses discrimination and bias risks. Legal teams review datasets and test algorithms for discriminatory outcomes to alleviate potential liability. Transparency relates to disclosure and explainability requirements. Teams should maintain documentation of model logic and decision-making criteria to support legal defensibility. Accountability creates ownership for model outputs and ethical oversight, establishing clear lines of responsibility that legal teams can defend. Privacy protects personal data through encryption, pseudonymization, and access controls – critical areas for regulatory compliance. Human oversight lets humans override automated decisions, a requirement increasingly mandated by regulations like the EU AI Act. The MIT AI Risk Repository shows security and system limitations (26%), socioeconomic risks (19%), and discrimination risks (15%) represent the most common risk domains. Legal teams should focus their governance resources on these areas accordingly. A governance framework that blends these standards and principles helps legal departments become strategic advisors who shape their organization’s approach to AI, rather than just compliance guardians. Core Documentation Kit Components for Legal Teams Image Source: Fisher Phillips Legal teams need complete documentation to adapt AI governance to their organization’s needs. These core documents are the foundations of a defensible AI program that reduces risks while enabling state-of-the-art solutions. AI Governance and Use Policy Template The AI Governance Policy Template is the life-blood of any working AI governance program. This foundation document sets clear, enforceable guardrails around AI use across the organization. A working AI policy template should define roles and responsibilities, governance oversight mechanisms, and escalation procedures for AI-related concerns. Legal teams must address professional responsibility considerations in the policy. A well-laid-out template sets expectations for attorneys’ knowledge of AI tools and verification requirements for AI-generated outputs. Your policy should have these key sections: Purpose statement defining the overall goal and compliance commitments Competence requirements for legal professionals using AI tools Permitted and prohibited AI use cases with verification protocols Confidentiality and data security safeguards Compliance with jurisdictional regulations Monitoring and continuous improvement processes AI Risk Assessment Checklist for Legal Review Legal teams should use a structured approach to review AI systems before deployment. A complete AI risk assessment checklist helps spot potential legal vulnerabilities across multiple dimensions, from data privacy to output reliability. Legal reviewers should check these aspects: Algorithm bias and discrimination potential Data privacy compliance across jurisdictions Output verification processes and human oversight Intellectual property risks Documentation adequacy for regulatory compliance Risk levels determine assessment depth—customer service AI systems need deeper scrutiny than internal document summarization tools. The checklist should also include periodic reassessment since AI systems change faster than traditional software. AI Vendor Assessment Questionnaire Third-party AI vendors bring significant risks that legal teams must review carefully. In fact, IBM’s 2025 Cost of a Data Breach Report found that 13% of organizations reported breaches with AI models or applications, and 97% of these organizations lacked proper AI access controls. Your vendor questionnaire should go beyond basic due diligence to address AI-specific concerns. Vendors must explain how they handle: Training data provenance and rights Model behavior documentation and limitations Explainability tools and audit support API security and access controls Jurisdiction-specific compliance capabilities Service level agreements and fail-safe mechanisms Ask for specific evidence like model cards, security certifications (SOC 2 Type II, ISO 27001), and documented fallback
Integrating AI Governance Tools with MLOps Pipelines
A surprising fact: 85% of machine learning models never reach production. This reality expresses why AI governance tools have become vital components of modern ML pipelines. The global MLOps market hit US$1.58 billion in 2024 and will likely reach US$2.33 billion by 2025, with a compound annual growth rate of 35.5%. Many organizations don’t deal very well with implementing effective governance throughout their AI lifecycles. A well-laid-out MLOps infrastructure is a vital element that helps AI models move reliably from development to production while reducing failures. Enterprise AI governance tools also help tackle serious financial concerns. Data quality problems cost companies about US$12.9 million each year, while predictive system downtime costs an average of US$125,000 per hour. This piece explores the best AI governance tools for model orchestration and their integration with MLOps pipelines. You’ll learn why AI governance framework tools matter for ethical model development and how they support compliance workflows. AI incidents rose by 56.4% to 233 cases in 2024. A resilient AI model governance system isn’t optional anymore – it’s vital for building trustworthy AI systems. The text also covers ISO 42001 AI governance tools implementation strategies that will help you establish reliable, secure, and compliant ML operations. Understanding the Role of AI Governance in ML Pipelines Image Source: Medium AI governance stands as the life-blood of reliable machine learning operations. It embodies a detailed system of policies, processes, and tools that help develop, deploy, and monitor AI systems responsibly throughout their lifecycle. Organizations can balance innovation and risk management through this structured approach, which builds a foundation for ethical and compliant AI implementation. AI governance framework tools for ethical model development Ethical considerations are the foundations of effective AI governance frameworks. Research shows that organizations must make fairness a priority in model development. AI systems shouldn’t perpetuate or worsen biases or prejudices. Teams can detect and fix potential bias issues before models reach production using tools like AI Fairness 360 and Fairness Indicators. A reliable ethical AI framework has these vital components: Transparency mechanisms that make AI decisions understandable and explainable Accountability structures with clear ownership of AI outcomes Privacy and security controls that protect sensitive data throughout the AI lifecycle Human oversight protocols that maintain meaningful control over AI systems “Model Cards,” developed by companies like IBM, provide standardized documentation for transparency, capturing critical information about model development, training data, and limitations. These documentation tools help teams spot potential ethical concerns early in the development process. Enterprise AI governance tools for regulatory compliance Regulatory scrutiny continues to grow, and organizations need specialized tools to guide them through the complex compliance landscape. Companies can face fines up to EUR 35 million or 7% of their annual turnover for severe compliance violations under the EU AI Act. Enterprise-grade governance tools become vital for risk mitigation. Modern compliance tools offer automated assessment capabilities. Teams can identify regulatory obligations in frameworks like GDPR, NIST AI RMF, and the EU AI Act. These platforms change manual oversight processes into intelligent, scalable orchestration systems that blend with existing MLOps workflows. Enterprise compliance tools excel with centralized policy enforcement, regulatory updates, and automated documentation generation. Tools like watsonx.governance provide compliance accelerators—pre-built libraries of regulatory content that optimize the identification of applicable requirements for each AI use case. Why governance is critical in production ML environments Production environments create unique challenges that make governance vital. Models moving from development to deployment face increased risks of drift, bias amplification, and unexpected behavior. These issues can cause major financial, legal, and reputational damage without proper governance. Good governance in production requires continuous monitoring of model performance and behavior. Organizations maintain model quality over time with tools that track metrics related to fairness, accuracy, and data drift. These tools serve as early warning systems for potential issues before they impact business outcomes. Risk mitigation aside, production governance creates clear audit trails that show responsible AI practices to regulators, stakeholders, and customers. This visibility builds trust and provides key evidence during compliance audits or when model decisions come into question. Governance systems help cross-functional teams work together by creating structured collaboration frameworks that unite technical, legal, and business views. This collaborative approach keeps AI systems in line with organizational values and regulatory requirements throughout their operational lifetime. Key Challenges in Aligning Governance with MLOps Organizations face major hurdles when they implement AI governance. A newer study shows 56% of respondents call model governance implementation one of their biggest problems in deploying ML applications in production. These roadblocks stop organizations from getting full value from their AI investments. Lack of traceability in model lifecycle ML models evolve through development stages, making traceability a core challenge. Organizations find it hard to track changes to model code, data transformations, and machine learning pipelines without proper documentation frameworks. Teams can’t explain performance issues because they lack visibility, which creates serious accountability gaps. AI systems also need a unique, verifiable identity to prove their authenticity across systems. This missing element affects reproducibility and damages stakeholder trust. Teams end up with “black boxes” because they can’t track their models properly. They struggle to explain: Which training datasets influenced model behavior What preprocessing steps were applied to input data How hyperparameters were selected and optimized Who made critical decisions throughout development The traceability problem goes beyond technical documentation. Teams need structured methods to document business context, stakeholder information, and guidelines they use to reproduce models. Compliance gaps in continuous deployment workflows ML systems face unique compliance challenges with continuous deployment. Models can degrade over time unlike traditional software. This happens due to changing data patterns, user behavior shifts, or evolving external conditions. This issue, known as concept drift, needs special monitoring systems that standard CI/CD workflows often lack. Teams find it hard to automate compliance checks in deployment pipelines. Highly regulated industries must maintain detailed audit trails. They need to document every action, including commits, peer reviews, and staff involved in each deployment step. These requirements clash with the speed-focused nature of continuous
AI Risk Management Register: Categorization and Mitigation
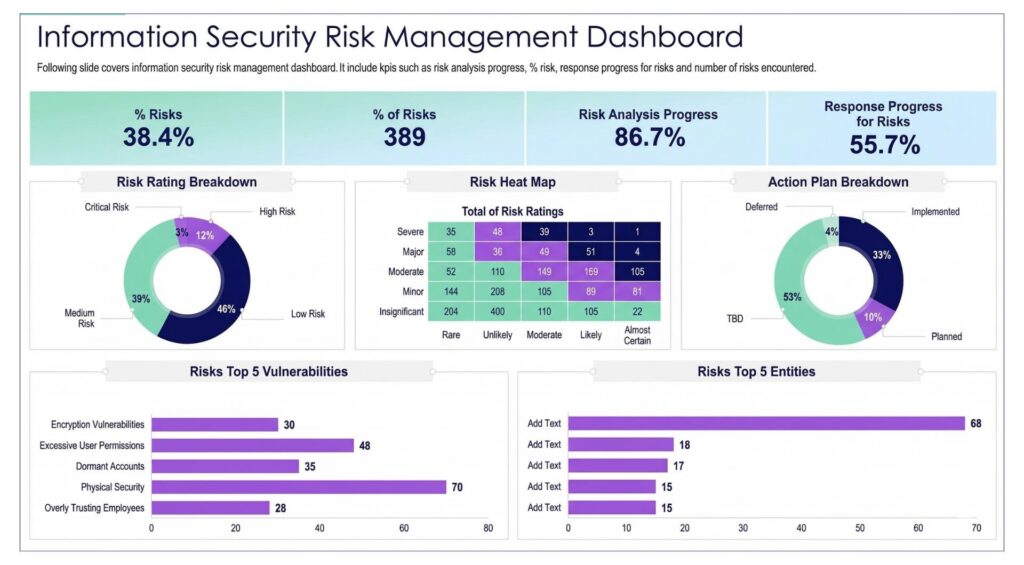
Companies are racing to boost their AI investments, with 92% planning increases over the next three years. The rush to adopt AI technology comes with significant risks – a fact acknowledged by 60% of S&P 500 companies. This gap between implementation and protection needs immediate attention. The AI market shows no signs of slowing down. Experts project a 60% year-over-year spending surge by 2025, pushing the market value to $480 billion in 2026. Research firm Gartner’s data suggests that companies will cancel 40% of emerging agentic AI projects by 2027, largely due to poor risk controls. The UK’s Center for Data Ethics and Innovation reveals an alarming trend – while 78% of public sector organizations use AI systems that directly affect service delivery, only 31% keep AI-specific risk registers. This piece will help you create and maintain a detailed AI risk management register. You’ll learn about core components, key risk categories to monitor, and steps to implement effective controls. The guidance will give you a practical framework to identify, categorize, and alleviate AI risks in your organization. Core Components of an AI Risk Management Register Image Source: Info-Tech A central AI risk management register is the life-blood of responsible AI governance. This living document tracks, rates, and manages all AI-related risks throughout an organization. The right implementation creates an early warning system that helps organizations find issues, assign who fixes what, track how well controls work, and show regulators and stakeholders they’re doing their due diligence. Risk ID, description, and categorization The foundation of any good AI risk register starts with clear identification and grouping. Each risk needs its own tracking ID. On top of that, it needs specific details: Clear risk description: You need precise explanations of what could go wrong instead of vague statements. Take this example: “Model may produce racially biased outputs due to underrepresentation in training data”. AI application specificity: Don’t just write “ChatGPT.” The register should say “ChatGPT-4 for generating external marketing blog posts” or “GitHub Copilot for Python code assistance in the R&D team”. Risk categorization: Standard groupings make classification consistent. Common risk types include performance risks (accuracy, drift), fairness and bias risks, privacy risks, security risks, legal/regulatory risks, and ethical/societal risks. Data sensitivity classification: This shows what kind of data the AI will work with – public, internal, confidential, or proprietary source code. Risk source identification: This shows how we found the risk – through model testing, internal audits, stakeholder feedback, or external rules like GDPR or the EU AI Act. Standard categorization lets organizations group similar threats and use consistent risk reduction strategies. The EU AI Act created a risk-based system that puts AI systems into four risk levels, each with different regulatory needs. The right classification determines everything from banned applications to documentation requirements. Higher risk levels need stricter compliance. Inherent vs residual risk scoring Risk scoring creates the register’s number-based foundation. You need to measure two key things: Inherent risk shows how much risk exists without any controls. This measures the baseline risk before any risk reduction efforts. NIST’s Risk Management Framework says you can estimate risk by multiplying how likely something is to happen by what it all means. Organizations typically calculate inherent risk using: Impact rating: High/Medium/Low or 1-5 scale Likelihood rating: High/Medium/Low or probability-based scoring Inherent risk score: Impact × Likelihood Residual risk measures the risk that stays after controls are factored in. This shows your organization’s real exposure after putting risk reduction strategies in place. This helps prove due diligence and risk acceptance decisions. The difference between inherent and residual risk scores shows how well your controls work. Jack Jones, who created the FAIR model, suggests a more practical way: treat inherent risk as the current risk level with existing controls, rather than imagining no controls exist. The residual risk would be whatever risk remains after adding more controls. Mapped controls and linked obligations The register must tie risks to specific controls and regulatory requirements. This connection ensures full coverage and regulatory compliance: Controls/mitigating actions: These are specific technical or procedural steps that reduce risk. Examples include differential privacy implementations, bias audits, model interpretability tools, and approval workflows. A draft AI Risk Mitigation Taxonomy lists four control types: governance and oversight controls, technical and security controls, operational process controls, and transparency and accountability controls. Linked obligations: Each risk needs mapping to applicable regulations and requirements. This mapping shows how risk reduction efforts support audit readiness and keeps risk management working with compliance needs. Risk owner assignment: The register must show who’s responsible for managing each risk, like the CISO, Data Science lead, or business unit manager. This responsibility ensures risks get proper attention and fixes. Target dates and status tracking: Setting deadlines and watching progress is vital for good risk management. The register should record the current status (open, mitigated, accepted) and when to review next. A detailed AI risk register connects every part of your risk management program. When all pieces work together, it changes from a static document into a useful tool that keeps improving AI governance. Organizations can see AI risk exposure across teams while staying in line with financial, operational, and reputation risk areas. AI-Specific Risk Categories to Track Image Source: AWS AI risk management needs specific tracking of risk categories unique to AI systems. Traditional IT risks don’t match the new challenges that AI brings, and we just need specialized ways to watch and reduce these risks. Algorithmic bias and fairness risks AI bias shows up in three main categories that need monitoring whatever the intent: Systemic bias exists in AI datasets, organizational norms, and broader societal contexts Computational and statistical bias comes from non-representative samples in AI datasets and algorithmic processes Human-cognitive bias comes from how people notice AI information or think about AI system functions These biases can speed up and scale the harm to individuals, groups, and organizations. AI systems’ discrimination isn’t always bias—sometimes AI results accurately reflect society’s existing patterns. In spite of that, fairness management
AI for Government: The Basics of Ethical Procurement
AI has reshaped the business world and changed how government agencies accomplish their missions. Artificial intelligence provides solutions to many public sector challenges by automating routine tasks, making better decisions, and cutting down risks. Artificial intelligence can reshape the scene of government operations if used ethically in procurement. AI systems can analyze large datasets to review suppliers based on cost, quality, and compliance. These systems predict demand trends and spot suspicious activities that might signal fraud. The training data’s existing societal biases can reflect and magnify in AI systems. The responsible use of AI in government needs careful review. The U.S. government must adopt these opportunities to stay competitive, while ensuring fairness, transparency, and accountability that protect public institution integrity. Public bodies want to achieve these goals by using procurement to set standards for ethical development and machine learning implementation in government. This piece outlines the key steps to ethically procure AI solutions for government use. We’ll explore AI’s role in public services and build internal capacity for responsible implementation. Step 1: Understand the Role of AI in Government Services Image Source: cef-see.org AI is reshaping how governments deliver services and meet public needs, even though adoption remains in early stages. A 2023 Bloomberg Philanthropies survey reveals that all but one of these local governments are learning about AI’s potential, while just 2% currently use it. Before making any procurement decisions, understanding how AI works in government settings is vital. How AI supports public sector goals Government agencies now see AI as a solution to maintain service levels while controlling costs, especially with tight budgets and staff shortages. AI-powered government operations could boost public administration productivity by up to 3% and increase real GDP by up to 4% by 2035. AI helps the public sector through several mechanisms: Operational efficiency: AI automates routine tasks so the core team can focus on higher-value work. Government employees who use AI save about 3.25 hours weekly. These time savings add up to major productivity gains across organizations. Better decision-making: AI analyzes large datasets to find patterns that help improve service delivery. To name just one example, 58% of cities are learning about generative AI for data analysis, while 76% use it for data-driven policymaking. Cost reduction: AI automation and targeted services could reduce fiscal deficits by up to 22% by 2035 compared to baseline projections. This includes efficiency savings and better compliance in areas like tax collection. Improved citizen experience: AI powers 24/7 self-service options that citizens now expect. Almost 98% of governments believe citizens prefer to interact through new technologies. Digital transformation has become essential to meet public expectations. Examples of AI in local government and federal agencies Local governments across America show tangible benefits from their AI solutions: Pittsburgh uses an AI-powered traffic management system that provides immediate analysis of key intersections. Traffic managers can adjust signals to optimize vehicle flow and reduce idle time. This supports the city’s goal to cut transportation emissions 50% by 2030. Phoenix created myPHX311, a web portal and app that answers common questions in Spanish and English. The system connects residents to city agencies for water service requests, graffiti reporting, and streetlight outage notifications. Washington, DC’s AI system helps city workers inspect 1,800 miles of sewer pipes. This automation cut reporting time from 75 minutes to just 10 minutes per hour of video inspection. Wilmington, Delaware used AI to send targeted ads on social media platforms that prompted residents to pay overdue bills. The city recovered $1.10 million in unpaid water bills while avoiding uncomfortable collection calls for employees. Federal agencies are adopting AI faster than ever. By December 2024, they reported over 1,700 AI use cases. The Department of Health and Human Services leads with 271 use cases. The Department of Homeland Security has added DHSChat, an internal agency chatbot, to its growing AI implementations. These agencies use AI for various purposes. The top three categories are mission-enabling internal support, health and medical applications, and government services including benefits delivery. Defense and intelligence agencies use AI for computer vision, graph analysis, and deep neural networks to spot suspicious activities in large datasets. AI brings the most value when organizations treat it as a foundation across departments rather than isolated pilot projects. Government organizations can tap into the full potential of AI by starting with quick wins while building momentum and investing in infrastructure, data quality, and workforce skills. Step 2: Identify Ethical Risks Before Procurement Image Source: SoluLab AI tool procurement needs more than just understanding their benefits. Government agencies must spot ethical risks that could break public trust and cause harm before signing contracts. We’ve seen what happens when these risks get ignored – just look at Google’s withdrawal from Project Maven in 2018 when employee protests over ethical issues blindsided their procurement process. Recognizing bias and fairness issues AI systems can copy and increase existing societal biases when trained on historical data. These algorithms become more than just math formulas in government settings – they turn into moral actors that affect citizens’ lives. Several cases show us these risks clearly: The COMPAS recidivism algorithm unfairly labeled Black defendants as high-risk, which raised serious questions about fair sentencing Detroit police wrongfully arrested a Black man in 2020 because of bad facial recognition matches. This showed how the technology makes more mistakes with people of color A healthcare algorithm didn’t properly assess Black patients’ needs because it looked at costs instead of actual health outcomes Bias can sneak into AI systems in many ways. It happens through training on skewed data, choosing efficiency over fairness, and feedback loops that keep disadvantages going. What’s fair isn’t simple either – different situations need different fairness measures, and you can’t satisfy all of them at once. Agencies should use structured frameworks like NIST’s AI Risk Management Framework to deal with these issues. They also need review councils to check high-impact systems before launch and development teams that bring different viewpoints to the table. Assessing data quality
How to Map FedRAMP / ISO to the NIST AI Risk Management Framework
The NIST AI Risk Management Framework marks a defining moment in AI governance. It stands as the first detailed, government-backed approach to managing artificial intelligence risks. This voluntary, non-certifiable framework emerged in January 2023. It guides organizations to design, develop, implement, and use AI systems responsibly throughout their operations. The framework provides essential guidance for organizations navigating AI governance complexities, specifically designed to meet the 2023 U.S. Presidential Executive Order on safe AI use. Organizations often already follow decades-old frameworks like FedRAMP or ISO standards. Multi-framework compliance offers a quick way to cover multiple frameworks at once. This strategy brings clear advantages. It saves time and reduces audit fatigue. The approach minimizes duplicate work and helps build a stronger, more consistent security posture. The NIST AI RMF Core features four key functions—Govern, Map, Measure, and Manage. These functions can map effectively to existing frameworks and create a unified compliance strategy. Let’s explore ways to arrange the NIST AI Risk Management Framework with FedRAMP and ISO standards. You’ll find practical guidance to create crosswalks between these frameworks and identify shared controls. This unified approach addresses AI-specific risks throughout the technology lifecycle. The result? A clear roadmap that integrates these frameworks efficiently while ensuring detailed AI risk management. Understanding the NIST AI Risk Management Framework NIST released its AI Risk Management Framework (AI RMF) on January 26, 2023. This marked a key milestone in AI technology governance. The framework came together through teamwork. People shared comments, joined workshops, and gave their input. The result was a complete way to manage AI risks. What is NIST AI RMF and why it matters The NIST AI RMF helps organizations handle risks in AI systems throughout their life. The framework shows teams how to build trust into AI products, services, and systems right from design to evaluation. AI technologies keep changing the digital world at breakneck speed. They bring new risks about being open, fair, private, and secure. The NIST AI RMF gives everyone the same language and method to handle these risks. This creates a foundation that lets innovation grow responsibly. The framework stands on four main functions that work together: Govern: Sets up leadership oversight, organizational policies, and accountability culture Map: Spots context, needs, and risks in AI systems Measure: Creates ways to check performance and risk levels Manage: Puts controls in place to reduce risks and keeps watch These functions help organizations create AI systems that work well, stay safe, and bounce back from problems. Voluntary nature and non-certifiable status The NIST AI RMF is not mandatory. Organizations can pick and choose what works for them. This flexibility makes sense because AI gets used in many different ways. You won’t find a NIST-recognized certification process here. Unlike ISO 42001, which can certify your management system, the NIST AI RMF just gives advice. Many teams start with this framework before moving to certified standards. The framework may be optional, but its complete approach has caught on worldwide. Teams beyond U.S. federal agencies – in the UK, US, and other countries – now use it to spot and reduce AI risks better. How it complements NIST SP 800-37 The NIST AI RMF fits with other NIST risk tools. It builds on NIST Special Publication 800-37, which lays out the Risk Management Framework (RMF) for information systems. NIST SP 800-37 has seven steps: Prepare, Categorize, Select, Implement, Assess, Authorize, and Monitor. This process focuses on keeping regular information systems safe and matches the Federal Information Security Management Act (FISMA). The AI RMF tackles AI-specific challenges head-on. AI system security ties closely to IT infrastructure security. Teams can use both frameworks at once. NIST has created overlays where AI meets cybersecurity. These give AI users and developers a starting point for security, though they’re optional. Teams can take what they need from the AI RMF Playbook and Control Overlays based on their industry. The NIST AI RMF adds to current risk management by showing how to handle AI’s ethical, technical, and social effects from start to finish. Overview of ISO 42001 and FedRAMP Frameworks You need to understand each standard’s purpose and scope to map AI governance frameworks properly. Organizations must know how ISO 42001 and FedRAMP work as separate yet potentially complementary systems to match them with the NIST AI Risk Management Framework. ISO 42001: AI Management System Standard ISO/IEC 42001:2023 is the first international standard for Artificial Intelligence Management Systems (AIMS). This new standard came out in December 2023 and offers a well-laid-out method for organizations that create, provide, or use AI systems. The standard gives organizations a complete framework to set up, run, maintain, and improve their AI governance. It includes rules about risk management, AI system effect assessment, system lifecycle management, and oversight of third-party suppliers. ISO 42001 uses a Plan-Do-Check-Act method that helps organizations: Set up AI governance policies and practices Run responsible development procedures Track performance against set metrics Keep improving AI management processes This standard tackles key AI issues like transparency, accountability, fairness/bias, security/safety, and privacy. Organizations that use ISO 42001 must follow 38 specific controls split into 9 control objectives. Unlike the NIST AI RMF, you can get certified in ISO 42001. Organizations go through several audit stages including document review, operational assessment, and checking how well they’ve implemented everything. Once approved, certificates last three years with yearly check-ups. FedRAMP: Cloud Security Authorization Program The Federal Risk and Authorization Management Program (FedRAMP) takes a different approach to technology governance. This 12-year-old program offers a standard, government-wide system for U.S. federal agencies to adopt secure cloud services. FedRAMP uses NIST 800-53 security controls but adapts them for cloud environments with extra rules for constant monitoring and risk assessment. The program lets multiple federal agencies use a single Authorization to Operate (ATO), following a “do once, use many times” approach. Organizations seeking FedRAMP authorization must: Prepare System Security Plan (SSP) documentation Complete a full security assessment by a third-party assessment organization (3PAO) Get authorization from their sponsoring agency Monitor
Designing the AI Governance Operating Model & RACI
An AI governance operating model turns AI from a source of unmanaged risk into a capability the business can scale with confidence, and a clear RACI matrix is what makes ownership unambiguous across the AI lifecycle. The need is not theoretical: in McKinsey’s most recent State of AI survey, 88 percent of organizations reported using AI in at least one business function, up from 78 percent a year earlier, yet most remain stuck in piloting rather than scaling. That distance between fast adoption and disciplined AI governance is exactly where an operating model earns its keep. This guide walks through designing that operating model with the RACI framework, short for Responsible, Accountable, Consulted, and Informed. It covers how to assess your governance gaps first, build role-based ownership across legal, data, and engineering, operationalize approvals and escalation in day-to-day workflows, and keep the structure durable as models and regulations change. Assessing AI Governance Gaps Before Designing RACI “AI safety requires AI governance, and the dirty secret in the AI industry is that the weakest link in AI governance is data pipelines.” — Bjorn Reynolds, CEO of Safeguard Global, expert in AI data governance and security Most organizations underestimate how much AI is already in use. Surfacing shadow AI, the tools employees adopt without approval, is the starting point, followed by a structured inventory that records every model in use, its purpose, owner, and the data it touches. Building that inventory is widely regarded as one of the first and most important steps in standing up a governance program, and it is the same discipline Elevate applies when scoping AI assets for risk management. Evaluate governance maturity against a framework Once you know what you have, measure maturity against an established framework rather than an internal opinion. The NIST AI Risk Management Framework offers a structured way to identify, measure, and manage AI risk, and maturity is often described in stages that run from reactive, where teams handle problems as they surface, to proactive and then transformative. If you are choosing between frameworks, it helps to see how the main options compare against one another before committing. Identify compliance blind spots Many AI programs carry predictable blind spots: no continuous monitoring, thin audit trails, and risk reviews that check technical accuracy but skip ethical, societal, and regulatory impact. Closing these gaps before you design the RACI gives the matrix something real to govern, rather than formalizing ownership over a process no one fully understands. Designing a Role-Based AI Governance Framework Effective AI governance is cross-functional by design. The programs that work pull in privacy, IT, security, legal, compliance, data science, and product, because no single function can see the full risk surface of an AI system on its own. Stand up a Responsible AI committee A dedicated AI governance committee is the engine of oversight. It brings together legal, IT, security, human resources, compliance, data science, and management to oversee implementation, monitoring, and auditing. In a mid-sized organization, engineering leadership typically owns strategy, security and compliance assess risk, data science supplies technical depth, legal handles regulatory alignment, and product ties the work to business goals. Sector-specific contexts may also need their own policies, such as a dedicated AI policy for universities. Assign roles across legal, data, and engineering Clear titles prevent gaps. Core positions worth defining include a Chief Data and Analytics Officer or Chief AI Officer who champions governance as business strategy, data and AI stewards who own quality, metadata, and lineage, AI ethics officers who oversee responsible use, and model owners who remain accountable for performance and incidents. The Chief AI Officer role itself has emerged quickly as organizations centralize this accountability, and legal teams play an outsized part in making sure AI systems meet data protection and ethical obligations. Use RACI to define model ownership The RACI matrix clarifies who does what for every AI activity, from data preprocessing to model training to deployment approval. Unclear ownership is one of the most common reasons projects stall, which is why each activity should map to the four roles below. Role What it means in AI governance R – Responsible Performs the work or makes the decision, such as preparing data or training the model. There can be more than one. A – Accountable Owns the outcome and signs off. There should be exactly one named person per activity to avoid diffused responsibility. C – Consulted Provides input through two-way dialogue, such as domain specialists, security, or legal advisors. I – Informed Kept up to date on progress through one-way communication, such as executives or clients. Applied across the lifecycle, a simplified matrix might look like the illustrative example below, which organizations adapt to their own roles and risk tolerance. Activity CDAO / CAIO Model Owner Ethics & Legal Executives Set AI policy A C R I Build and train model I R C I Validate and bias-test A R C I Approve deployment A R C I Monitor in production A R C I Want a RACI built around your actual roles? Elevate helps teams map AI governance ownership across legal, data, and engineering, then turn it into approval and escalation workflows that hold up under audit. Book a readiness meeting Operationalizing RACI in AI Workflows “Think of AI as a sports car: the engine is powerful, but without brakes and steering, it’s a liability. AI governance isn’t about slowing down progress—it’s what enables us to move faster, with confidence.” — Christina Fung, SVP and Head of Global AI Enablement Center of Excellence at CGI, AI governance leader A matrix on a slide changes nothing. The value appears when those roles are wired into the workflows teams use every day. Approval workflows for model deployment Two things should require approval before going live: the model itself and its deployment endpoint. Most mature teams require models to pass quality checks, bias assessments, and feature-importance tests, and many automate this with MLOps pipelines that compare artifacts against set thresholds, update model status, and alert a named approver when a
7 AI Governance Best Practices for Enterprise AI Teams
Trust in artificial intelligence remains alarmingly low among enterprises that need AI governance best practices. A Harvard Business Review study reveals that only 28% of U.S. online adults trust companies using AI models with their data, while 46% explicitly state they don’t. AI systems now make decisions that affect customers, employees, and society at large, which raises the stakes significantly. Enterprise AI governance serves as the foundation of policies, processes, and controls that ensure responsible, compliant, and secure use of artificial intelligence throughout an organization. The regulatory landscape continues to evolve rapidly. More than 75 countries have adopted or started drafting AI legislation as of July 2025, making a structured governance approach essential. Organizations face serious risks when AI lacks proper governance. Bias and discrimination can creep into critical areas like hiring, lending, and healthcare decisions. This piece explores seven proven AI governance best practices that help enterprises build responsible AI systems while meeting emerging regulations. These practices represent the life-blood of successful enterprise AI governance and will help your teams direct through the complex world of AI implementation. Establish Ownership and Governance Structure AI governance success depends on clear ownership. Companies of all sizes don’t deal very well with AI accountability. Multiple departments want partial ownership, but no one takes full responsibility to keep systems safe, ethical, and compliant. Companies need formal governance structures with clear roles and responsibilities to tackle this challenge. Create AI governance board with cross-functional leads Smart companies set up dedicated AI governance bodies that include people from every department. These teams bring together different viewpoints needed for complete oversight. Good AI governance needs cooperation between: Technical experts who know model architecture Legal and compliance officers for regulatory guidance Business leaders who understand operational effects Ethics specialists to review fairness concerns Security professionals to handle vulnerabilities Recent studies show companies with effective cross-functional AI governance teams deploy AI 40% faster and face 60% fewer compliance issues after deployment compared to companies using siloed approaches. All the same, 67% of companies still have trouble with cross-functional cooperation in AI contexts. The governance board needs executive backing and authority to enforce policies when needed. It also needs to create standard procedures, look at high-risk projects, and update policies based on what they learn. Proper resources help prevent the governance team from slowing down breakthroughs. Assign model owners and AI champions in each unit Companies must pick specific roles within business units beyond the main governance team. The old saying rings true: “you can’t govern what no one owns”. Model owners take charge of performance and maintenance throughout the AI lifecycle. They handle everything from design to deployment to retirement, including retraining schedules, drift monitoring, and keeping inputs relevant. Companies benefit when they choose AI champions in each business unit to connect technical teams with business stakeholders. These champions help turn governance requirements into practical steps while making sure AI projects line up with business goals. These formal governance roles create better accountability: AI Product Owner Data Product Owner AI Risk Officer Ethics or Compliance Officer Federated Domain Stewards New AI projects need approval workflows involving these roles. This ensures every AI project gets proper technical, ethical, and business review. Risk ownership throughout the AI lifecycle needs clear definition. To name just one example, the privacy team might handle data collection and consent, while security takes over during model deployment, and legal leads regulatory validation. This removes confusion and lets experts handle their specific risks. Use a RACI matrix to clarify responsibilities Many companies now use frameworks like the NIST AI Risk Management Framework to guide their governance. A RACI (Responsible, Accountable, Consulted, Informed) matrix helps implement these frameworks without confusion or operational standstills. A well-laid-out RACI matrix shows which leaders should be responsible, accountable, consulted, and informed for each governance framework activity: govern, map, measure, and manage. This clarity becomes crucial during key decisions. When data science deploys a model without proper audit trails, the RACI matrix tells whether the MLOps team, compliance officer, or business unit owner can step in. Only 25% of boards have added AI oversight to their committee charters. Board committees need to expand their duties to include AI governance practices. This exercise helps boards avoid gaps and overlaps in AI oversight while using their committees’ focus, expertise, and time better. Companies need a clear process to raise, sort, and fix cross-functional issues. If someone spots a privacy risk during model testing, the system should automatically alert both security and legal teams for joint review. These escalation paths need preset timeframes and tracking to prevent issues from getting lost. Clear ownership through governance boards, model owners, and detailed RACI matrices gives companies the structure they need for responsible AI development and use. Map and Classify Data for AI Use Data governance is the foundation of responsible AI systems. AI technologies have advanced, but companies still need a reliable map of their data’s journey through LLM workflows. Learning about what data your AI systems can access and how to classify this information should be your first step to create reliable governance practices. Label data by sensitivity and legal constraints Data mapping connects fields across systems and keeps accuracy and meaning intact as data moves, integrates, or changes. Companies need this to comply with privacy regulations like GDPR, HIPAA, and CCPA because it shows where data exists, how it flows, and what happens to it. Your AI data classification should organize information into these clear sensitivity tiers: Public Data: Information safe for public access (marketing materials, website content) Internal Data: Organizational information intended only for internal use (company policies) Confidential Data: Private information requiring security controls (customer information, business contracts) Highly Confidential Data: The most sensitive information that could cause significant damage if leaked (trade secrets, financial transactions) AI systems need more sophisticated classification approaches than traditional data governance. AI-powered classification tools understand context and intent—they don’t just look for patterns or keywords but grasp how data fits into the bigger picture. These systems
When to Engage AI Governance Consulting for Program Rollout
Companies spend $30 to $40 billion on AI initiatives, yet 95% of them see no returns on their investment. This reality shows a big gap between adopting AI and making it work effectively. AI governance consulting helps businesses overcome these challenges and deliver real results. The numbers tell an interesting story. About 52% of organizations are rushing to adopt Generative AI, and 76% of leaders believe AI will change everything within three years. But many hit roadblocks with execution. The problem is clear – businesses want to implement AI solutions but lack proper governance frameworks. Timing plays a vital role when companies compare AI governance consulting prices and look for the best business partners. Understanding what AI governance consulting includes helps teams pick from consulting firms of all sizes that offer expert guidance. This piece dives into the right time to bring in external governance experts and ways to check your company’s readiness. You’ll learn where consulting adds the most value, different pricing options, and tips to find your ideal partner. The main focus remains simple – to help you get better returns on AI investments through solid governance. Identifying the Right Time to Engage AI Governance Consulting Organizations struggle to find the right time to bring in external AI governance expertise. The timing can affect both implementation success and return on investment by a lot. A smart approach to scheduling your AI governance consulting can determine whether your AI delivers value or just stagnles. Early-stage AI strategy development Getting governance consultants during the original strategy planning helps organizations avoid costly mistakes. Research shows that 80% of AI projects fail because companies rush to implement technology without proper planning. Consultants offer vital guidance by helping organizations: Line up AI initiatives with business goals before major investments Build a responsible AI framework that balances breakthroughs with risk management Review your current technology stack, data quality, and team skills to check AI readiness Organizations still developing their AI maturity model benefit the most from early consultation. McKinsey’s research shows that connecting digital strategies with AI strategies leads to clearer policies on data security and accountability. Getting governance expertise at this stage creates guardrails that keep security intact without stopping innovation. Post-pilot phase with scaling challenges Moving from successful pilot to enterprise-wide implementation is another key moment to get consulting help. Companies often run into pattern recognition problems that stop them from scaling. A consumer packaged goods company started by using AI in customer service but found greater gains when they spotted similar patterns across multiple business functions. On top of that, only 18% of organizations have enterprise-wide councils that can make decisions on responsible AI governance. This creates a big gap in scaling oversight. Governance consultants help spot technical roadblocks, data quality problems, and organizational barriers early. This prevents expensive mistakes that could derail projects months into implementation. Their expertise becomes essential to create policies for consistent governance in a variety of AI applications. Regulatory or compliance-driven triggers New regulations often push organizations to seek governance expertise. The EU Artificial Intelligence Act, coming in 2026, could fine companies up to €35 million or 7% of global revenue for breaking rules. New York City’s AI bias audit requirements for hiring tools also create urgent compliance needs. The numbers show why this matters: 95% of leaders think their business will face impacts from proposed EU regulations. More than 80% of organizations plan to spend at least 10% of their AI budget on meeting regulatory requirements. Organizations facing these triggers should focus on: Building automated compliance frameworks that adapt to regulatory changes Creating AI-specific risk management approaches Setting documentation standards that prove compliance Only 2% of companies say they’ve fully implemented responsible AI across their organization. Getting consultants when regulatory pressures first appear helps organizations stay ahead instead of playing catch-up with compliance requirements. Your organization’s specific situation determines when to get AI governance consulting—whether you’re creating your original strategy, scaling successful pilots, or handling regulatory pressures. Knowing these triggers helps you intervene at the right time to maximize AI’s value while reducing potential risks. Assessing Internal Readiness Before Consulting Engagement Image Source: Elevate Consult Companies need a full picture of their needs before they invest in AI governance consulting services. This self-evaluation helps them spot specific needs and pick areas to improve. They can then get more value from their consulting partnerships. Recent data from the Thomson Reuters Foundation’s AI Company Data Initiative shows that only 48% of companies have reliable governance frameworks to handle AI-related risks. AI maturity model evaluation Maturity models give organizations a way to review their AI governance capabilities. These evaluations help organizations set their current position against industry standards. They use established frameworks like the NIST AI Risk Management Framework as their foundation. Most maturity models show growth through these stages: Initial/Reactive: No documented governance practices or just random approaches Defined/Proactive: Company-wide standard practices with proper documentation Managed/Optimized: Practices run smoothly with constant monitoring and improvements A proper assessment needs detailed records and proof-based reviews. Teams should include members who know their stuff from different departments to gather reliable information. The knowledge gap remains wide. Only 14% of smaller companies know about major standards like the NIST AI Risk Management Framework. to see where your company stands and what steps you need to take next. Existing governance structures and gaps Many organizations still have big holes in their governance despite having AI strategies. Numbers tell an interesting story. While 76% of companies with an AI strategy have management oversight, only 41% make their policies available to employees. This gap between what’s on paper and what happens creates weak spots in how governance works. Your review of existing structures should look at: Policy framework and ethical standards Roles and responsibilities definition Risk and compliance programs Architecture and standardized tools AI model management processes Observability and monitoring capabilities The numbers raise concerns. About 48% of companies don’t watch their AI systems for accuracy, drift, or misuse—simple practices needed for safe