PRIVACY COMPLIANCE · INTERNATIONAL
International Data Privacy Compliance
Multi-Jurisdiction Programs for Global Organizations
Data privacy law is no longer a European question with local footnotes. More than twenty US states now have comprehensive privacy statutes, the UK regime diverged from the EU in February 2026, and jurisdictions across Asia, Latin America, the Middle East and Africa have enacted or amended frameworks of their own. Running a separate program per country does not scale. Elevate Consult builds one control set mapped across the regimes an organization actually operates in, so evidence is produced once and answers many.
2026 UPDATE
Why a single-jurisdiction program stopped working
The EU and UK regimes split
The Data (Use and Access) Act 2025 amended the UK GDPR with main provisions in force from 5 February 2026 and a statutory complaints duty from 19 June 2026. Cookies, automated decision-making and subject access now differ. Organizations that maintained one European program are non-compliant in one of the two jurisdictions on at least one point.
The US patchwork outgrew the CCPA comparison
California, Virginia, Colorado and Utah are no longer a representative list. More than twenty states now have comprehensive privacy statutes with differing thresholds, rights, cure periods and enforcement models, and California added a dedicated enforcement agency and automated decision-making regulations that no other state matches.
Transfer mechanisms remain contingent
The EU-US Data Privacy Framework survived the Latombe challenge at the General Court on 3 September 2025 and is under appeal at the Court of Justice. UK adequacy was renewed in June 2025 for four years. Both are dependencies with expiry or reversal risk, which is why Standard Contractual Clauses stay in place as a fallback rather than being retired.
Convergence is real at the principle level
Most regimes share the same core:
informed consent or a lawful basis, purpose limitation, individual rights, security of processing and breach notification. The divergence sits in thresholds, timelines, definitions and enforcement. That is what makes a mapped control set viable and a copied program dangerous.
WHAT IT IS
One program, mapped across regimes
An international privacy program is not the sum of national programs. It is a single set of controls, a single data inventory and a single evidence structure, with jurisdiction-specific configuration where the law actually requires different handling.
The work is deciding where configuration is required and where it is not. Cookie consent requires per-jurisdiction configuration. A records of processing inventory does not. Getting that boundary wrong produces either a program that cannot scale or one that fails in a specific market.
THE COST OF GETTING IT WRONG
Fines are the visible consequence, not the largest one
Regulatory penalties reach 20 million euros or 4 percent of global annual turnover under the EU GDPR, with comparable ceilings elsewhere. Beyond fines, non-compliance produces litigation and class action exposure, loss of customer trust that rarely recovers, and operational restrictions including bans on data transfers or limits on operating in a jurisdiction. The commercial consequence arrives earlier than the regulatory one. Enterprise procurement and third-party risk reviews increasingly ask for evidence of privacy governance, and an organization that cannot produce it loses the deal before any regulator is involved.
Europe
EU GDPR, UK GDPR and DUAA 2025
The EU GDPR governs processing of EU residents’ data regardless of where the organization sits. The UK operates the UK GDPR with the Data Protection Act 2018, amended by the Data (Use and Access) Act 2025, which introduced divergence from February 2026.
United States
State comprehensive privacy statutes
More than twenty states now have comprehensive laws with differing thresholds, rights and enforcement. California is the outlier: a dedicated enforcement agency, six consumer rights, and automated decision-making regulations phasing into 2027.
Latin America
Brazil LGPD and regional frameworks
The LGPD follows GDPR structure with its own authority and enforcement posture. Several regional regimes have been enacted or amended, each with its own registration, transfer and breach requirements.
Asia Pacific
Japan APPI, and regional regimes
Frameworks vary widely in consent model, cross-border transfer mechanics and breach timelines. Assume differences rather than mapping everything to a GDPR baseline.
Middle East and Africa
National and free zone regimes
Several jurisdictions operate national data protection laws alongside separate free zone frameworks, which means a single legal entity can face two regimes in one country.
Sector overlays
Sector rules on top of national law
Financial services, health, education and government contracting each add obligations above the general privacy statute, and those are usually where the tighter timelines live.
OUR APPROACH
Assess, map, implement, sustain
Elevate builds repeatable processes rather than single-jurisdiction projects, because the regulatory map will change again and a program built to one statute has to be rebuilt each time it does
Initial assessment and gap analysis
Evaluate current practice across the jurisdictions the organization actually operates in, identify gaps per regime, and recommend a prioritized path rather than a per-country project list.
Control implementation
Design and enforce policies, procedures and tooling that satisfy the common core once, with jurisdiction-specific configuration only where the law requires it.
Incident response and breach management
Establish protocols that meet the tightest applicable notification timeline rather than the average one, with jurisdiction-specific decision trees.
Training and awareness
Role-based training that reaches the teams where privacy decisions are actually made: product, marketing, engineering, HR and support.
Key personnel appointments
Designate data protection officers, privacy officers and EU or UK representatives where a jurisdiction requires them.
Data mapping and inventory
Catalogue personal data flows and processing activities to produce a single view of the data ecosystem that every regime’s records requirement can draw from.
Security of processing
Address the technical and organizational measures every regime requires, aligned with ISO 27001, ISO 27701 and SOC 2 so security evidence serves both the privacy and security programs.
Third-party risk management
Assess vendor and subprocessor risk, establish contractual safeguards, and monitor on a cadence rather than at onboarding only.
Documentation and records
Build the record structure that supports audit and regulator inquiry across regimes, so evidence is produced once.
Continuous monitoring
Regular review as regimes change, because they will. The 2026 UK divergence and the California ADMT regulations are recent examples rather than exceptions.
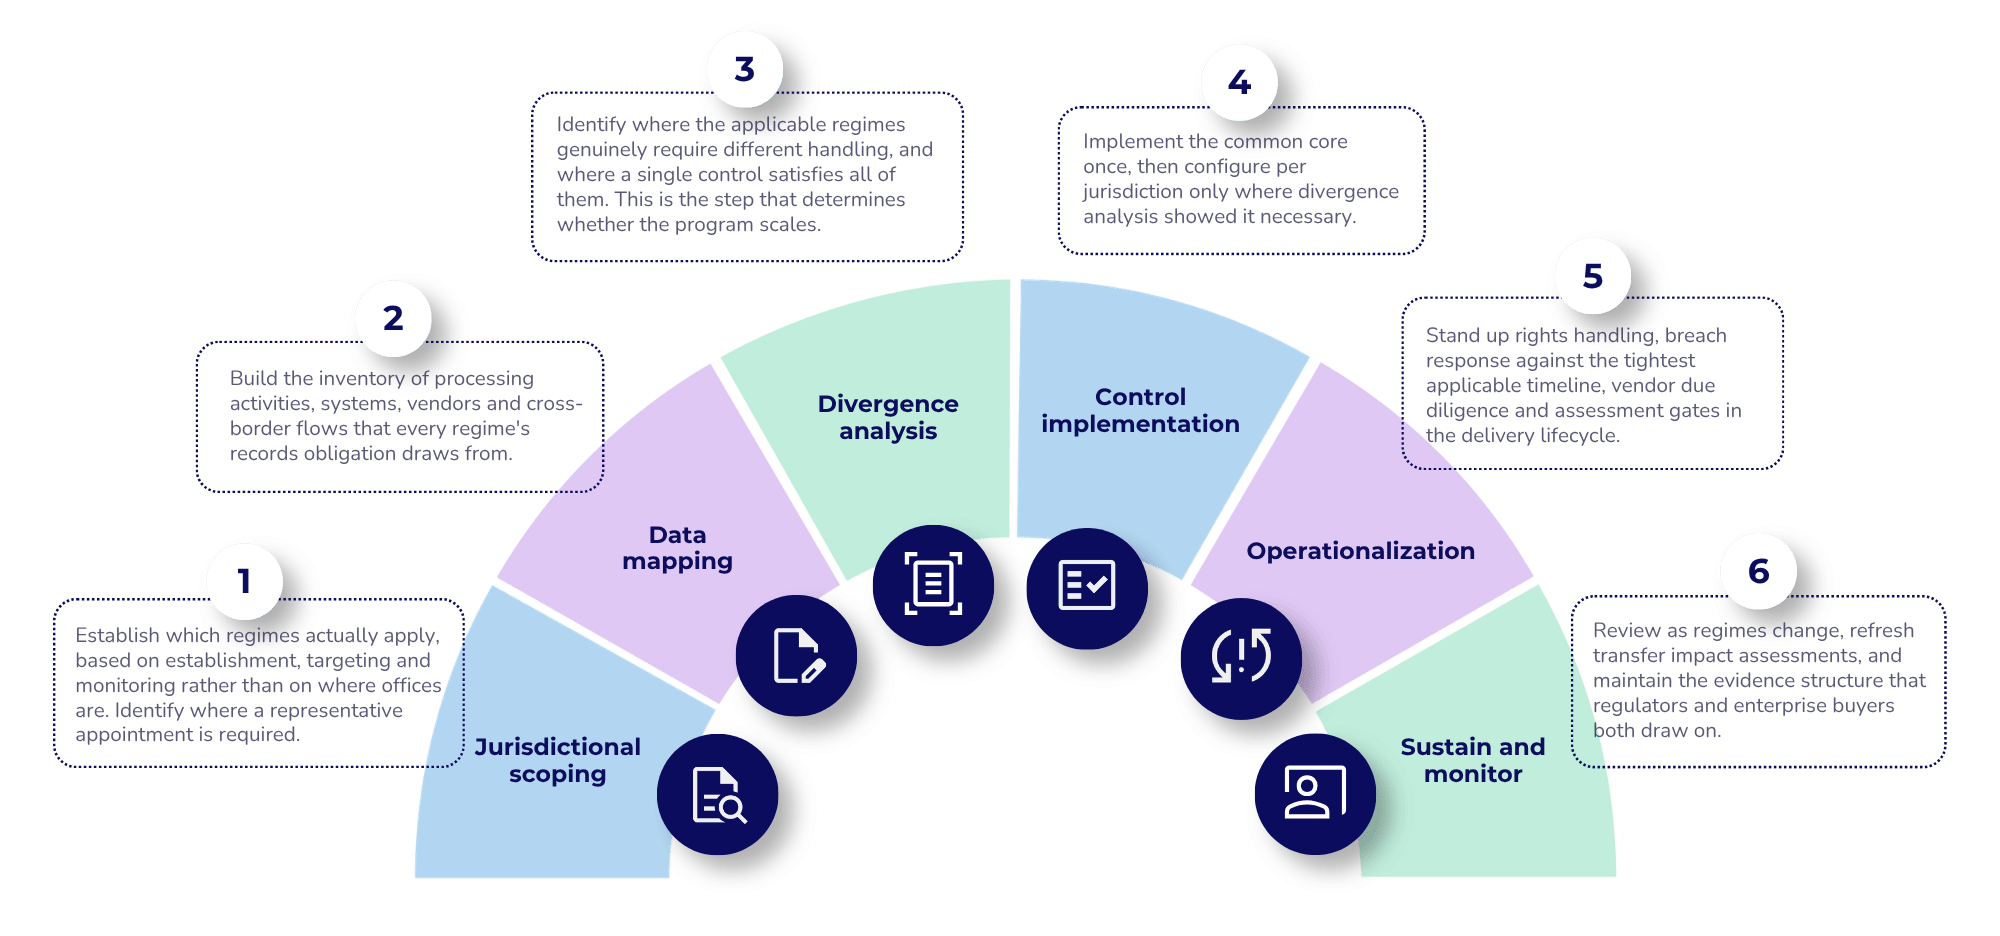
ENGAGEMENT PHASES
How the work runs
WHO THIS IS FOR
Roles Elevate works with on this standard
GET STARTED
Ready to build one program across your jurisdictions?
Whether the driver is expansion into a new market, a divergence that broke an existing program, or an enterprise buyer asking for evidence, Elevate Consult scopes the applicable regimes, maps the controls once and builds the records structure that serves all of them.
FAQ
Common Questions
Do we need a separate privacy program for each country?
No, and building one is the most common and most expensive mistake. Most regimes share a common core: a lawful basis or informed consent, purpose limitation, individual rights, security of processing and breach notification. Build that once, then configure per jurisdiction only where the law genuinely diverges, such as cookie consent, breach timelines and automated decision-making.
Are EU GDPR and UK GDPR still interchangeable?
No. The Data (Use and Access) Act 2025 amended the UK regime with main provisions in force from 5 February 2026 and a statutory complaints duty from 19 June 2026. Cookies, automated decision-making, subject access and lawful bases now differ. Organizations serving both markets need jurisdiction-aware configuration in at least those areas.
How do we handle international data transfers?
Through a recognized mechanism plus a transfer impact assessment: Standard Contractual Clauses for the EU, the International Data Transfer Agreement or Addendum for the UK, or an adequacy decision where one exists. The EU-US Data Privacy Framework is valid but under appeal at the Court of Justice, and UK adequacy was renewed in June 2025 for four years. Both are dependencies, so keep SCCs available as a fallback.
Which US states have comprehensive privacy laws?
More than twenty now do, and the list grows each legislative session. Naming Virginia, Colorado and Utah as the followers to California describes 2021 rather than the current position. Thresholds, consumer rights, cure periods and enforcement models differ between them, and California is the only state with a dedicated privacy enforcement agency.
What triggers a data protection officer appointmen
It varies. Under the EU and UK GDPR the triggers are public authority status, large-scale regular and systematic monitoring, or large-scale special category processing. Other regimes use different tests, and some require a local representative separately from a DPO. Assess each applicable regime rather than assuming one appointment covers all of them.
Where do most international programs fail?
At the inventory. A program can have strong policies and still be unable to answer where a data category lives, which vendor processes it, and under which transfer mechanism it leaves the jurisdiction. Every downstream obligation, from rights handling to breach notification to transfer assessment, depends on that inventory being accurate and current.