Cybersecurity and Compliance for Law Firms
Client Confidentiality, Outside Counsel Guidelines and AI in Legal Practice
Law firms hold the most sensitive material their clients produce, concentrated in one place, protected by a duty that predates every cybersecurity framework. That combination is why attackers target the sector and why corporate clients now impose security requirements through outside counsel guidelines and client audits rather than trusting professional obligation alone. Elevate Consult builds the security and privacy programme that satisfies those guidelines, plus the AI governance that legal practice now requires.
UPDATE
What is driving security investment in the sector
Clients audit their firms now
Large corporate clients impose security requirements contractually through outside counsel guidelines, and increasingly verify them. Firms serving healthcare clients sign business associate agreements; firms serving financial institutions inherit GLBA-related expectations; firms serving regulated industries inherit whatever their client is subject to.
Generative AI entered legal practice faster than policy did
Drafting, review, research and discovery tools process privileged material. The governance questions are concrete: where does the data go, is it used for training, who can see the output, and what happens when the tool is wrong in a filing.
The professional duty is not a security programme
Confidentiality obligations create the duty. They do not create the controls, the evidence or the incident response capability a client audit will test. The gap between the two is what firms are now being asked to close.
Privacy obligations reach firms directly
Firms process personal data as controllers for their own operations and as processors for client matters. The CCPA and the state patchwork, the GDPR where EU individuals are involved, and Spain's LOPDGDD where Spanish operations exist all apply to the firm itself.
WHO WE HELP
Firms and in-house legal functions
Law firms of all sizes, in-house legal departments, legal service providers and e-discovery vendors, and alternative legal service organizations.
The sector’s risk profile is driven by concentration. A single firm holds the merger documents, the litigation strategy, the regulatory correspondence and the personal data of many clients at once, which makes it a more efficient target than any of those clients individually.
WHAT CLIENTS ASK FOR
The frameworks that appear in outside counsel guidelines
Client security requirements converge on a small number of recognizable artifacts, because a general counsel’s office needs something it can verify rather than a description of good intentions.
An accredited certificate against the 2022 edition. The 2013 edition transition closed on 31 October 2025, so a firm presenting an older certificate has a problem to fix before its next client audit.
ISO 27001
An attestation covering security and, where relevant, confidentiality and availability. Frequently specified alongside or instead of ISO 27001 depending on where the client sits.
SOC 2
Most firms below the largest tier have no dedicated security function, and outside counsel guidelines increasingly ask who owns security. A named, accountable function answers that question.
Virtual CISO
Firms are controllers for their own data and processors for client matters. Both roles carry obligations, and the role determination drives which ones.
Privacy programme
For firms deploying generative AI in drafting, review, research or discovery, the governance that answers where privileged data goes and what happens when the output is wrong.
AI governance
Network, application and social engineering testing. Law firms are a high-value phishing target and the sector’s exposure concentrates in people rather than infrastructure.
Penetration testing
HOW ELEVATE HELPS
Certification where clients ask, capability everywhere else
Elevate builds the certifications clients name and the operational capability that makes them true, which are not the same project.
ISO 27001 certification
ISMS build or transition to the 2022 edition, covering scope, risk assessment, Statement of Applicability, internal audit, management review and Stage 1 and Stage 2 audit support.
SOC 2 readiness
Scoping, control design, evidence structure and audit support for the report the client specified.
Virtual CISO
Named security leadership covering programme ownership, client security questionnaire response, incident readiness and the reporting that outside counsel guidelines increasingly require.
AI governance for legal practice
Acceptable use policy for generative AI covering privileged material, model and tool inventory, vendor data use review, and the ISO 42001 or NIST AI RMF programme underneath it.
Privacy programme
Controller and processor role determination, records of processing, data subject rights handling, and the CCPA, GDPR and state obligations that follow.
Penetration testing and social engineering
Testing scoped to the sector’s actual exposure, which concentrates in credential compromise and pretexting rather than in perimeter infrastructure.
Client security questionnaire support
The evidence set and the response capability that turns a recurring, resource-consuming questionnaire cycle into a repeatable one.
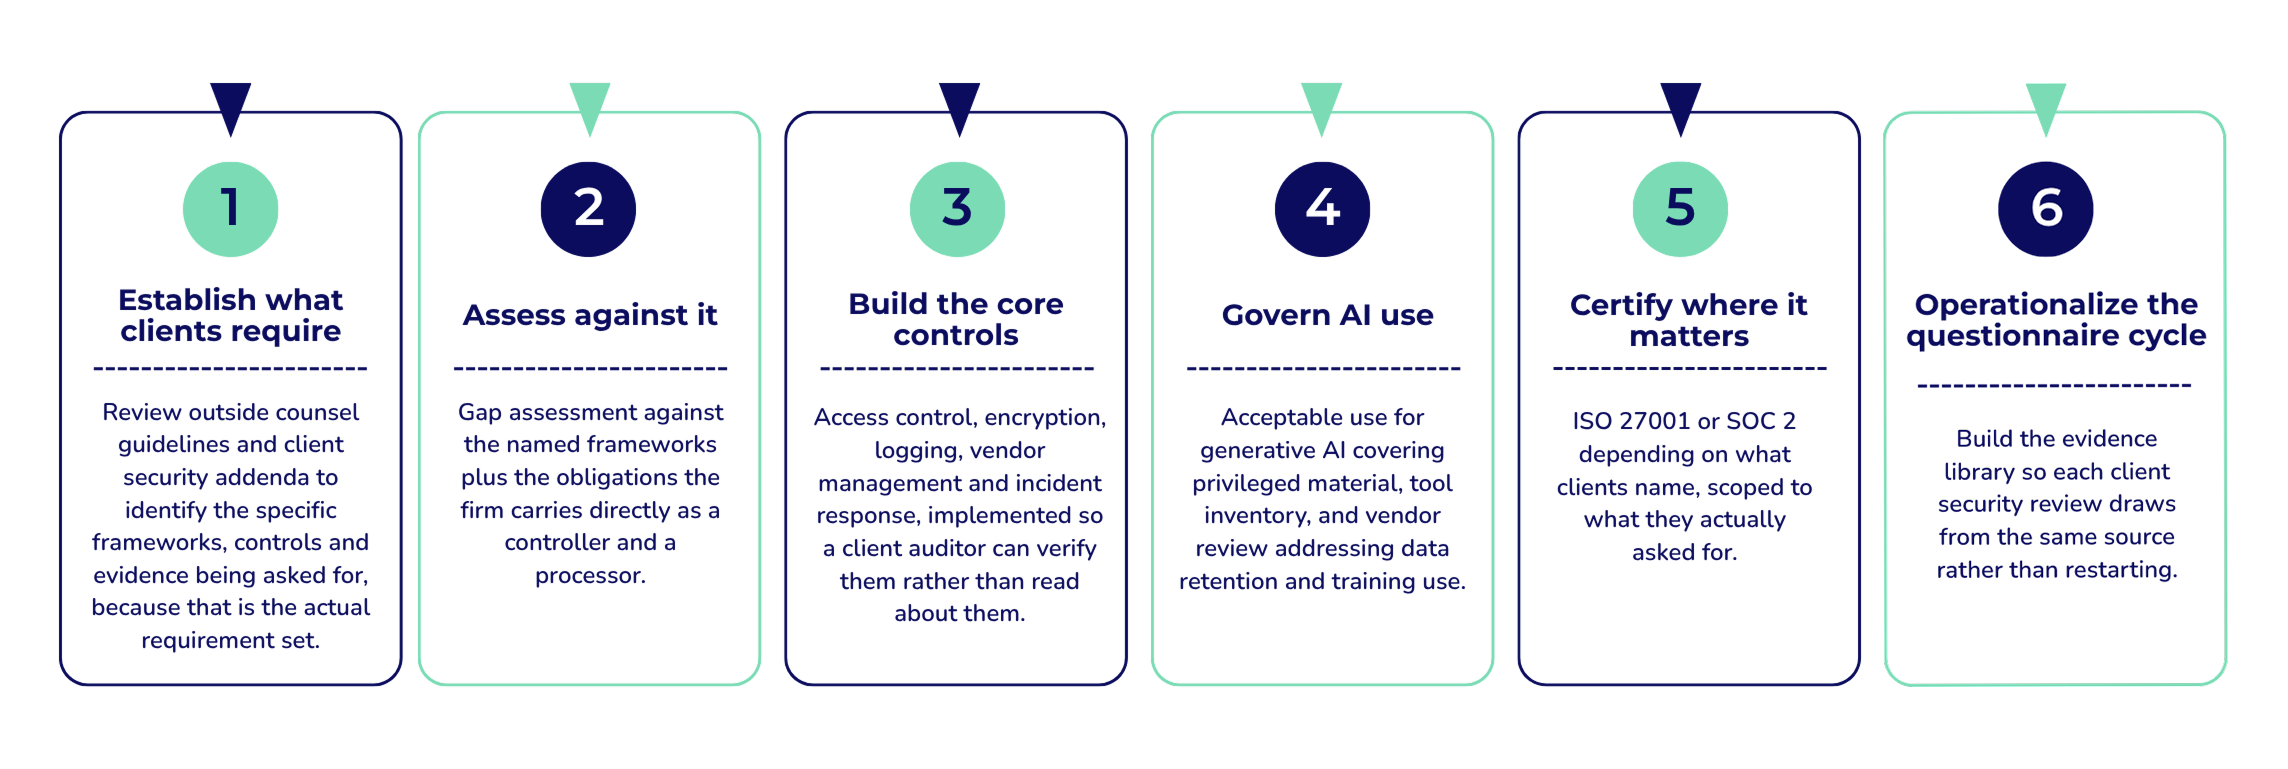
ENGAGEMENT PHASES
How the work runs
WHO THIS IS FOR
Roles Elevate works with on this standard
Managing partners and COOs
General counsel and in-house legal
Law firm IT and security leads
Risk and compliance officers
Knowledge management and innovation teams
GET STARTED
Ready to answer client security audits without a fire drill?
Elevate Consult builds the certifications your outside counsel guidelines name, the operational capability that makes them true, and the AI governance that generative tools in legal practice now require.
FAQ
Common Questions
🡪 Why do law firms face elevated cybersecurity risk?
Concentration. A single firm holds merger documents, litigation strategy, regulatory correspondence and personal data for many clients simultaneously, which makes it a more efficient target than any individual client. Corporate clients have responded by imposing security requirements contractually through outside counsel guidelines and by verifying them through audits.
🡪 What do outside counsel guidelines typically require?
It varies by client, but the requirements converge on recognizable artifacts: an ISO 27001 certificate or a SOC 2 report, named security ownership, encryption and access control standards, incident notification commitments with specific timelines, and increasingly questions about generative AI use with client material. The specific guidelines are the actual requirement set, so they should drive the programme rather than a generic framework.
🡪 Does the duty of confidentiality satisfy security obligations?
No. The professional duty creates the obligation; it does not create the controls, the evidence or the incident response capability that a client audit tests. Firms are increasingly asked to demonstrate rather than assert, and the gap between the two is what the security programme has to close.
🡪 Can we use generative AI with client material?
That is a policy decision the firm has to make explicitly rather than by default, and it needs to address where the data goes, whether the vendor uses inputs for training, retention, who can access outputs, and what happens when the output is wrong in a filing. Many outside counsel guidelines now ask the question directly, so an unwritten answer becomes a client-facing problem.
🡪 Do privacy laws apply to law firms directly?
Yes, in both roles. A firm is a controller for its own operational data covering employees, prospects and business contacts, and a processor for personal data handled in client matters. The CCPA and the state patchwork apply where thresholds are met, the GDPR where EU individuals are involved, and national laws such as Spain’s LOPDGDD where the firm operates there.
🡪 ISO 27001 or SOC 2?
Whichever clients name. SOC 2 is the more common ask from North American corporate clients; ISO 27001 travels better internationally and is what European clients recognize. Firms with a mixed client base often need both, and the control overlap means the second costs considerably less than the first once the first exists.