AI Risk Assessment: Steps, Owners & Remediation Planning (2026 Guide)
The numbers are striking – 78% of companies now use generative AI, but 91% of machine learning models drift within several years after deployment. Organizations implementing artificial intelligence systems need a solid risk assessment plan. The rapid AI adoption comes with serious challenges. AI-tool usage has led to data leaks in 68% of organizations, yet only 23% have proper security policies. Business leaders see the potential – over 60% believe AI will boost customer relationships and productivity. A well-planned risk assessment methodology becomes vital for long-term AI success. The stakes are high – companies that don’t document risk assessments under regulations like the EU AI Act risk fines up to 7% of global turnover. Let me walk you through detailed AI risk assessment frameworks and step-by-step methods that work. You’ll learn how organizations handle risk ownership throughout the AI lifecycle and blend third-party risk assessments into their governance. This piece will help you spot, prioritize and alleviate security, bias, and compliance risks in your AI systems before they create problems or regulatory issues. Understanding AI Risk Assessment and Its Scope Image Source: SlideTeam “By far, the greatest danger of Artificial Intelligence is that people conclude too early that they understand it.” — Eliezer Yudkowsky, AI Safety Researcher, Machine Intelligence Research Institute Organizations that use AI need to know what makes these systems risky. A well-laid-out risk assessment helps teams spot and fix potential problems before they cause damage. Definition and Purpose of AI Risk Assessment AI risk assessment helps teams spot, review, and alleviate potential risks in artificial intelligence technologies. The concept boils down to a simple formula: risk = (likelihood of an AI model error or exploit) x (its potential effect). This helps teams calculate both how likely problems are and how bad things could get if they happen. The National Institute of Standards and Technology (NIST) adds more detail to this idea. They describe AI risk as “the composite measure of an event’s probability of occurring and the magnitude or degree of the corresponding event. The impacts, or consequences, of AI systems can be positive, negative, or both and can result in opportunities or threats”. AI risk assessment does more than just find problems. It serves three key functions: Preventing harm to users and stakeholders by minimizing the likelihood of model errors Ensuring compliance with evolving regulatory requirements Enhancing trust by showing steadfast dedication to responsible AI use Risk management that works also helps teams discover the full potential of AI systems. Teams that tackle and document risks early create AI systems people can trust, balancing breakthroughs with responsibility. Difference Between AI Risk Assessment and AI Governance AI risk assessment and AI governance play different roles in an organization’s AI strategy. AI governance creates the big-picture frameworks, rules, and standards that guide AI research, development, and use. It writes the rulebook for responsible AI use with detailed policies and structures. AI risk assessment acts as the hands-on defense within the broader governance plan. Think of governance as your steering wheel and risk management as your brake pedal—it keeps your business safe when surprises pop up. Risk assessment zeros in on finding and fixing issues like: Data bias leading to unfair outcomes Model performance degradation Security vulnerabilities Privacy breaches Transparency issues These pieces work together through collaborative effort. AI governance builds the foundation that makes risk management work through clear accountability, defined policies, ethical AI use guidelines, regulatory alignment, and continuous monitoring. Missing either piece leaves organizations open to regulatory fines and reputation damage. When to Use an AI Risk Assessment Template Teams should check AI risks at several points in a system’s lifecycle. The first review should happen before buying or building anything. Regular checks should continue as long as the system runs. How often you check depends on several things: The system’s risk level to the organization and individuals How the organization employs the system Changes in technology and regulatory environments Risk-averse organizations might check more often to stay safe. Teams should also review risks when big changes happen—like using the system differently or adding new data sources. A standard risk assessment template gives teams four key benefits: consistent reviews they can repeat, audit-ready risk documentation, better teamwork between security and data science groups, and easier compliance across different regions. Simple checklists and random security reviews don’t deal very well with AI systems because of their unique challenges—hard-to-explain decisions, changing models, and new ways things can go wrong. A structured assessment framework helps organizations move from putting out fires to following a process they can measure, audit, and use for regulations. This systematic approach helps teams get the most from AI while keeping risks in check. Types of AI Risks and Their Real-World Impact Image Source: Info-Tech AI implementation comes with risks that affect users, organizations, and society. A well-laid-out risk assessment helps spot problems before they cause damage. Data Privacy and Security Risks AI systems handle massive amounts of personal data, which creates major privacy issues. Yes, it is challenging to control these risks. This challenge itself becomes risky as advanced models like GPT-4o evolve faster. AI data privacy risks come from data collection problems and security gaps. Organizations gather sensitive information without clear permission. Training data contains terabytes of personal details from social media, healthcare records, and financial information. This creates two risks—collecting data without people’s knowledge and using it beyond what was originally allowed. AI systems face unique security problems. Cybercriminals use AI to launch sophisticated attacks. They create automated phishing campaigns with convincing malicious content. The biggest problem is that only 24% of generative AI projects have proper security. This exposes data and models to breaches that cost $4.88 million on average. On top of that, new attack methods have emerged: Machine learning poisoning (contaminating training data with misleading information) Evasion techniques (malware that changes behavior to avoid detection) Autonomous attack bots (operating continuously without human intervention) Model Bias and Explainability Challenges AI models reflect and increase existing social biases. These systems
Budgeting and Timeline for Full AI Governance Framework Rollout
Companies that welcome AI tend to perform better than their competitors without an AI strategy in 2024. The benefits are clear, yet setting up a working AI governance framework creates major financial hurdles for many organizations. AI initiatives yield an average return of 3.5X, and 5% of companies see returns up to 8X. The costs of custom AI development vary widely from $20,000 to over $500,000. Projects often run over budget, with 60% of AI initiatives costing 30-50% more than planned. Building your own governance solution needs millions of dollars and dedicated teams working for long periods. Money tells just part of the story – internal development takes up valuable time and management attention that could serve core business goals better. This piece breaks down everything about budgeting and timing for your AI governance framework rollout. You’ll learn about the changing digital world of AI governance and pick the right framework template. We’ll detail the infrastructure costs, show realistic timelines, and guide you through maintaining your governance program. Trust matters more than ever – 71% of CEOs say it affects their organization’s success by a lot. That’s why proper AI governance has become essential today. What’s Different About AI Governance Rollouts in 2026 The AI governance landscape has changed dramatically since the early 2020s. AI governance frameworks have evolved from theory to crucial operational components in 2026, and they look quite different from their original versions. What’s Different About AI Governance Rollouts in 2026 Shift from model building to orchestration layers AI governance in 2026 puts orchestration first, rather than focusing on individual model governance. Companies started by managing specific models, but now they must handle complex AI systems where multiple models work together. This means governance frameworks must oversee entire AI orchestration layers. Teams must monitor more than just model outputs – they need to track how models interact, how data flows, and what decision paths look like. Modern enterprise AI governance frameworks now have specific controls to watch how models work together in larger systems. This marks a fundamental change from managing single AI components to overseeing complete AI ecosystems. On top of that, it’s clear that governance must go beyond technical aspects. The quickest way to handle orchestration involves matching AI systems with business goals and tracking their evolution over time. Rise of agentic AI and its governance implications Agentic AI systems, which can make decisions and act with minimal human oversight, present one of 2026’s biggest governance challenges. These systems don’t work well with traditional frameworks and need specialized approaches. Agentic AI governance is complex for several reasons: Decision autonomy: These systems make sequential decisions that we can’t easily predict or explain Goal-directed behavior: Agentic systems chase objectives almost independently Learning and adaptation: They keep evolving, sometimes in ways developers never predicted Agentic AI brings new risks about unauthorized actions, decision drift, and goal misalignment. Then, model AI governance frameworks must have specific controls to watch agent behavior, set boundaries for autonomous decisions, and create emergency override options. Companies rolling out AI governance frameworks must set clear rules about when humans need to step in. They also need detailed testing environments to check agentic systems before launch. Increased regulatory pressure and audit readiness Regulatory requirements are a big deal as they mean organizations can no longer develop AI governance frameworks without considering regulations. Major jurisdictions now have binding AI regulations with heavy penalties for those who don’t comply. The EU AI Act became fully active in 2025. It groups AI systems by risk and sets strict governance rules for high-risk applications. The US has created specific regulations through agencies like the FDA, FTC, and NIST, which makes compliance more complex. Being ready for audits has become crucial to AI governance framework implementation. Companies must keep detailed documentation, run regular internal audits, and prepare for regulatory inspections. This includes clear responsibility chains, documented decisions, and proof of compliance. AI governance frameworks typically have regulatory compliance modules that link controls to specific requirements. Organizations can easily show compliance during audits and avoid managing multiple governance structures. The focus on audit readiness has standardized AI governance documentation. The NIST AI governance framework and ISO 42001 lead the way, giving companies proven templates that meet regulatory requirements across different jurisdictions. Choosing the Right AI Governance Framework Template Image Source: Scrut.io The year 2026 will see organizations choose AI governance frameworks as their building blocks. Several time-tested options exist, and companies must assess which template lines up with their needs and regulatory environment. Comparing ISO 42001 vs NIST AI RMF Two major frameworks have become reference standards in the AI world: ISO/IEC 42001 and the NIST AI Risk Management Framework (NIST AI RMF). These frameworks show key differences that shape implementation choices. ISO/IEC 42001 comes from the International Organization for Standardization. It guides AI management systems and aims to ensure ethical, reliable, and clear AI technology development. The U.S. National Institute of Standards and Technology created NIST AI RMF. This framework takes a structured path to handle risks in AI systems throughout their lifecycle. These frameworks differ in structure: ISO 42001: Built around 10 clauses and 4 annexes with 38 specific controls. These cover policies, organizational structure, resources, and AI system lifecycle. NIST AI RMF: Works through four core functions – Govern (setting policies and accountability), Map (finding context), Measure (analyzing risks), and Manage (putting mitigation strategies to work). ISO 42001 stands out as a certifiable standard that needs external audits valid for three years and yearly checks. NIST AI RMF takes a different route with self-attestation and no formal certification, though companies can bring in third-party validators. Customizing a model AI governance framework for your org Your organization’s specific industry needs, context, and risk profile should guide framework customization. Start by getting a full picture of your AI systems and how they affect stakeholders, operations, and compliance needs. Several factors should guide your choice. ISO 42001 works better for global operations and compliance, especially in strict industries like healthcare,
AI Governance Certification Readiness: The Attestation Roadmap
Most organizations today face a critical gap in their AI systems. Recent studies show that 73% lack proper AI governance frameworks, which puts them at risk of regulatory fines and AI control failures. The EU AI Act’s enforcement brings steep penalties – organizations could face fines up to €35 million or 7% of their global revenue. The business world needs trustworthy AI governance more than ever. This piece offers a practical roadmap to help you get ready for AI governance certification. The numbers tell an interesting story: while only 37% of organizations regularly assess their AI risks, companies with mature governance frameworks see impressive results. These organizations deploy AI systems 3.2x faster and cut compliance risks by 87%. The introduction of ISO 42001, the first global management system standard for AI, gives organizations a clear path to build and improve trustworthy AI systems. The certification process can be challenging because it’s relatively new and has specific requirements. Our step-by-step approach will help you understand and prepare for AI ethics and governance certification, making this complex process more manageable. What AI Governance Certification Means in 2025 Image Source: Elevate Consult AI governance certification in 2025 goes beyond a simple compliance checkbox. It shows how well organizations know how to manage AI systems throughout their lifecycle. AI has become deeply woven into critical business processes, and the difference between traditional governance and specialized AI governance keeps growing more important. Enterprise AI Governance vs. Traditional IT Governance Enterprise AI governance builds on data governance and IT governance frameworks. Yet it tackles unique challenges that traditional methods can’t handle. The key difference lies in how AI systems work compared to regular IT systems. Traditional IT governance focuses primarily on: System reliability, security protocols, and infrastructure management Predetermined functions with predictable outcomes Static systems that follow rule-based processes Periodic audits for performance monitoring Enterprise AI governance must handle these extra dimensions: Dynamic Learning Systems: Regular software performs consistently after deployment. AI applications change as their data and infrastructure evolve, which makes it hard to maintain performance, transparency, and fairness. This means we need ongoing risk checks instead of one-time assessments. Ethical Considerations and Explainability: Traditional IT governance centers on security and compliance. AI governance must also deal with bias, fairness, and transparency. Many AI systems work like a “black box,” making it hard to understand why they make specific decisions. Model Governance Complexity: Companies need strategies to move AI models from lab to production safely and effectively. Poor planning can lead to model deterioration—this is a big deal as it means that companies face negative brand impacts, regulatory action, and safety issues. AI governance also needs special monitoring that goes beyond regular IT metrics. This includes model drift detection, fairness assessments, and explainability requirements. Companies using AI-driven solutions need governance frameworks built specifically for these changing risks and learning models. How ISO 42001 and NIST AI RMF Complement Each Other Two frameworks lead the way for AI governance certification in 2025: ISO 42001 and the NIST AI Risk Management Framework (RMF). These frameworks don’t compete—they work together to provide detailed AI governance. ISO 42001 creates an AI Management System (AIMS) that focuses on ethical AI usage, transparency, and trust. This globally recognized standard helps build credibility with stakeholders worldwide and makes market entry easier. It guides companies through managing AI quality from design to maintenance. NIST AI RMF provides a more flexible approach to managing AI system risks. It uses four core functions—Govern, Map, Measure, and Manage—to help identify, assess, and reduce AI-specific risks. These frameworks support each other in several ways: ISO 42001’s structured management system works well with NIST AI RMF’s risk-based approach. ISO 42001 sets up organizational governance structures, while NIST AI RMF shows how to spot and fix risks. ISO 42001 creates a detailed management framework that covers organizational governance and legal compliance. NIST AI RMF helps make AI systems more trustworthy and reliable by addressing technical, ethical, and societal risks. Many organizations use both frameworks together or one after the other. A combined approach uses ISO 42001’s global standardization and quality assurance with NIST AI RMF’s flexibility and ethical focus. Some companies start with NIST AI RMF during early AI adoption and switch to ISO 42001 as their AI systems mature. AI governance professionals need to understand both frameworks. The AI governance certification market will reach USD 15 billion by 2026, growing faster than most security or ethics-driven sectors. This growth shows the rising need for experts who can understand regulations, arrange AI systems with these frameworks, and check models for bias and explainability. Assessing Your Current AI Governance Maturity Image Source: Ali Arsanjani – Medium You need to know your organization’s current maturity level before getting AI governance certification. This step sets a clear baseline and shows exactly where your governance practices need work. Using a 5-Level Maturity Model for Self-Assessment Enterprise AI governance frameworks use a five-level system to measure organizational readiness. These maturity models give you a well-laid-out path to review and boost your AI governance capabilities. The five levels are: Initial/Ad-Hoc (Level 1): AI governance doesn’t exist or only reacts to problems at this stage. Individual enthusiasts or isolated teams drive AI adoption using their preferred tools. Risk exposure is very high. “Shadow AI” runs wild without any standard policies. Managed/Repeatable (Level 2): Organizations see the need for control, but efforts remain scattered. Each department creates its own guidelines without central coordination. This leads to mixed practices across the enterprise. Defined/Standardized (Level 3): Organizations reach a turning point and set up unified governance frameworks. An AI Governance Council forms with members from Legal, IT, Ethics, and Operations. A central AI policy covers data privacy and fairness. Managed (Level 4): Organizations track and review activities regularly. They add technical controls like instrumentation and metrics to support evidence-based governance. Optimized (Level 5): Governance becomes part of AI systems architecture. The governance layer grows smarter and can understand context and adapt to conditions. Start your self-assessment by comparing
AI Governance and Ethics: Controls, Reviews & Approvals
Cloud-based attacks now account for 82% of all security breaches. This alarming trend makes AI governance and ethics top priorities. Yet only 29% of organizations have detailed AI governance plans, which leaves them vulnerable to major risks. The regulatory world has changed. A resilient AI governance framework is now mandatory for businesses. The EU AI Act of 2024 stands as the world’s most detailed artificial intelligence governance law. Organizations face steep penalties – up to €35 million or 7% of total global turnover. Legal, compliance, and audit leaders rank technology as their primary risk concern, above economic factors and tariffs. Organizations must develop strong AI governance principles and clear policies to discover the full potential of AI while reducing its risks. Poor responsible AI governance can backfire badly. The Dutch government learned this lesson when the District Court of The Hague struck down their System Risk Indication (SyRI) for human rights violations. But 68% of executives still think generative AI’s benefits outweigh its risks. This makes proper controls and review mechanisms crucial. This piece will guide you through the key elements of effective AI governance. We’ll cover everything from ethical foundations to practical controls and approval processes that safeguard your organization while supporting innovation. Why AI Governance and Ethics Are Business-Critical Image Source: Medium “We’re seeing a kind of Wild West situation with AI and regulation right now. The scale at which businesses are adopting AI technologies isn’t matched by clear guidelines to regulate algorithms and help researchers avoid the pitfalls of bias in datasets.” — Timnit Gebru, Founder of The Distributed AI Research Institute, AI ethics pioneer AI adoption is booming – 70 percent of organizations use it without proper governance structures. The scary part? Most don’t see this gap as a major risk. This dangerous mix of quick adoption without oversight puts businesses at risk on many fronts. Setting up proper ai governance and ethics isn’t just about tech anymore – we need it to run our businesses. Reputational risks from ungoverned AI Bad AI can wreck a company’s image and destroy stakeholder trust in minutes. The Global Situation Room’s Reputation Risk Index now calls AI misuse the biggest threat to organizations. This damage hits more than just PR – it costs real money: Loss of revenue: Customers jump ship to competitors they see as safer or more ethical, hitting both immediate and future income Rising acquisition costs: Lost trust means spending more to get new customers through big discounts or expensive PR fixes Market valuation impact: Stock prices usually take a hit after AI-related problems come to light Talent attrition: Top performers and business partners often walk away from companies with questionable AI practices Generative AI causes special headaches since algorithm mistakes can spread like wildfire online. Brands face quick public anger when AI-created content has obvious mistakes or seems to push human creativity aside. On top of that, public awareness about AI ethics keeps growing. A recent survey showed 72% of people worry about AI systems using their personal data without permission. Legal liabilities from biased or opaque models Legal risks from biased or non-transparent AI systems keep piling up. AI now helps make decisions about hiring, lending, healthcare and customer service. Companies that ignore ethical principles like fairness, transparency and accountability face serious legal trouble. Disparate impact liability has become a key legal tool against algorithmic discrimination. People can now sue for discrimination based on protected characteristics without proving intent – crucial since machines can’t have “intent” in legal terms. A newer study, published by the University of Washington, found AI models picked resumes with white-associated names 85% of the time, while choosing those with Black-associated names only 9% of the time. Courts have started setting important precedents in AI bias cases. The Mobley v. Workday, Inc. case saw the Northern District of California certify a collective action. They warned that treating software and human decision-makers differently could gut anti-discrimination laws in today’s world. The EEOC has also made it clear – employers will answer for their AI hiring systems. Examples of governance failures: The SyRI case The SyRI case shows exactly why we need solid ai governance principles. Back in 2020, the District Court of The Hague shut down the Dutch government’s System Risk Indication (SyRI) – an automated system meant to catch welfare fraud. The court found that SyRI violated human rights. The system lacked privacy protections and nobody could explain how it worked. The system targeted low-income neighborhoods, raising red flags about discrimination against poor people and immigrants. The court said it failed the “fair balance” test under European human rights law. This ruling set a global precedent for organizations using automated decision systems. As digital welfare systems spread worldwide, courts will likely follow suit and ban systems that step on basic rights. The SyRI case proves that robust artificial intelligence governance isn’t optional – organizations need it to avoid legal, financial, and reputation damage. Companies must now ask not just “Can AI do this?” but “Should AI do this, and what happens if it goes wrong?”. Every organization will face this question sooner or later. Ethical Foundations for AI Governance Policy Image Source: Vera Solutions A reliable ai governance framework needs strong ethical foundations to work well over time. AI technologies now cross borders and industries worldwide. This has led international organizations to create detailed guidelines that have become the life-blood of responsible AI use globally. OECD AI Principles and UNESCO Ethics Guidelines The OECD AI Principles have shaped global artificial intelligence governance since their adoption in 2019 and recent update in May 2024. These principles help create AI that people can trust while protecting human rights and democratic values. The principles now guide 47 countries, making them the first worldwide standard for AI. They focus on: Inclusive growth and sustainable development Human rights and democratic values Transparency and explainability Robustness, security, and safety Accountability UNESCO’s Recommendation on the Ethics of AI adds another key element to ai governance policy.
Selecting Your Technology Partner: Vetting AI Governance Consulting
AI tools have found their way into almost 80% of organizations, which makes ai governance consulting crucial for modern businesses. While AI adoption soars, trust remains a concern – only 27% of executives would put their faith in fully autonomous agents for enterprise use. Business functions that once treated AI as experimental now consider it mission-critical, yet governance frameworks lag behind this rapid transformation. Investment in AI continues to surge, with the global market expected to hit $391 billion by 2025. The technology’s impact grows deeper as 65% of businesses now use generative AI in at least one function. Security remains a pressing issue, with 71% of organizations pointing to new threats as their main concern. These trends highlight why ai governance consulting services have become fundamental to business operations. This piece will help you understand what ai governance consulting encompasses and how to pick the right partner to address these complex challenges. You’ll discover concrete criteria to make informed decisions, whether you’re new to ai governance consulting firms or ready to enhance your existing framework. Identifying High-Impact Use Cases for AI Governance Image Source: KumoHQ “The problem that needs to be addressed is that the government itself needs to get a better handle on how technology systems interact with the citizenry. Secondarily, there needs to be more cross-talk between industry, civil society, and the academic organizations working to advance these technologies and the government institutions that are going to be representing them.” — Clem Delangue, Co-founder and CEO, Hugging Face Choosing the right ai governance consulting partner starts with finding suitable use cases. McKinsey research reveals that only 15% of boards get AI-related metrics. This suggests a huge gap in governance oversight. The best consultants can help close this gap by targeting areas where AI governance delivers maximum business value. Lining up AI governance with business goals AI governance must connect directly to your organization’s strategic goals to succeed. Your governance efforts should match how much AI affects your competitive landscape. The first step toward effective AI governance requires clear agreement between leadership and management about your company’s AI direction and vision. Great consultants begin by exploring how AI governance can boost specific business goals like customer satisfaction, operational efficiency, or sustainability targets. This approach ensures governance becomes a business value driver rather than just a compliance task. Prioritizing use cases with measurable ROI Many organizations face challenges with AI initiatives because they lack a structured way to pick the right opportunities. MIT research shows that sales and marketing make up about 50% of GenAI investments based on executive estimates. These areas get more attention because they show clearer ROI. Look for ai governance consulting services partners who: Help calculate potential opportunities and risks of AI adoption Set up measurable metrics tied to business outcomes Help develop a “lowest-hanging fruit” method to find high-impact, low-effort use cases The best consultants suggest starting small with practical use cases that show value within 2-4 weeks. This builds momentum for bigger initiatives. Avoiding AI for AI’s sake: focusing on outcomes Companies often make the mistake of implementing AI without connecting it to business outcomes. Good ai governance consulting firms help you avoid this trap by focusing on both business value and responsible implementation. Leading consultants make sure AI initiatives support measurable goals – better customer experience, lower operational costs, improved productivity, or predictive analytics capabilities. They help you choose AI use cases that match your KPIs. This ensures your AI strategy drives growth instead of becoming a cost burden. Note that excellent governance stands out through consistent execution across the AI lifecycle, not just documentation. Top consultants make this easier by linking experimentation with accountability, so AI delivers real business value. Key Criteria for Selecting AI Governance Consulting Services Image Source: Info-Tech Choosing the right partner for AI governance needs a thorough look at several critical factors. Top-tier AI governance consulting partners don’t just offer generic solutions—they bring specialized expertise that fits your organization’s unique challenges. Domain expertise in your industry Your AI governance success depends on industry-specific knowledge. AI behavior can lead to completely different outcomes based on the sector. Healthcare, finance, and aviation need governance frameworks that focus on traceability and compliance because of strict regulations. Less regulated sectors work better with flexible approaches. You should look for consultants who have proven experience in your specific industry and understand your operational incentives and regulatory requirements. Structured methodology for governance implementation Good consultants give you clear frameworks that blend with your existing risk management practices. IBM’s approach tackles both organizational governance and technical tools. Their well-laid-out methods define roles, responsibilities, and accountabilities throughout the AI lifecycle. On top of that, the best partners help you create AI governance councils with leaders from your company to oversee initiatives and show commitment to ethical guardrails. Support for responsible AI practices and compliance The best consulting services help organizations build adaptable frameworks that keep AI systems ethical and compliant. They help you conduct AI risk assessments, set up testing protocols for fairness and transparency, and create ongoing monitoring systems. As regulations like the EU AI Act continue to change, your consultant should guide you through these changes. Ready to assess your AI governance readiness? Book a Readiness Call to get a full picture of your organization’s current capabilities and identify next steps. Ensuring Scalability, Integration, and Post-Launch Support Image Source: LeewayHertz “The next decade will see AI move beyond being a back-office efficiency tool to becoming a potentially proactive ethical compass for nonprofit boards. The way things are headed, I sense that AI will not only analyze compliance and performance data in real time but also flag ethical dilemmas before they occur — surfacing unintended consequences of decisions and their impacts, potential mission drift risks and stakeholder sentiment shifts.” — Patrick Downes, Managing Partner, Governance Ireland The success of any AI initiative depends on how well it grows and merges after the original deployment. Good AI governance consulting must tackle these post-implementation challenges
Finalizing the Data Provenance Strategy for AI Data Governance
Poor data quality costs organizations $12.90 million each year. This makes AI data governance essential for business success. Humans and machines produce about 402 million terabytes of data daily in 2024. Such massive volumes create significant challenges for data management and integrity. The rise of generative AI and large language models in daily operations has shifted the focus. The question now focuses on how AI governance affects financial and operational results. Data provenance tracks a record’s history from its origin through various changes. It has become essential to work effectively with governance. Companies that excel at data governance and AI frameworks show better results than their competitors. This happens especially when they maintain strong data culture and stewardship. Healthcare teams provide a perfect example. They use provenance tracking to maintain accurate patient records from collection through modifications. Clear governance rules, permissions, and audit trails have become essential. These ensure AI systems interact with approved data and deliver responsible outcomes. This piece will show you how to create a detailed data provenance strategy. You’ll learn to strengthen your AI data governance framework by setting up ownership roles and building strong infrastructure that meets regulations. Positioning Data Provenance in the AI Governance Lifecycle Image Source: Atlan Data provenance is the life-blood of good AI governance. It creates a historical record that helps organizations track information’s trip from creation through changes. It goes beyond simple data cataloging by recording the complete lifecycle—who created the data, when it was created, what changes happened, and who made those changes. This detailed documentation helps reshape the scene by turning AI systems from mysterious “black boxes” into transparent, accountable technologies. How provenance supports ai governance goals Data provenance tackles several vital AI governance objectives. It builds authenticity and integrity through verifiable records of data origins. This verification has become more important now that studies show people can spot AI-generated content only 50% of the time—no better than guessing. So, provenance documentation are the foundations of: Regulatory compliance: Organizations need to show they follow laws about data use, bias reduction, and system safety Risk management: Provenance data helps identify and fix potential issues Debugging capabilities: Teams can trace problems back to their source when issues come up Bias identification: Looking at data sources helps spot potential biases before they show up in AI outputs Provenance also helps solve transparency problems in AI by answering vital questions: Where did the training data come from? Does it have intellectual property protection? Did it come from unreliable or biased sources? AI systems stay fundamentally unclear to users, regulators, and affected communities without these answers. Data provenance is different from data lineage even though they’re related. Lineage tracks technical data flows at file and process levels, while provenance focuses on authenticity, integrity, and historical context of individual data elements. These concepts work together in governance frameworks. Lineage shows the technical path while provenance builds credibility. Data engineers use lineage to debug pipelines, while legal and compliance teams need provenance to check audit requirements and usage rights. Connecting provenance to model versioning and monitoring Models without provenance face big challenges. Data scientists often talk about building models with old data copies. They spend hours looking for file sources or wondering if they used the right processing scripts on the original data. These problems get worse when multiple teams work with data. Teams become afraid to make changes that might break dependencies. Provenance becomes strong infrastructure to version and monitor models by: Enabling reproducibility: Teams can recreate exact training conditions and datasets with detailed provenance tracking Facilitating debugging: Provenance helps find specific data inputs or changes when models act strangely Supporting continuous monitoring: Regular provenance tracking spots data drift, poisoning attacks, or contamination Enhancing collaboration: Clear documentation lets multiple teams work with shared data confidently Developers can track provenance in several ways, from manual documentation to automated systems. Some platforms track provenance automatically for all code run, which works well in cloud-hosted integrated machine-learning environments. The goal stays the same whatever method you use: keep an unbroken chain of documentation from data creation through model development and deployment. We have a long way to go, but we can build on this progress in implementing detailed provenance. Organizations should create governance frameworks with clear rules for data management and tracking. Blockchain and data lineage tools can automate tracking and improve metadata records. Data provenance isn’t just about following rules – it’s vital infrastructure to build AI systems people can trust. Establishing Ownership and Roles for Provenance Management Image Source: SlideTeam Organizations need clear ownership and defined roles in their data governance structure to manage provenance. Teams can map, measure, and manage AI risks throughout the data lifecycle with proper accountability systems in place. The NIST AI Risk Management Framework states these accountability structures are the foundations of responsible AI deployment. data stewards vs ai stewards: responsibilities Data stewardship is the foundation of provenance management that includes the complete data lifecycle from creation to deletion. Data stewards focus on five main responsibilities: Ensuring data integrity – Quality and accuracy maintenance supports effective decision-making Enforcing data privacy and security – Working with IT teams to implement strong access controls, encryption, and security measures Managing metadata – Documentation provides clarity about data origins Facilitating communication – They bridge technical teams and business executives to translate complex concepts Implementing governance policies – They arrange with both regulatory requirements and business objectives Data stewardship isn’t usually a dedicated role. Business Analysts, Data Engineers, IT Managers, Department Heads, and Compliance Officers often handle these responsibilities. AI stewards have emerged as an extension of traditional data stewardship roles. Their focus has shifted from human-generated data to overseeing how artificial intelligence processes information. They make sure it fits with existing governance standards. This creates a key difference: data stewards handle traditional data assets, while AI stewards tackle the unique challenges of AI systems and their data interactions. These roles become crucial if you have provenance tracking. Data stewards link with each layer
How to Build Evidence Maps for AI Governance: A Practical Guide for 2026
The numbers are concerning – only 43% of organizations have an AI governance policy, and a third have none at all. This gap shows a critical challenge we face in 2026. While 78% of organizations use AI in at least one business area, only 25% have fully implemented AI governance programs. This creates a 53-percentage-point gap between adoption and governance maturity. The governance gap becomes especially worrying when industries adopt AI systems faster into their operations. A recent survey shows that 84% of health insurers already use AI and machine learning in some capacity. Organizations need structured, risk-based policies that cover all AI systems to ensure compliance and audit readiness. Frameworks like ISO/IEC 42001:2023 provide a familiar plan-do-check-act structure that can make legal requirements operational. However, many organizations don’t deal very well with practical implementation. Let me walk you through building effective evidence maps for AI governance in this piece. This practical approach helps reshape complex frameworks into implementable controls. Our research breaks down thousands of pages of standards and regulations into twelve essential domains. You’ll learn how to create evidence artifacts that connect AI governance principles with demonstrable compliance. Key Takeaways Evidence maps are essential tools that transform AI governance from theoretical frameworks into demonstrable compliance, bridging the critical gap between AI adoption and regulatory requirements. • Regulatory enforcement has shifted from voluntary guidelines to binding requirements – Organizations face real consequences including fines, forced system withdrawals, and reputational damage without proper evidence documentation. • Evidence maps create traceable connections between obligations and artifacts – Unlike simple checklists, they establish dynamic relationships linking regulatory requirements to specific test results, documentation, and operational controls. • Centralized evidence indexes prevent “AI sprawl” and compliance gaps – Structured registries with version control and traceability mechanisms ensure all AI systems remain visible and governable across the organization. • Integration into AI lifecycle workflows enables proactive governance – Pre-deployment checkpoints and post-market monitoring transform evidence maps from static documents into operational tools that adapt throughout system lifecycles. • Practical tools like model cards and requirement matrices make governance actionable – Standardized documentation and visualization platforms help organizations move from “governance by PDF” to measurable, auditable controls. The transition from principles to proof is no longer optional—organizations must implement systematic evidence mapping now to avoid reactive compliance measures when regulations, audits, or incidents force their hand. Why Evidence Maps Are Now Essential for AI Governance AI regulations have changed completely since 2025. What started as optional frameworks and ethical guidelines has grown faster into binding requirements with real consequences. These changes make evidence maps vital tools for organizations dealing with AI governance. Regulatory enforcement trends in 2026–2027 Regulators worldwide now focus on enforcement instead of guidance. What used to be optional has become mandatory compliance. The EU AI Act stands out as the clearest example – its high-risk obligations will take full effect in August 2026. Italy’s €15 million fine against OpenAI for GDPR violations in training data processing shows that regulators want documented controls and technical safeguards, not just ethics statements. U.S. states have stepped up to fill the federal regulatory gap. Colorado’s AI Act will take effect June 30, 2026. It requires developers and deployers to prevent algorithmic discrimination, assess impact, and inform consumers. California has also put in place generative AI transparency requirements and frontier AI safety frameworks. Recent enforcement actions show what organizations should expect. The FTC’s “Operation AI Comply” went after deceptive AI marketing. State attorneys general have increased their oversight too. Pennsylvania’s Attorney General settled with a property management company in May 2025 over claims that its AI platform led to unsafe housing. Insurance markets send another clear message. Carriers now offer “AI Security Riders” that need proof of adversarial red-teaming, model risk assessments, and special safeguards before providing coverage. Insurance companies base decisions on loss data and exposure models, not philosophy. Shift from principles to proof in AI compliance The biggest change in AI governance is the switch from beliefs about responsible AI to actual proof. Missing documentation can now violate regulations. Organizations must show: Technical documentation files for high-risk systems Post-market monitoring plans that track real-life harms Conformity assessment results proving safety and accuracy Impact assessments covering bias, privacy, and fundamental rights AI governance must now focus on proof rather than policy. Companies can measure their “say-do ratio,” and written principles alone won’t cut it anymore. Organizations need well-laid-out evidence maps that link governance requirements to specific artifacts. Evidence maps help build effective knowledge management systems. They show gaps in current evidence and point out areas that need more attention. AI tools can create these maps well, helping build “living” synthesis products that update automatically with new research. The 2026 goal is clear – AI governance must move from theory to proven controls. Companies without consistent, auditable oversight of AI systems risk higher costs through fines, forced withdrawals, damage to their reputation, or legal expenses. Evidence mapping isn’t just about documentation – it’s crucial for managing risk. By 2026, healthcare and other regulated sectors won’t just look at vendor governance to tell them apart. It will determine if they can use systems at all. Models that can’t explain outputs or show how they handle bias and safety risks will face pushback, whatever their accuracy claims. Understanding the Role of Evidence in AI Governance Frameworks Image Source: Northwest AI Consulting Major AI governance frameworks now give us well-laid-out ways to collect evidence. Each framework has its own method to show compliance. These frameworks help create systems we can track and audit that link principles to real-life use. ISO/IEC 42001 and the PDCA model ISO/IEC 42001, which came out in December 2023, is the world’s first AI management system standard you can get certified for. Many frameworks look at specific AI uses, but ISO/IEC 42001 takes a different path. It looks at the management structure that supports AI systems through an Artificial Intelligence Management System (AIMS). The standard uses the Plan-Do-Check-Act (PDCA) method across ten well-laid-out clauses. Organizations
The Cost of Inaction: Budgeting for AI Risk Assessment vs. Fines
Companies that don’t assess AI risks properly face huge financial penalties. The EU has collected almost five billion euros in GDPR fines since 2018. AI compliance failures cost businesses 15-25 times more than what they would have spent on original governance investments. The digital world of artificial intelligence regulation has changed. The EU AI Act now hits violators with fines up to €35 million or 7% of global annual turnover for serious violations. This makes proper risk management crucial for survival. Tech companies should prepare because Gartner expects AI regulatory disputes to rise by 30% by 2028. Most organizations struggle to create a complete AI risk assessment framework that works for both current and future compliance needs. The numbers tell a concerning story – 95% of organizations faced negative outcomes from their AI projects. Even worse, 77% lost money directly over two years. Risk assessment for generative AI brings its own set of problems as the technology keeps evolving faster with new uses. This piece compares the costs of taking early action on AI risk assessment versus the potential financial damage from non-compliance. It also shows practical ways your organization can assess AI risks and avoid becoming another warning example. Understanding the Cost Structure of AI Non-Compliance AI regulation non-compliance costs go way beyond the reach and influence of basic fines. The real cost breakdown has immediate penalties, hefty legal bills, and long-term fixes. These expenses make proactive AI risk evaluation look like a bargain. Regulatory penalties under EU AI Act and BIPA The EU AI Act uses a three-tier penalty system based on how bad the violation is. The worst offenses – those breaking rules about banned AI practices – can cost companies €35,000,000 or 7% of their worldwide yearly revenue, whichever hits harder. Breaking general AI Act rules brings the penalty down to €15,000,000 or 3% of yearly revenue. Even small slip-ups like giving wrong info to authorities can lead to fines of €7,500,000 or 1% of yearly revenue. BIPA (Illinois Biometric Information Privacy Act) packs quite a punch too. Until just a while back, BIPA violations added up with each biometric scan. Companies had to pay between $1,000 for accidents and $5,000 for intentional violations per scan. This rule created some eye-popping numbers – White Castle faced a possible $17 billion hit just for scanning employee fingerprints repeatedly. A new change to BIPA now caps it at one violation per person no matter how many scans happen. The financial risk stays pretty big though, especially if you have lots of users. Litigation and legal defense costs Companies that fail AI compliance checks face big legal bills on top of those penalties. Attorney fees, court costs, expert witness payments, and settlements often cost more than the original fines. Legal defense usually needs: Lawyers who know AI regulations inside out Money for digging up technical documents Expert witnesses who can break down AI systems Class action defense teams, especially for biometric cases Companies dealing with rule-breaking in different places end up paying even more as they try to handle various regulations. Just answering regulatory questions can mess up normal business operations. Remediation expenses for AI system redesign Most ai risk assessment frameworks miss the huge cleanup costs that come after breaking compliance rules. When regulators catch an AI system breaking rules, companies must: Stop using non-compliant AI right away Build new systems that follow the rules Set up better tracking and documentation Get staff up to speed on following rules These fixes cost serious money through lost work time, tech team distractions, and business disruptions. Tech teams often have to stop working on cool new stuff to fix compliance issues. This hurts their market position and slows down important projects. Companies also need to build retrieval-augmented generation systems that only use approved, licensed content instead of random internet stuff. This means big system changes, not just quick fixes. Good AI risk assessment methods help spot these costs early. Companies can then invest smartly in following rules instead of spending money in panic mode. Teams that use structured AI risk assessment questions while building systems usually dodge these snowballing costs by staying on top of things. Indirect Business Impacts of Ignoring AI Risk Assessment Poor AI risk assessment leads to more than just regulatory fines and legal expenses. The ripple effects on business often go well beyond initial cost estimates. These secondary effects can put an organization’s survival at risk, whatever its market position. Revenue loss from paused AI operations Companies that launch AI projects without proper risk evaluation often need to shut down operations completely. This directly hits their revenue streams. A shocking 95% of enterprise AI pilot programs fail to show any measurable effect on profit and loss statements. This shows how unprepared deployments tend to collapse under pressure. The challenges show up at every stage. Almost half (48%) of companies that started AI projects ended up having to pause or completely reverse these initiatives. These shutdowns happen because of data privacy issues (48%), weak regulatory frameworks (37%), and customer concerns (35%). Short-term pauses often turn into complete abandonment. Bad test results tend to raise red flags among executives who aren’t familiar with development processes. Their concerns can shut down entire generative AI programs—not just single applications. This leads to wasted investments and missed revenue opportunities. Market valuation drops post-incident Stock markets react quick to signs of AI governance failures. The S&P 500 software and services index fell 4.6% in early 2026. This wiped out about USD 1.00 trillion in market value in just seven trading days. Some companies saw even bigger drops—ServiceNow fell 7.6%, Salesforce lost 4.7%, and Microsoft dropped 5%. This “software-mageddon” selloff hit companies of all types. Thomson Reuters saw its biggest one-day drop ever after investors worried about Anthropic’s Claude disrupting its legal business. Markets now see AI disruption risk as a threat to the survival of 10-year-old business models. Financial experts say we might just be seeing the start. Some predict an
ISO/IEC 42001: Why Your AI Platform Needs an AIMS
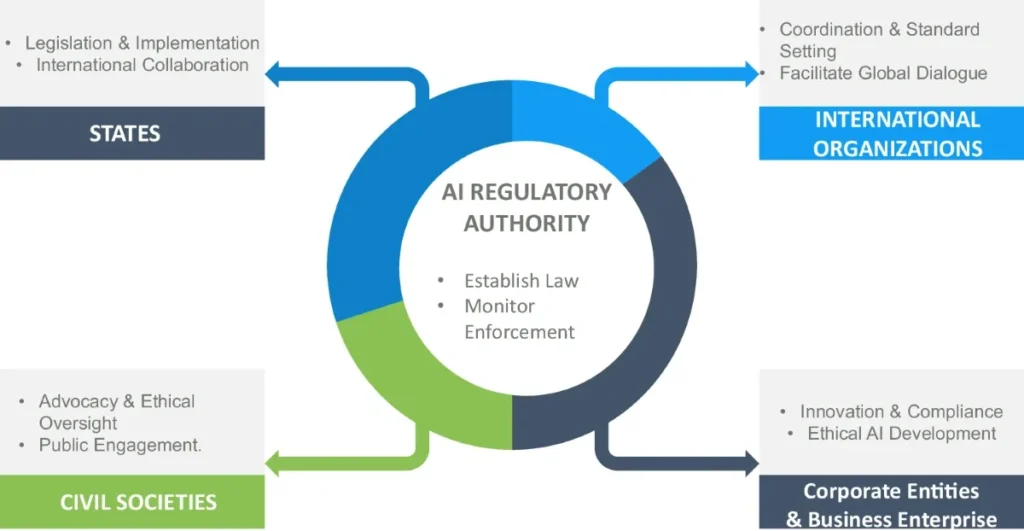
Organizations are rapidly embracing artificial intelligence – 72% now use AI in at least one business function, a significant jump from 55% last year. The world’s first international standard for Artificial Intelligence Management Systems (AIMS), ISO IEC 42001, has emerged to guide responsible AI governance. The International Organization for Standardization and the International Electrotechnical Commission published this well-laid-out framework in December 2023. The timing proved perfect as GenAI hype decreased and boardroom concerns grew. ISO/IEC 42001 serves a broad purpose. It helps enterprises prove their accountability and match requirements with emerging regulations like the EU AI Act, which became effective August 1, 2024. Companies that obtain ISO 42001 certification can achieve compliance 40% faster compared to those beginning without it. This piece explains ISO/IEC 42001’s importance for your AI platform and shows how AIMS implementation builds stakeholder trust through responsible AI management. You’ll learn practical implementation steps and understand how this standard supports regulatory compliance in the ever-changing AI world. What is ISO/IEC 42001 and Why It Matters for AI Platforms AI systems are becoming more complex, and organizations just need structured governance frameworks. ISO/IEC 42001:2023 serves as the life-blood for organizations that want to manage AI responsibly throughout its lifecycle. Definition of ISO/IEC 42001:2023 ISO/IEC 42001 became the world’s first internationally recognized standard specifically designed for AI governance in December 2023. This groundbreaking framework gives systematic guidelines to establish, apply, maintain, and improve an Artificial Intelligence Management System (AIMS) within organizations. The standard tackles unique AI challenges—including ethical considerations, transparency, accountability, and data privacy concerns. At its core, ISO/IEC 42001 creates a well-laid-out approach to manage AI projects, from complete risk assessment to effective risk treatment. Organizations that implement ISO/IEC 42001 see many benefits: Better quality, security, traceability, and reliability of AI applications Boosted efficiency in AI risk assessments Greater confidence in AI systems Lower costs of AI development Better regulatory compliance The standard follows the proven Plan-Do-Check-Act methodology that organizations with existing management systems know well. This approach will give proper oversight, helps organizations adapt to technology progress, and ensures regular AI risk assessments. What is an AI Management System (AIMS)? An Artificial Intelligence Management System is a set of interrelated or interacting elements within an organization. It establishes policies, objectives, and processes for responsible AI development and use. AIMS provides the operational framework you need to govern AI systems throughout their lifecycle. ISO/IEC 42001’s AIMS structure covers policies to optimize, reduce risks, and continuously improve AI operations. It highlights principles like fairness, non-discrimination, and privacy respect to line up AI systems with society’s values and public interests. On top of that, it helps organizations comply with emerging AI legislation and build trust with stakeholders. Organizations with AIMS can spot and fix potential risks before they become major problems. How ISO/IEC 42001 is different from ISO/IEC 27001 and SOC 2 ISO and IEC jointly publish ISO/IEC 42001 and ISO/IEC 27001, but they serve different purposes. ISO/IEC 27001 focuses on Information Security Management Systems (ISMS) to ensure information confidentiality, integrity, and availability. ISO/IEC 42001 targets AI Management Systems with a focus on responsible, transparent, and explainable AI operations. ISO/IEC 27001 concentrates on data security, access control, and network protection. We focused ISO/IEC 42001 on AI risk, ethics, data governance, and AI lifecycle management. All the same, both standards make important contributions to organizational governance and risk management. Organizations that already have ISO/IEC 27001 certification can implement ISO/IEC 42001 up to 40% faster. This speed comes from their similar structures, despite focusing on different areas. Together, they create a unified governance structure that handles both information security and AI-specific challenges with an all-encompassing approach. ISO/IEC 42001 brings new AI-specific requirements that ISO/IEC 27001 doesn’t have: Transparency and explainability documentation Specialized data governance and quality standards Model development and validation procedures Human oversight mechanisms AI ecosystem governance Organizations that strategically implement both standards build a strong foundation. This approach helps achieve high performance standards across multiple disciplines and ensures success in today’s ever-changing technological landscape. Core Structure of the ISO/IEC 42001 AI Management System Standard Image Source: Johner Institute ISO/IEC 42001 uses a systematic framework that helps organizations handle AI responsibly throughout its lifecycle. The standard works like other ISO management systems. It blends core clauses with detailed annexes to create a complete governance model for artificial intelligence systems. Clause 4–10 Overview: Context to Improvement Seven operational clauses (4-10) make up the foundation of ISO/IEC 42001. These clauses follow the Plan-Do-Check-Act method that many organizations with management systems already know well. This cycle helps systems adapt to new AI technologies and risks. Clause Focus Purpose 4: Context of the Organization Scope definition Define AI system boundaries and understand stakeholder expectations 5: Leadership Management commitment Demonstrate leadership commitment through clear policies and accountability 6: Planning Risk assessment Identify AI risks/opportunities and conduct impact assessments 7: Support Resource allocation Ensure adequate resources, competencies, and documentation 8: Operation Implementation Establish AI lifecycle controls reflecting principles like fairness and privacy 9: Performance Evaluation Monitoring Regularly assess AIMS effectiveness through audits and reviews 10: Improvement Continual enhancement Implement corrective actions based on evaluation results These clauses work together as a comprehensive system that fits with existing organizational processes. The standard gives you a practical framework to handle AI-related risks and opportunities across your organization, rather than focusing on specific AI applications. Annex A Controls: Risk, Bias, and Oversight Annex A works as the operational core of ISO/IEC 42001. It offers 38 specific controls under 10 control objectives that bring an AI Management System to life. These controls tackle key aspects throughout the AI lifecycle: AI Policies (A.2): Establishes policies for responsible AI development and use Internal Organization (A.3): Defines roles, responsibilities and reporting mechanisms Resources for AI Systems (A.4): Manages tangible and intangible resources essential for AI Assessing Impacts (A.5): Assesses AI systems’ effects on individuals and society AI System Lifecycle (A.6): Guides responsible development from requirements to maintenance Data for AI Systems (A.7): Addresses data quality, preparation, and transformation Information for Interested Parties (A.8):
AI Data Governance: Provenance, Quality, and Model Lineage
Teams that can’t explain their data’s origin, changes, or results face AI systems that simply don’t work. This vulnerability destroys trust and makes AI applications less effective in industries of all types. AI data governance tackles this challenge head-on by creating a well-laid-out framework that manages information throughout its lifecycle. Data lineage reveals data’s journey and transformations across systems. It provides detailed audit trails that track every change. Data provenance shows where data originated and its complete history. These elements are the foundations of responsible AI governance. AI systems become ‘black boxes’ without reliable provenance mechanisms. Users, regulators, and affected communities can’t see how training and analyzed data transform. This piece dives into how data lineage and provenance complement each other to maintain data quality and integrity. A clear data provenance framework helps organizations cut redundancy, control quality better, and create trustworthy AI systems. Data lineage becomes your AI pipeline’s backbone, and reproducibility transforms from a challenge into a natural habit. Defining Data Lineage, Provenance, and Their Role in AI Governance The way data flows through AI systems are the foundations of good governance. Data lineage and provenance each play unique but complementary roles that help build trustworthy AI systems. Let’s get into what these concepts mean and how they work within AI governance frameworks. What is Data Lineage? (Definition and Meaning) Data lineage tracks the complete experience of data from its origins to where it is now. The tracking documents how data moves and changes in systems and processes of all sizes. Organizations can use this visual map to understand data flows, dependencies, and transformations throughout their data pipeline. Data lineage answers basic questions like “Where did this data originate?”, “What transformations has it undergone?”, “Where does it move next?”, and “Who uses it and for what purpose?”. Users can observe and trace different touchpoints along the data experience and prove it right for accuracy and consistency. Data lineage includes several critical components: Origins: Shows where and when data was created or captured, and where it’s managed to keep (both internal and external sources) Characteristics: Describes what the data means in business terms (business metadata) and technical terms (technical metadata) Movements: Documents where data has been across hybrid ecosystems, from source to staging, to data warehouses and lakes, to analytics tools Transformations: Records how data was altered during its experience, including translations, quality rules, and reference data values Users: Identifies who or what accesses the data and for what reasons Data lineage works as a vital troubleshooting tool beyond documentation. Teams can analyze root causes of data quality issues, track errors, and assess the effects of proposed changes. On top of that, it gives the transparency needed to meet regulatory compliance in industries of all types. What is Data Provenance? (Definition and Use Cases) Data provenance zeroes in on the historical record of data by capturing its derivation history from original sources. Lineage maps technical connections, but provenance highlights authenticity and integrity. It documents who created the data, when it was created, what changes were made, and by whom. Data provenance answers questions like “Who created the data and when?”, “What changes have been made to the data and by whom?”, and “What is the original source of the data?”. This historical context builds credibility and traceability for data assets throughout their lifecycle. Data provenance comes in two main classes: Backward provenance (retrospective): Tracks data history by identifying origin, transformations, and movement Forward provenance (prospective): Records how data will move and transform in future workflows Data provenance helps many industries. Healthcare teams use provenance tracking to record patient data accurately from original collection through various changes. Financial institutions need provenance to audit transactions and trace them back to their origins. Scientific researchers rely on provenance to ensure their experiments can be validated and reproduced. Data provenance serves as reliable infrastructure for AI systems, maybe even the most important part. AI systems become “black boxes” without reliable provenance mechanisms. The origins and transformations of training data stay hidden from users, regulators, and affected communities. Data Lineage vs Data Provenance: A Comparative View People often use these terms interchangeably, but data lineage and provenance serve different purposes in governance frameworks: Aspect Data Lineage Data Provenance Primary Focus Technical flow and transformations of data Origin, authenticity, and historical context Scope Journey and transformations History and authenticity Key Questions Where data flows and how it changes Where data originated and who modified it Typical Users Data engineers, ML engineers Legal, compliance, marketing, data leaders Representation Flow maps, system-to-system diagrams Metadata logs, change logs, provenance chains Governance Role Ensures quality, prevents breakages Ensures audit-readiness and regulatory trust These concepts work together in AI governance frameworks despite their differences. Teams can’t maintain data lineage without knowing data’s provenance. Understanding provenance works best when lineage is clear. Together they create a detailed framework to track, validate, and govern data across AI systems. Both lineage and provenance play crucial roles in AI governance. Data and engineering teams use lineage to debug pipelines and understand dependencies. Legal and compliance teams rely on provenance to answer critical questions about data usage rights and audit requirements. Core Components of an AI Data Governance Framework A strong AI data governance framework needs several interconnected components that work together to ensure data integrity and trustworthiness. The foundational concepts of lineage and provenance support governance systems that combine metadata, stewardship, and technical tracking capabilities. Metadata Management and Data Catalog Integration Metadata—the “data about data”—forms the foundation of effective AI governance. A well-structured metadata enables automation by providing keys to anchor processes, integration points, and algorithms. It also formalizes the context that data managers and consumers need to identify, communicate, and apply data properly. Organizations without proper metadata must rely on institutional knowledge to work with their data. This creates inefficiencies and governance gaps. Effective metadata management involves: Technical metadata describing structure and format (schemas, table definitions, data types) Business metadata providing semantic meaning in plain language Operational metadata tracking runtime behavior and