CYBER SECURITY COMPLIANCE · ISO 27001
ISO/IEC 27001: 2022
ISMS Readiness, Implementation and Certification Support
ISO/IEC 27001: 2022 is the international standard for information security management systems, and it is the certificate most enterprise buyers ask for by name. The 2013 edition is gone: its transition window closed on 31 October 2025, and every valid certificate now sits on the 2022 edition. Elevate Consult builds the ISMS, closes the gaps, and prepares the evidence that Stage 1 and Stage 2 auditors actually test.
2026 UPDATE
What changed and what is coming
The 2013 edition is fully retired
The transition window for ISO/IEC 27001:2013 closed on 31 October 2025. Certificates issued against the 2013 edition are no longer valid. Any organization still presenting one in a vendor questionnaire has a problem to fix before the next enterprise review, not at the next recertification.
Climate change is now a mandatory context consideration
Amendment 1:2024 added a requirement to Clauses 4.1 and 4.2: organizations must determine whether climate change is a relevant issue for the ISMS. The amendment was immediately effective and applies to every certified organization. It does not require a climate program. It requires a documented determination, and auditors do ask for it.
The privacy extension became a standalone standard
ISO/IEC 27701 was republished on 14 October 2025 as a standalone privacy management system that no longer requires ISO 27001 underneath it. Organizations running both now have a structural decision to make rather than an automatic dependency.
WHAT IT IS
A certifiable management system, not a control checklist
ISO/IEC 27001 specifies the requirements for establishing, implementing, maintaining and continually improving an information security management system. The requirements sit in Clauses 4 through 10. Annex A lists 93 control themes that an organization selects from and justifies through a Statement of Applicability.
The distinction matters because most failed audits are not control failures. They are management system failures: no internal audit record, no management review with decisions, a Statement of Applicability that does not match the risk register.
CONTROL STRUCTURE
Ninety three controls across four themes
The 2022 edition restructured Annex A from 114 controls in fourteen domains into 93 controls across four themes, with eleven controls new to the edition.
Organizational controls
37 controls
Policies, roles and responsibilities, access rights, information labeling, supplier relationships, threat intelligence, cloud service use.
People controls
8 controls
Terms and conditions of employment, screening, security awareness and training, remote working, disciplinary process.
Physical controls
14 controls
Physical security perimeters, physical entry, secure areas, equipment siting and maintenance, cabling security, secure disposal.
Technological controls
34 controls
User endpoint devices, privileged access, configuration management, data masking, data leakage prevention, monitoring, secure development.
OUR PROCESS
Readiness through certification, built on what already exists
Elevate delivers ISO 27001 work in modules so an organization buys the level of support it needs rather than a fixed package.
Risk module
ISMS standards implementation, control scope definition, internal audit against Annex A, security impact and objectives analysis, internal and external vulnerability scanning, penetration testing, corrective action plan.
Governance module
ISMS documentation management policy, Statement of Applicability, ISMS charter and committee structure, ISMS manual creation and maintenance.
Incident module
Table-top exercises for disaster recovery, business continuity and cyber incident response.
Training module
Security awareness training licenses and maintenance, phishing simulation campaigns.
Reporting module
Information security objectives and metrics, ISO 27001 information security assessment report, consolidated list of findings.
ENGAGEMENT PHASES
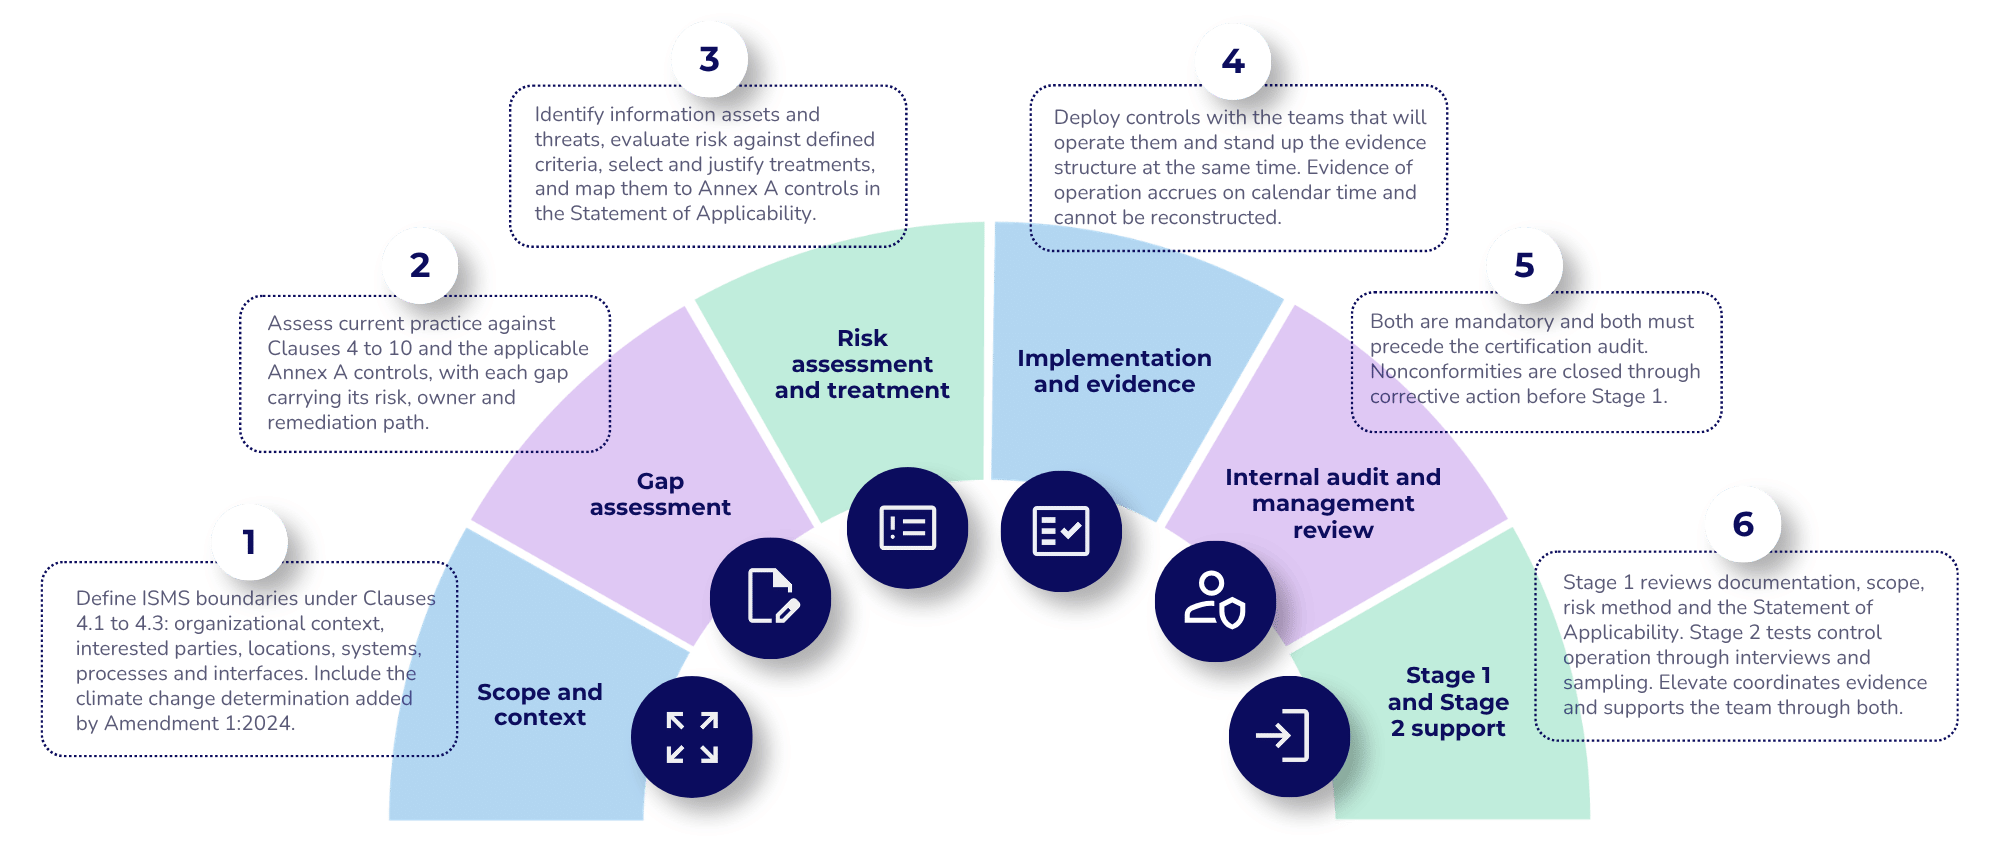
How the work runs
WHO THIS IS FOR
Roles Elevate works with on this standard
GET STARTED
Ready to build or transition your ISMS?
Whether the driver is a stalled enterprise deal, a 2013 certificate that has lapsed, or a first certification, Elevate Consult provides the scope definition, gap assessment, risk work and audit support that gets an organization to a certificate and keeps it there.
FAQ
Common Questions
🡪 Is ISO 27001:2013 still valid?
No. The transition period closed on 31 October 2025 and certificates issued against the 2013 edition are no longer valid. Organizations that have not transitioned need a gap assessment against the 2022 edition and a recertification audit rather than a surveillance visit.
🡪 How many controls are in ISO 27001:2022?
Annex A lists 93 control themes across four categories: 37 organizational, 8 people, 14 physical and 34 technological. Eleven controls were new to the 2022 edition. An organization does not implement all 93 by default. It selects and justifies them through a Statement of Applicability tied to its risk assessment.
🡪 What does the 2024 climate amendment require?
Amendment 1:2024 added a requirement to Clauses 4.1 and 4.2 that organizations determine whether climate change is a relevant issue for the ISMS and consider the expectations of interested parties on the subject. It was immediately effective. It does not mandate a climate program, but it does require a documented determination that auditors will ask to see.
🡪 What is the difference between Stage 1 and Stage 2?
Stage 1 is a readiness and documentation review covering scope, policies, risk methodology, risk register and Statement of Applicability. Stage 2 tests real-world effectiveness through interviews, control sampling and evidence over time. Passing Stage 2 produces the certificate, followed by annual surveillance audits across a three-year cycle.
🡪 How long does ISO 27001 certification take?
Typical end-to-end timelines run from roughly three to twelve months depending on scope, existing maturity and resourcing. Two constraints do not compress with budget: internal audit and management review must actually happen before the certification audit, and evidence of control operation accrues on calendar time.
🡪 How does ISO 27001 relate to ISO 27701 and ISO 42001?
All three are management system standards sharing the same Clause 4 to 10 structure, so governance, risk and evidence workflows can be run once rather than three times. ISO 27001 covers information security, ISO 27701 covers privacy and became standalone in October 2025, and ISO 42001 covers AI management systems. Organizations carrying more than one should integrate rather than duplicate.