
CYBER SECURITY COMPLIANCE · CMMC COMPLIANCE AS A SERVICE
CMMC Compliance as a Service
Ongoing Readiness, Evidence Upkeep and the Annual Affirmation Cycle
The annual affirmation survived the Phase 2 suspension. Every year a senior official signs an assertion about the organization’s compliance with 110 requirements, and every year the environment has drifted since the last time anyone checked. Compliance as a Service exists for that gap: documentation that stays current, evidence that accumulates rather than being reassembled, open items that close, and a readiness position that does not have to be rebuilt before each signature.
2026 UPDATE
What survived the suspension
The 2022 edition restructured Annex A from 114 controls in fourteen domains into 93 controls across four themes, with eleven controls new to the edition.
The affirmation is annual and unchange
A current NIST SP 800-171 self-assessment posted in SPRS with a senior official affirmation remains a condition of eligibility. The suspension removed the third-party assessment, not the recurring obligation to assert compliance and stand behind it.
Environments drift between milestones
Staffing changes, provider changes, architecture updates and new systems all move the boundary and the control set. An SSP accurate at the last assessment describes a system that no longer exists, and that gap is invisible until someone looks.
Evidence accrues on calendar time
This is the constraint that no budget fixes. A control configured last week and a control configured nine months ago produce the same screenshot and very different defensibility. An organization that lets evidence collection lapse cannot recover the gap later.
If certification returns, position matters
A CMMC Reform Task Force delivered recommendations to the Department of War CIO in mid-September 2026, with a public report expected shortly after. Whatever emerges, an organization that maintained documentation and evidence through the pause is in a materially different position from one that stopped.
WHAT IT IS
An operating rhythm, not a retainer
CMMC Compliance as a Service creates an ongoing cadence for documentation upkeep, evidence organization, accountability and readiness review. Instead of treating compliance as a scramble before a milestone, it maintains the position between them.
It suits teams that want support staying aligned as environments, responsibilities and business needs change, without building a full internal compliance function.
WHAT IT MAINTAINS
The work that gets deprioritized after the initial push
The realities that make CMMC harder to sustain than to start are ordinary: the person who owned an item left, the provider changed, nobody updated the diagram, the evidence folder stopped being filled.
Documentation upkeep
SSP, policies, procedures
Keeping the System Security Plan, policies, procedures and related artifacts current against the environment as it actually operates.
Open item tracking
Owners and deadlines
Remediation items, action owners and due dates tracked to closure rather than to the next status meeting.
Change support
Scope, systems, personnel, providers
Identifying when a business, technology, staffing or provider change creates new compliance risk or moves the boundary
Evidence management
Organization and review readiness
Evidence collected continuously rather than assembled before a deadline, organized so it supports the objective it is cited against.
Readiness reviews
Recurring checkpoints
Regular reviews covering what changed, what needs attention and what could affect the next affirmation.
Affirmation preparation
The annual signature
Assembling the basis on which the senior official signs, so the assertion rests on current evidence rather than on the last assessment
WHO IT FITS
Organizations past the start line
This is not a starting service. It suits organizations that have already done the heavy lift and need a sustainable way to hold the position.
Recurring readiness reviews
Regular checkpoints reviewing what has changed, what needs attention and what could affect ongoing readiness before it affects an affirmation.
Owner and action tracking
A structured way to follow open items, responsibilities, deadlines and next steps across the programme.
Strategic compliance guidance
Practical input on evolving priorities, documentation questions and readiness concerns, including how programme changes affect the organization’s position.
Documentation and evidence support
Guidance keeping compliance materials current, organized and defensible, with evidence accumulating continuously.
Change and risk visibility
Support identifying when business, technology, staffing or provider changes create new compliance risk.
Connected support
Where deeper execution is needed, Elevate supports End-to-End Managed Services and Mock Assessment engagements.
ENGAGEMENT PHASES
How the work runs
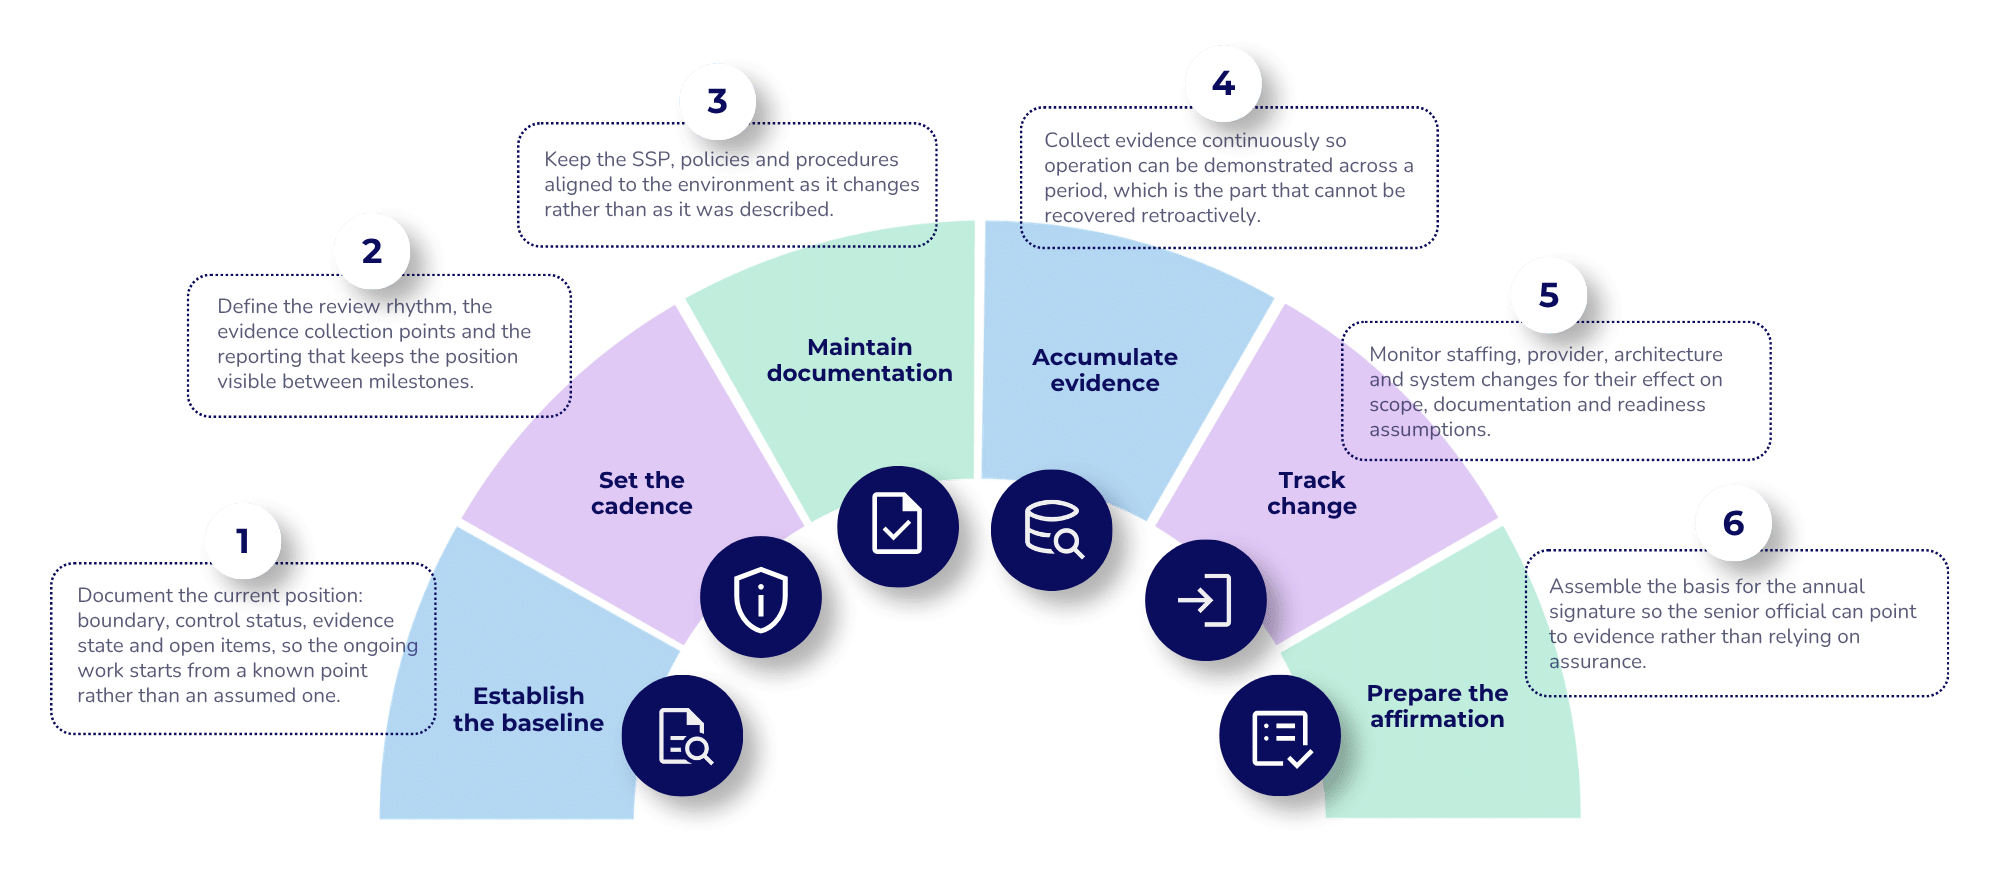
WHO THIS IS FOR
Roles Elevate works with on this standard
GET STARTED
Ready to stop rebuilding your position every year?
Elevate Consult maintains the documentation, evidence and accountability that make the annual affirmation something your senior official can sign against evidence, and keeps the programme from drifting between milestones.
FAQ
Common Questions
🡪 Do we still need ongoing compliance support with certification suspended?
For most organizations, yes, and arguably more than before. The annual senior official affirmation remains a condition of eligibility and carries False Claims Act exposure. With no assessor testing the claim, the quality of the documentation and evidence behind the signature is the only thing standing between the organization and that exposure.
🡪 How is this different from a one-time readiness project?
A readiness project prepares for a specific milestone. Compliance as a Service maintains the position afterwards through a consistent operating rhythm, which matters because environments drift and evidence accrues on calendar time that cannot be recovered.
🡪 How is this different from End-to-End Managed Services?
Compliance as a Service is the ongoing maintenance layer: documentation, evidence, recurring reviews, accountability and support through change. End-to-End Managed Services is broader and more execution-heavy, with deeper involvement in remediation coordination, implementation support and day-to-day programme movement, including enclave deployment where scope reduction is the right answer.
🡪 What happens if certification requirements return?
An organization that maintained documentation, evidence and boundary discipline through the pause is materially better positioned than one that stopped. A CMMC Reform Task Force delivered recommendations to the Department of War CIO in mid-September 2026. Whatever emerges, the underlying 110 requirements and the DFARS obligation behind them were never suspended.
🡪 Can you help when our environment changes?
That is much of the point. Staffing shifts, new providers, architecture updates and system changes all affect scope, documentation and readiness assumptions, and they usually happen without anyone flagging the compliance implication. The service exists to catch those before the next affirmation rather than after.
🡪 Who is this best for?
Organizations without a full-time internal compliance programme manager, teams with limited bandwidth, and contractors that want a structured way to keep documentation, evidence and accountability on track between milestones rather than rebuilding the position each year.