CYBER SECURITY COMPLIANCE · GOVRAMP
GovRAMP Audit Readiness and Authorization
Core, Ready, Provisional and Authorized, plus Continuous Monitoring
GovRAMP standardizes cloud security verification for state, local, tribal and educational government buyers, built on NIST SP 800-53 Revision 5. Two things changed the calculation for cloud providers in the last year: FedRAMP now recognizes GovRAMP as an approved alternative security framework, so state-level work counts toward federal authorization, and a growing set of states have made verification a procurement condition rather than a preference. Elevate Consult scopes the system, closes the control gaps, and guides providers from Core through Authorized and into continuous monitoring.
2026 UPDATE
What changed and what it means now
Reciprocity now runs in both directions
FedRAMP’s updated Class A certification rules recognize GovRAMP at any impact level as an approved alternative security framework. State-level verification is no longer only a SLTT play: it can serve as the prior audit that opens a federal path. That inverts the sequencing decision for providers who assumed federal first, state second.
Core opened an entry point without a 3PAO
Core status, introduced in May 2025, covers 60 foundational controls selected from NIST SP 800-53 Revision 5 and mapped to MITRE ATT&CK. It does not require a third-party assessment, which makes it the accessible first milestone for smaller and emerging vendors rather than a scaled-down version of Ready.
The AI Security Task Force moved into implementation
Launched in April 2025, the Task Force entered its 2026 implementation phase: generative AI treated as a significant change notification, a self-reporting AI addendum, AI notation on the Authorized and Progressing Product Lists, and alignment with NIST AI RMF updates and overlays to NIST 800-53. Providers shipping AI features into SLTT should expect to disclose them.
StateRAMP became GovRAMP on 14 February 2025
The rebrand reflected a membership that had outgrown the word state. StateRAMP Inc. remains the legal entity operating as GovRAMP, so existing memberships and authorizations carried over unchanged and prior StateRAMP authorizations remain recognized. Update bid libraries and supplier questionnaires that still say StateRAMP, because a tender response is read by a person.
State mandates are multiplying
Utah’s requirements took effect in 2025, North Carolina’s in April 2026, and Nevada’s on 1 July 2026. Texas handles GovRAMP through TX-RAMP reciprocity, granting Level 2 certification to products holding GovRAMP Core, Ready or Authorized status. The federal JAB Attestations pathway closed to new applications on 1 January 2026 and the list retired on 1 June 2026
WHAT IT IS
A verification program, not a certification body
GovRAMP is a nonprofit membership organization that standardizes cloud security requirements across state, local, tribal and educational government entities. Cloud service providers undergo third-party assessment against NIST SP 800-53 Revision 5 controls, with authorization levels corresponding to data sensitivity, and verified products appear on the Authorized Product List that procurement teams reference.
The practical value is reuse. Control work done for GovRAMP maps across FedRAMP, NIST SP 800-171, TX-RAMP, CMMC, ISO 27001 and SOC 2, which turns a single evidence set into answers for multiple buyers rather than a separate project per framework.
THE STATUS LADDER
Verification milestones, and what each one actually costs
GovRAMP is a ladder rather than a gate. A provider can demonstrate progress at each rung, which matters because SLTT buyers use the Progressing Product List during evaluation, not only the Authorized list.
Snapshot
40 controls
A scored security posture assessment. The entry point for providers who want a baseline before committing to a path.
Core
60 controls, no 3PAO
Foundational controls drawn from NIST SP 800-53 Revision 5 and mapped to MITRE ATT&CK. No third-party assessment required, which is what makes it accessible.
Provisional
300+ controls, sponsor required
Exceeds the minimum requirements with a government sponsor in place.
Progressing Snapshot
40 controls
Enrolled in the program and working toward an initial snapshot score. Visible on the Progressing Product List.
Ready
80 controls, 3PAO required
Meets the minimum security requirements and documentation baselines, verified by a third-party assessment organization. No government sponsor needed.
Authorized
300+ controls, sponsor required
Satisfies all requirements with a government sponsor. The full authorization that appears on the Authorized Product List.
OUR PROCESS
From scoping through continuous monitoring
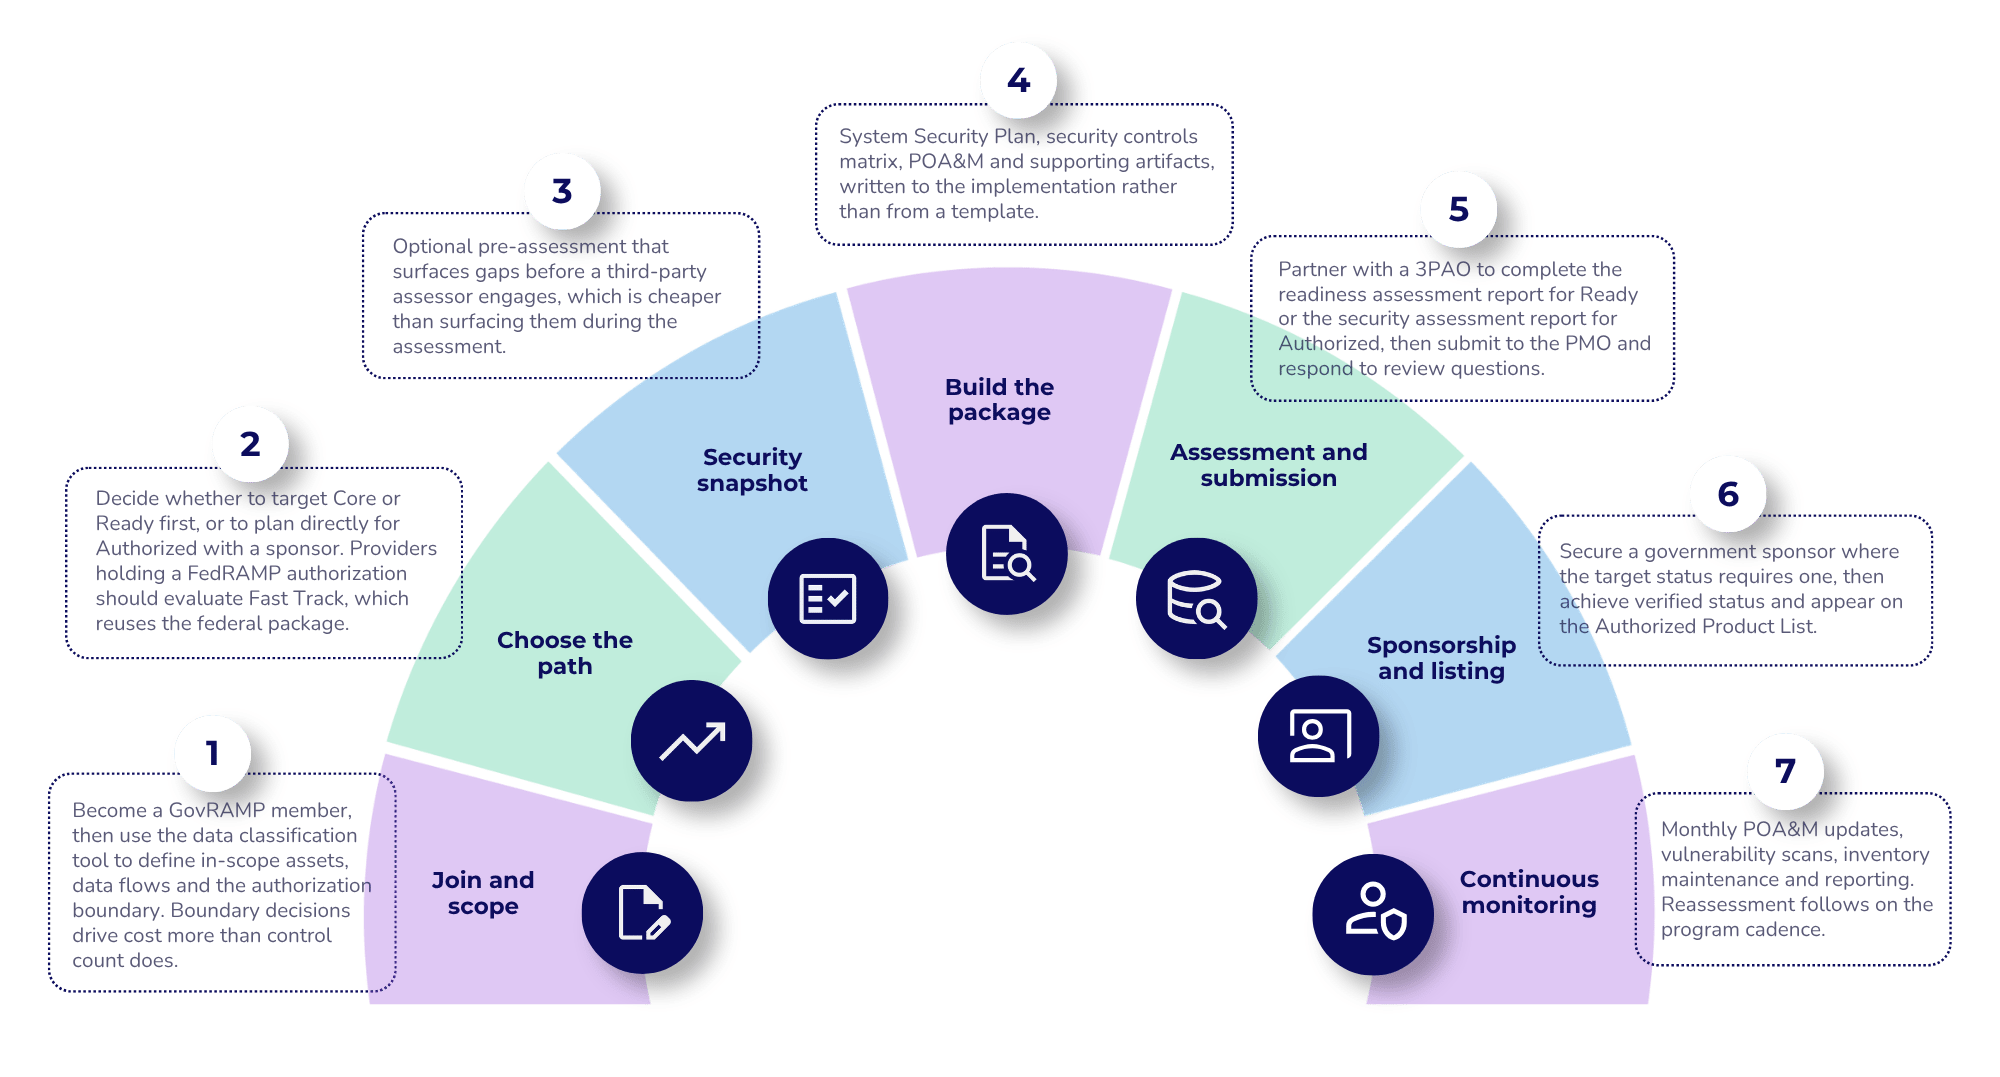
Elevate Consult supports providers across the full authorization lifecycle, and the sequencing decision is the first one that matters: Core and Ready require no sponsor, Provisional and Authorized do.
Readiness and gap assessment
Scope the system boundary, run a control-by-control gap review against the target status, and produce a prioritized POA&M.
3PAO coordination
Prepare teams for assessment, manage evidence requests, and resolve findings before they become schedule risk.
Continuous monitoring
Establish monthly reporting, vulnerability scanning cadence, ticketing workflows and change control that survive the first reassessment.
Documentation and evidence
Author the System Security Plan, security controls matrix, readiness assessment report or security assessment report, POA&M, test plans, diagrams and inventories.
Sponsorship strategy
Advise on the sponsorship approach, whether through a government member or the Approvals Committee, for providers targeting Provisional or Authorized.
AI and privacy add-ons
Align with AI Security Task Force priorities including significant change notification and the self-reporting addendum, plus ISO 42001 and privacy control mapping.
ENGAGEMENT PHASES
How the work runs
WHO THIS IS FOR
Roles Elevate works with on this standard
GET STARTED
Ready to start your GovRAMP path?
Whether the target is Core as a first milestone, Ready for a specific state requirement, or full Authorized status with a sponsor, Elevate Consult builds the roadmap, closes the gaps and guides you through 3PAO assessment and continuous monitoring.
FAQ
Common Questions
🡪 Is GovRAMP the same as StateRAMP?
Yes. StateRAMP rebranded to GovRAMP on 14 February 2025. StateRAMP Inc. remains the legal entity operating as GovRAMP, so memberships, authorizations and the product lists carried over unchanged, and prior StateRAMP authorizations remain recognized. Internal documents and bid libraries that still say StateRAMP should be updated, because the redirect works but a tender response is read by a person.
🡪 Do we need a government sponsor?
Only for Provisional and Authorized status. Snapshot, Progressing Snapshot, Core and Ready do not require sponsorship, which is why Core and Ready are the practical first targets for providers without an existing government relationship.
🡪 What is GovRAMP Core?
A status introduced in May 2025 covering 60 foundational controls selected from NIST SP 800-53 Revision 5 and mapped to MITRE ATT&CK. It does not require a third-party assessment. It exists as an accessible entry point for smaller and emerging vendors and as a demonstrable milestone on the path toward Ready or Authorized.
🡪 We have FedRAMP. Can we fast-track GovRAMP?
Yes. Existing FedRAMP authorization, provisional authorization or Ready status can accelerate GovRAMP through the Fast Track program, which reuses the federal package. Membership, PMO review and separate continuous monitoring still apply, so Fast Track shortens the work rather than eliminating it.
🡪 Does GovRAMP help with FedRAMP?
It now does, which is a recent change. FedRAMP’s updated Class A certification rules recognize GovRAMP at any impact level as an approved alternative security framework, meaning a GovRAMP audit can serve as the prior audit that a federal path requires. Providers who assumed federal first and state second should revisit that sequencing.
🡪 Is GovRAMP mandatory?
GovRAMP itself is a voluntary program, but individual states have made verification a procurement condition. Utah’s requirements took effect in 2025, North Carolina’s in April 2026 and Nevada’s on 1 July 2026. Texas operates its own statutorily mandated program, TX-RAMP, which grants Level 2 certification reciprocally to products holding GovRAMP Core, Ready or Authorized status.