CYBER SECURITY COMPLIANCE · FedRAMP
FedRAMP Consulting for Federal Cloud Providers
Rev5 Completion, 20x Architecture and CR26 Path Selectio
The next hard FedRAMP deadline is not the one most providers are watching. The VDR and VER vulnerability rules become mandatory on 7 December 2026, pulled forward from June 2027 to align with CISA Binding Operational Directive 26-04, and legacy monthly scanning no longer suffices on its own. The grace period ends 7 March 2027, after which non-compliant certifications are revoked. Elevate Consult covers the programme as it exists now under the Consolidated Rules for 2026: Rev5 completion and transition for programmes in flight, and 20x-ready architecture for organizations entering federal markets from zero.
2026 UPDATE
The CR26 calendar, in the order it arrives
7 December 2026: VDR and VER become mandatory
The vulnerability detection and response rules apply to all certifications. The date was pulled forward from June 2027 to align with CISA Binding Operational Directive 26-04. Legacy monthly scanning alone no longer satisfies the requirement. This is the next hard deadline and it is the one most providers have not scoped.
7 March 2027: the VDR and VER grace period ends
Certifications not compliant after this date are revoked with public notice. FedRAMP has stated the default grace period is a hard deadline that applies regardless of notification, corrective action or progress.
Already passed in 2026
FedRAMP Ready retired on 28 July 2026 with no new submissions accepted. The Class A pipeline opened 3 August, the Ready Conversion and Lost Sponsor pipelines on 10 August, and the Class B and Class C pipelines on 31 August. Providers still presenting FedRAMP Ready as a sales credential need a conversion plan rather than a talking point.
1 January 2027: CR26 becomes mandatory for all stakeholders
Current Rev5 certifications must have adopted the rules by this date. The baseline rebuild requirement applies at a provider’s first independent assessment after it.
11 June 2027: no new Rev5 applications
FedRAMP stops accepting applications for new Rev5 Certifications. Existing Rev5 certifications remain active until at least 31 December 2028 unless FedRAMP is otherwise directed.
WHAT FedRAMP IS
A certification, and then an agency authorization
FedRAMP is the standardized federal approach to security assessment, certification and continuous monitoring for cloud services used by agencies. It sits under GSA with requirements grounded in NIST-based security expectations.
Under CR26 the language changed for a reason worth understanding. FedRAMP issues a FedRAMP Certification. A federal agency issues the Authority to Operate for its own system. Those are two different things and conflating them in a sales conversation with an agency buyer is noticeable.
NO LONGER A ONE-PATH DECISION
Rev5 or 20x, and the lanes are not reciprocal
FedRAMP in 2026 is a certification type decision rather than a compliance checklist. Providers must commit to one path, and the two are not interchangeable.
FedRAMP Rev5
Organizations already in flight
The documentation-heavy path most current providers know. Finish well, reduce rework, and prepare for transition. New applications stop 11 June 2027; existing certifications remain active until at least 31 December 2028.
FedRAMP Certified
The official label
Replaces FedRAMP Authorized across the board. FedRAMP issues the Certification; the agency issues the ATO for its own system.
Sponsorless certification
The Program path
The Joint Authorization Board no longer exists. The Program path allows qualifying providers to certify with no agency sponsor for Classes A, B and C.
FedRAMP 20x
Organizations starting from zero
Built on Key Security Indicators, machine-readable evidence and continuous validation rather than narrative documentation. Faster and less document-heavy for cloud-native providers with mature automation.
Certification Classes A to D
Replaced impact levels
Low, Moderate and High gave way to Classes A, B, C and D. Existing authorized providers carried over automatically without re-authorization.
FedRAMP Ready retired
28 July 2026
Ready and the Readiness Assessment are gone. Preparation is now advisory and engineering work a provider scopes itself, which is a change in who carries the risk of getting it wrong.
WHAT CHANGED UNDER CR26
Terminology, structure and evidence
The Consolidated Rules for 2026 consolidate a year of rolling changes into one rulebook valid through 31 December 2028, which gives providers the first realistic chance in years to plan a multi-year roadmap against a fixed target.
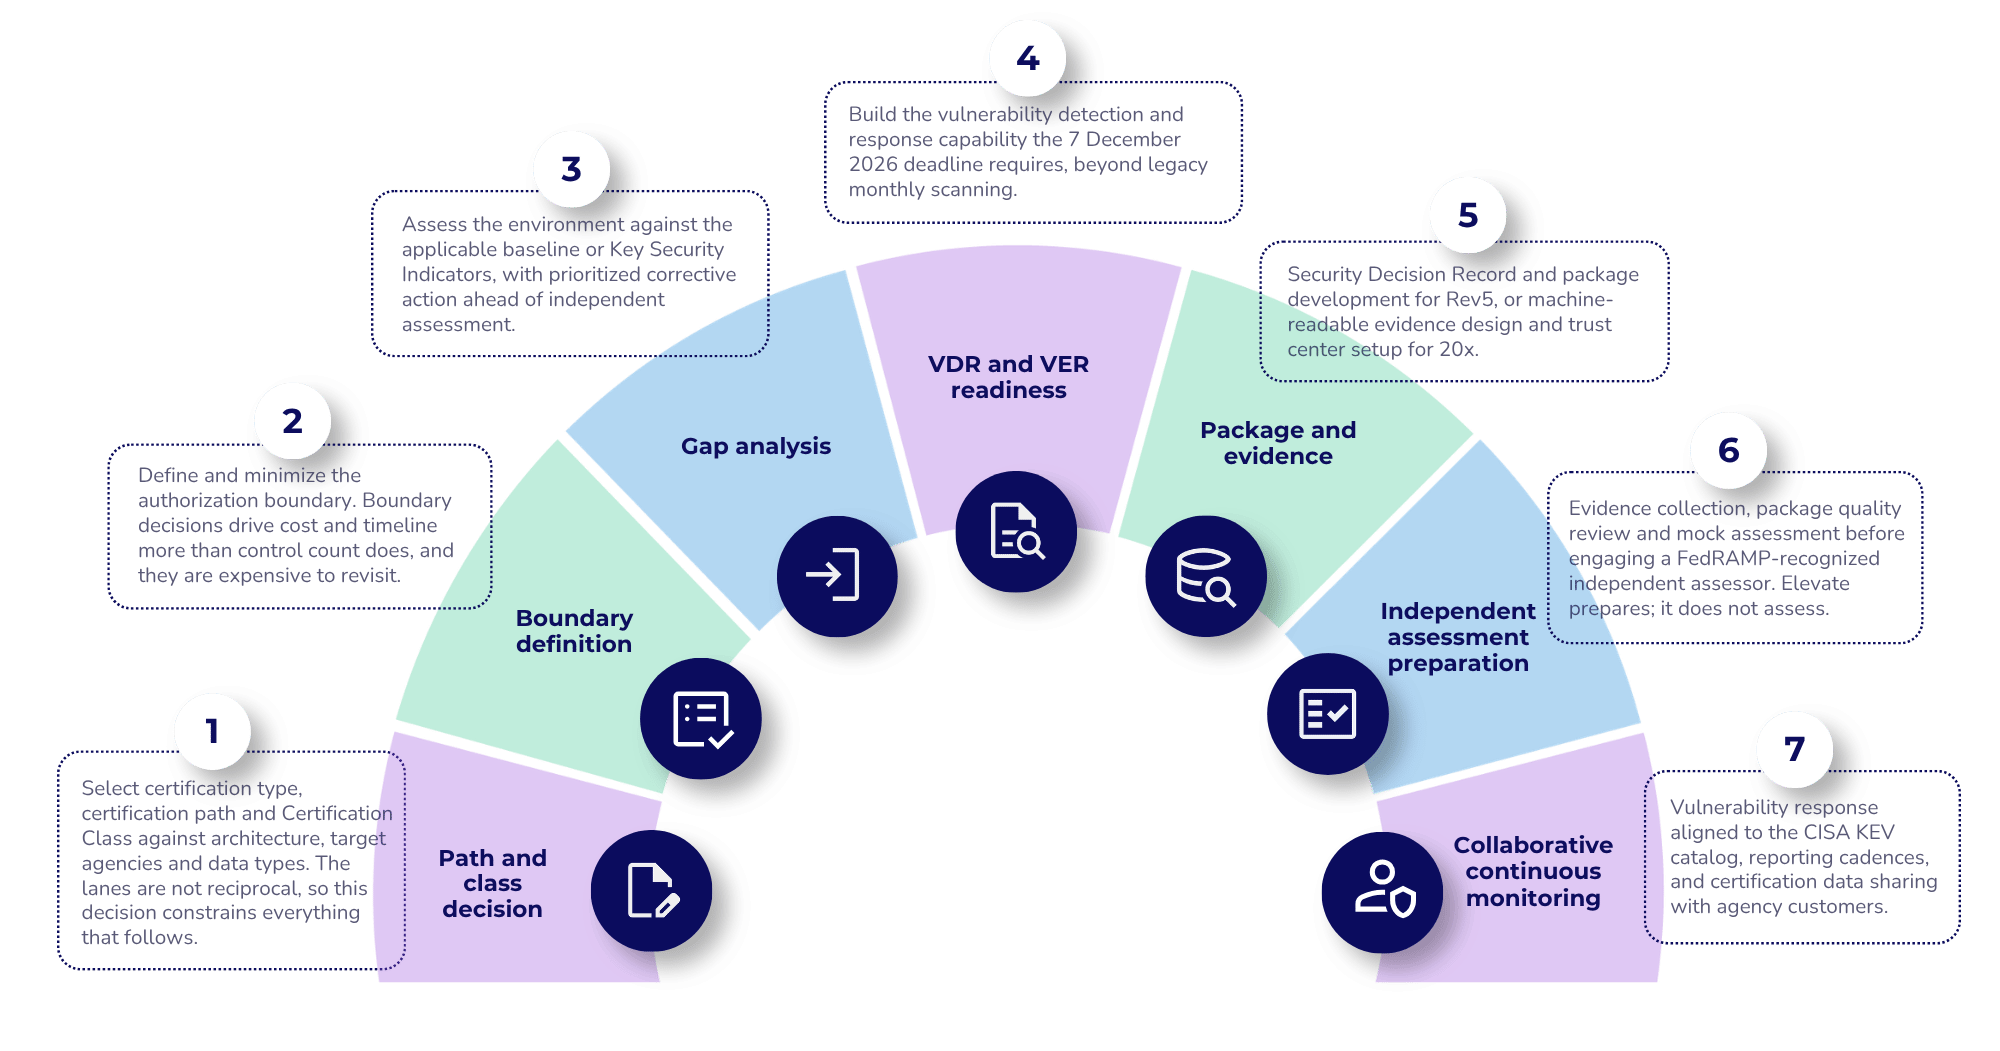
FedRAMP Certification Strategy and Scoping
Selection of certification type (FedRAMP 20x or Rev5), certification path (Program or Agency), and Certification Class (A through D) against your architecture, target agencies, and data types. Authorization boundary definition and minimization.
FedRAMP 20x Advisory
Key Security Indicator alignment, machine-readable evidence design, trust center setup, and continuous validation architecture.
Independent Assessment Preparation
Evidence collection, package quality review, and mock assessment ahead of engagement with a FedRAMP-recognized independent assessor. Elevate does not perform independent assessments.
FedRAMP Gap Analysis and Remediation Planning
Assessment of your current environment against the applicable FedRAMP baseline or Key Security Indicators, with prioritized corrective action plans ahead of independent assessment.
FedRAMP Rev5 Completion and Transition Strategy
Security Decision Record and package development, machine-readable package compliance, and transition planning toward FedRAMP 20x where appropriate.
Collaborative Continuous Monitoring Support
Vulnerability detection and response aligned to the CISA KEV catalog, reporting cadences, and ongoing certification data sharing with your agency customers, including monthly vulnerability scans and penetration test support.
ENGAGEMENT PHASES
How the work runs
WHO THIS IS FOR
Roles Elevate works with on this standard
GET STARTED
Already in Rev5 or starting from zero?
If you already started Rev5, Elevate helps you finish and transition ahead of the CR26 deadlines. If you are starting from scratch, Elevate helps you evaluate and build for 20x from the beginning.
FAQ
Common Questions
🡪 What is the next FedRAMP deadline we should be planning against?
7 December 2026, when the VDR and VER vulnerability rules become mandatory for all certifications. The date was pulled forward from June 2027 to align with CISA Binding Operational Directive 26-04, and legacy monthly scanning no longer satisfies the requirement on its own. The grace period ends 7 March 2027, after which non-compliant certifications are revoked with public notice.
🡪 Is FedRAMP 20x replacing Rev5?
Rev5 remains active for existing programmes and FedRAMP has said migration will not be forced. But FedRAMP stops accepting applications for new Rev5 Certifications on 11 June 2027, and existing Rev5 certifications remain active until at least 31 December 2028 unless FedRAMP is otherwise directed. 20x represents the modernization direction of the programme.
🡪 What is the official FedRAMP label now?
FedRAMP Certified. Under CR26 it is the single official designation, replacing FedRAMP Authorized. FedRAMP issues the Certification; a federal agency issues the Authority to Operate for its own system. The distinction matters in agency conversations.
🡪 Do we still need an agency sponsor?
Not for every path. The Joint Authorization Board no longer exists, and the Program path allows qualifying providers to certify with no agency sponsor for Classes A, B and C. Sponsorship requirements depend on the path and class selected, which is part of the strategy decision rather than a given.
🡪 Should a new provider start with Rev5 or 20x?
Starting from scratch, the stronger strategic recommendation is usually to evaluate 20x first and design for automation and machine-readable evidence from day one. The 11 June 2027 cutoff for new Rev5 applications weakens the default further. This is an advisory recommendation based on the public direction of the programme rather than a FedRAMP mandate.
🡪 What happened to FedRAMP Ready?
It retired on 28 July 2026 and no new submissions are accepted. The Readiness Assessment went with it. Preparation is now advisory and engineering work a provider scopes for itself, which shifts the risk of under-preparing onto the provider. Anything still resting on FedRAMP Ready as a sales credential needs a conversion plan to a full certification track.