Cyber Security Compliance · GLBA
GLBA Compliance and Safeguards Rule Services
Written Risk Assessment, Technical Safeguards and Program Validation
The FTC Safeguards Rule has been fully enforceable since 9 June 2023, with breach notification obligations following in May 2024, and it reaches far past banks. Mortgage lenders, auto dealers, tax preparers, investment advisers and Title IV higher education institutions all meet the FTC’s definition of a financial institution. The obligation most often missed is not a policy: it is the requirement to conduct annual penetration testing and semi-annual vulnerability assessments, or to implement continuous monitoring that achieves comparable outcomes. Elevate Consult builds and validates the full program.
2026 UPDATE
What the Rule actually requires
Nine program elements, not a policy document
Under 16 CFR Part 314, a covered institution’s written information security program must designate a Qualified Individual, base safeguards on a written risk assessment, implement specific technical safeguards, test them regularly, train the workforce, oversee service providers, keep the program current as risk evolves, maintain a written incident response plan, and require the Qualified Individual to report regularly to the board or senior leadership.
Eight technical safeguards flow from the risk assessment
Access controls, asset inventory, encryption of customer information, secure application development, multi-factor authentication, secure disposal, change management, and monitoring of user activity. Encryption applies both at rest and in transit, and multi-factor authentication is required for anyone accessing systems holding customer information.
Testing has a specific cadence
Covered non-bank financial institutions must conduct annual penetration testing and semi-annual vulnerability assessments, or implement continuous monitoring achieving comparable outcomes. This is among the most concrete obligations in the Rule and among the most frequently overlooked, and it is where the gap between a documented program and an actual security posture usually surfaces.
The program is ongoing, not a project
The Rule requires ongoing risk assessment, safeguard testing, vendor oversight, board reporting and program updates. A risk assessment completed once and filed does not satisfy it, and the Qualified Individual’s reporting obligation is what makes that visible at board level.
What GLBA requires
Three rules, one heavy
The Gramm-Leach-Bliley Act requires financial institutions to protect the security and confidentiality of customer financial information through three core rules. The Financial Privacy Rule governs how institutions collect and share nonpublic personal information. The Safeguards Rule mandates a written information security program. The pretexting provisions prohibit obtaining customer information under false pretenses.
For most institutions the Safeguards Rule carries the heaviest operational burden, because it is the one that requires demonstrable technical controls and recurring testing rather than disclosures.
Who is covered
A definition that reaches well past banks
The Safeguards Rule applies to any entity the FTC treats as a financial institution under GLBA. That definition reaches mortgage lenders and brokers, auto dealers, payday lenders, finance companies, insurance companies, tax preparation firms, investment advisers, Title IV higher education institutions handling federal student aid data, and finders that bring together buyers and sellers of financial products.
Consequences are meaningful. Civil penalties run in excess of fifty thousand dollars per violation and are adjusted annually for inflation, and individual officers and directors can face personal fines and imprisonment for willful violations.
Rationalizing the control set and automating evidence collection are the two responses with the largest effect, and both require someone willing to defend removing a control rather than only adding one.
Access controls
314.4(c)(1)
Authentication and access restriction, with periodic review of who has access to customer information and why.
Asset inventory
314.4(c)(2)
Identification and management of data, personnel, devices, systems and facilities, because a program cannot protect what it has not catalogued.
Encryption
314.4(c)(3)
Customer information encrypted both at rest and in transit, with the Qualified Individual approving any compensating control where encryption is infeasible.
Secure development
314.4(c)(4)
Secure development practices for in-house applications and evaluation procedures for externally developed applications.
Multi-factor authentication
314.4(c)(5)
Required for any individual accessing systems that hold customer information, not only for remote or privileged access.
Secure disposal
314.4(c)(6)
Disposal of customer information no later than two years after the last use, unless retention is required or targeted disposal is not reasonably feasible.
Change management
314.4(c)(7)
Procedures for evaluating the security impact of changes to systems holding customer information.
Activity monitoring
314.4(c)(8)
Monitoring and logging of authorized user activity, and detection of unauthorized access to or use of customer information.
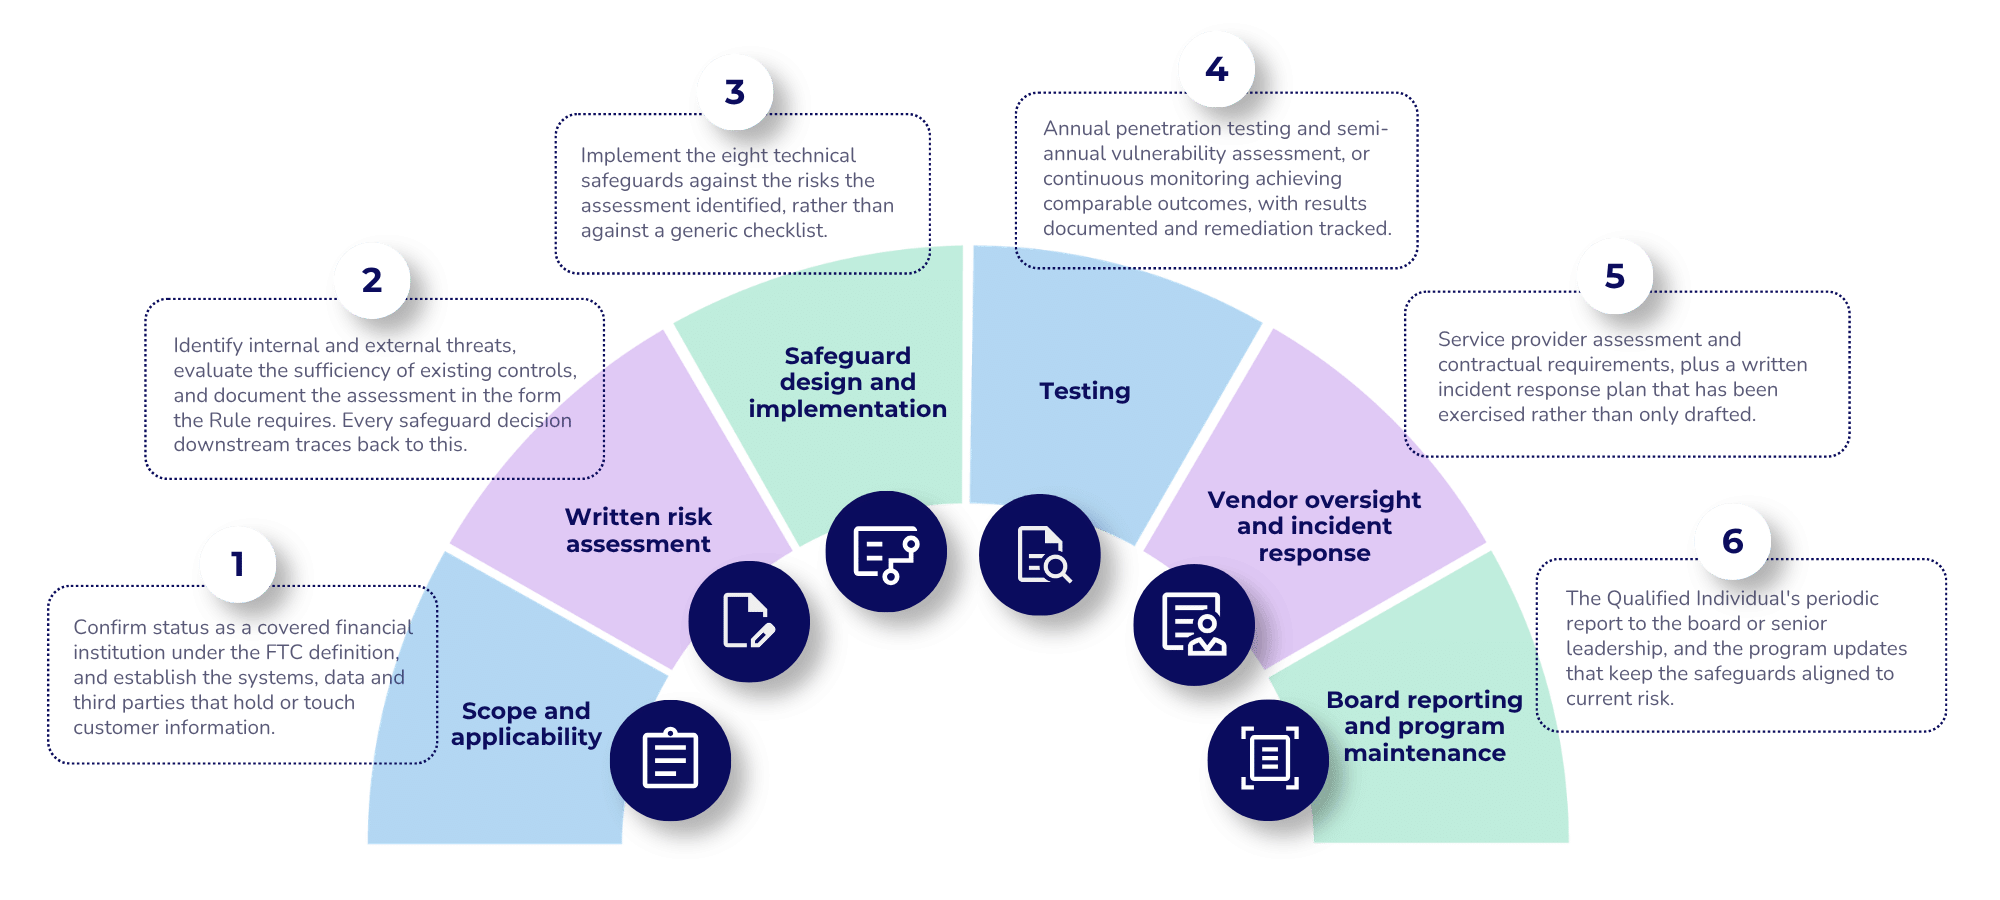
Our process
Risk assessment first, because everything follows from it
Elevate’s GLBA process aligns with GLBA 501(b) and the FTC requirements, and it starts with the written risk assessment because the Rule makes every safeguard downstream of it.
Written risk assessment
The foundation the Rule requires, identifying internal and external threats to customer information and evaluating the sufficiency of existing controls, documented so the safeguards that follow are traceable to it.
Vulnerability assessment
Review of existing vulnerability reports or scanning of in-scope assets, identification of weaknesses in current controls, and evaluation of the potential for unauthorized access, use or disclosure of customer information.
Penetration testing
The annual penetration testing the Rule requires for covered non-bank institutions, scoped to the systems that hold customer information.
Safeguard implementation
Design and implementation support across the eight technical safeguards, working with the teams that will operate them.
Service provider oversight
Vendor selection criteria, contractual requirements, and the periodic assessment of provider risk the Rule requires.
Incident response and board reporting
A written incident response plan meeting the Rule’s content requirements, and the reporting structure the Qualified Individual uses to brief the board or senior leadership.
ENGAGEMENT PHASES
How the work runs
WHO THIS IS FOR
Roles Elevate works with on this standard
GET STARTED
Ready to validate your Safeguards Rule program?
Elevate Consult conducts the written risk assessment, performs the annual penetration testing and semi-annual vulnerability assessments the Rule requires, implements the eight technical safeguards, and establishes the vendor oversight and incident response processes that hold up under FTC scrutiny.
FAQ
Common Questions
Who has to comply with the FTC Safeguards Rule?
Any entity the FTC treats as a financial institution under GLBA, which is a much broader category than banks. It includes mortgage lenders and brokers, auto dealers, payday lenders, finance companies, insurance companies, tax preparation firms, investment advisers, Title IV higher education institutions handling federal student aid data, and finders bringing together buyers and sellers of financial products.
What testing does the Safeguards Rule require?
Covered non-bank financial institutions must conduct annual penetration testing and semi-annual vulnerability assessments, or implement continuous monitoring that achieves comparable outcomes. This is one of the most concrete requirements in the Rule and one of the most frequently overlooked, and it is usually where the distance between a documented program and an actual security posture becomes visible.
What is a Qualified Individual?
The person a covered institution must designate to oversee, implement and enforce the information security program. The Rule does not require a specific title or certification, but it does require the individual to report regularly to the board or a senior officer, which means the role needs enough standing for that report to carry weight.
Is multi-factor authentication required for everyone?
For any individual accessing information systems that hold customer information, yes. The requirement is not limited to remote access or to privileged accounts. Where MFA is not used, the Qualified Individual must approve a reasonably equivalent or more secure access control in writing.
Does encryption apply to data at rest?
Yes, both at rest and in transit. Where encryption of customer information at rest is infeasible, the Rule permits the Qualified Individual to approve effective alternative compensating controls, but that approval has to be documented rather than assumed.
How often does the risk assessment need updating?
The Rule requires the program to be kept current as risk evolves, which means the risk assessment is periodic rather than one-time. In practice it should be revisited at least annually and whenever a material change occurs in systems, data, service providers or the threat environment, with the update documented so the safeguard decisions remain traceable.