Cybersecurity and Compliance for Technology Companies
SaaS, Cloud and Software Businesses Selling Into Regulated Markets
For a technology company, compliance is a sales problem before it is a security problem. Enterprise buyers, federal agencies and EU customers each ask for a different artifact, and the deal stalls until one exists. SOC 2 opens the enterprise door, FedRAMP and GovRAMP open the public sector, ISO 27001 travels internationally, and since 2026 the EU adds product and AI obligations that attach to the software itself rather than to the company. Elevate Consult builds one control set that answers all of them.
UPDATE
What changed for technology companies in 2026
EU Cyber Resilience Act reporting is live
Article 14 reporting obligations applied from 11 September 2026 for products with digital elements sold in the EU, including products already on the market. Manufacturers report actively exploited vulnerabilities and severe incidents on a 24 hour, 72 hour and 14 day cascade through ENISA's Single Reporting Platform. Full conformity and CE marking follow on 11 December 2027.
EU AI Act high-risk obligations moved to December 2027
Regulation (EU) 2026/1744 deferred Annex III high-risk obligations to 2 December 2027. What did not move: the Article 5 prohibitions and AI literacy obligation since February 2025, the general-purpose AI model rules since August 2025, and the Article 50 transparency obligations since August 2026, which reach any product with a chatbot or generative feature.
FedRAMP now recognizes GovRAMP
Updated Class A certification rules recognize GovRAMP at any impact level as an approved alternative security framework, so state and local work can count toward a federal path. That inverts the sequencing for providers who assumed federal first.
ISO 27001:2013 certificates expired
The transition window closed on 31 October 2025. A certificate issued against the 2013 edition is no longer valid, which is a problem to fix before the next enterprise security review rather than at the next audit.
WHO WE HELP
Software companies that sell to someone with a security questionnaire
SaaS and cloud providers, platform and infrastructure businesses, developer tools, embedded software and connected hardware vendors, and technology companies entering the public sector or the EU market for the first time.
The common pattern is that compliance arrives through procurement rather than through regulation. A buyer asks, a deal pauses, and the organization discovers that the artifact takes months to produce. Building the control set before the question arrives is the difference between a two week security review and a two quarter one.
WHERE THE PRESSURE COMES FROM
Four buyer types, four different artifacts
A technology company rarely needs one framework. It needs whichever one its next buyer recognizes, and the efficient answer is a single control set mapped across several.
SOC 2 is the default enterprise ask in North America. ISO 27001 travels better internationally and is the one European and Asian buyers recognize. Many companies need both, and the control overlap means the second costs far less than the first.
Enterprise buyers
The route to selling cloud services to federal agencies. Under the current consolidated ruleset the sponsor requirement changed and a prior audit from an approved alternative framework opens a faster path.
US federal agencies
Verification for the SLED market, now also recognized by FedRAMP as an approved alternative framework. Core status requires 60 controls and no third-party assessor, which makes it the accessible first milestone.
State and local government
Product-level cybersecurity obligations under the Cyber Resilience Act, AI-specific obligations under the AI Act, and sector obligations under NIS2 where the company operates in a listed sector. These attach regardless of where the company is headquartered.
EU market
ISO 42001 is the only accredited certification for an AI management system and increasingly appears in enterprise AI procurement. The NIST AI RMF carries a statutory affirmative defense under Texas TRAIGA.
AI-enabled products
More than twenty US states now have comprehensive privacy laws, and the EU and UK regimes diverged in February 2026. A single privacy program with jurisdiction-specific configuration beats a program per market.
Privacy across markets
HOW ELEVATE HELPS | SERVICES FOR TECHNOLOGY COMPANIES
One assessment, several answers
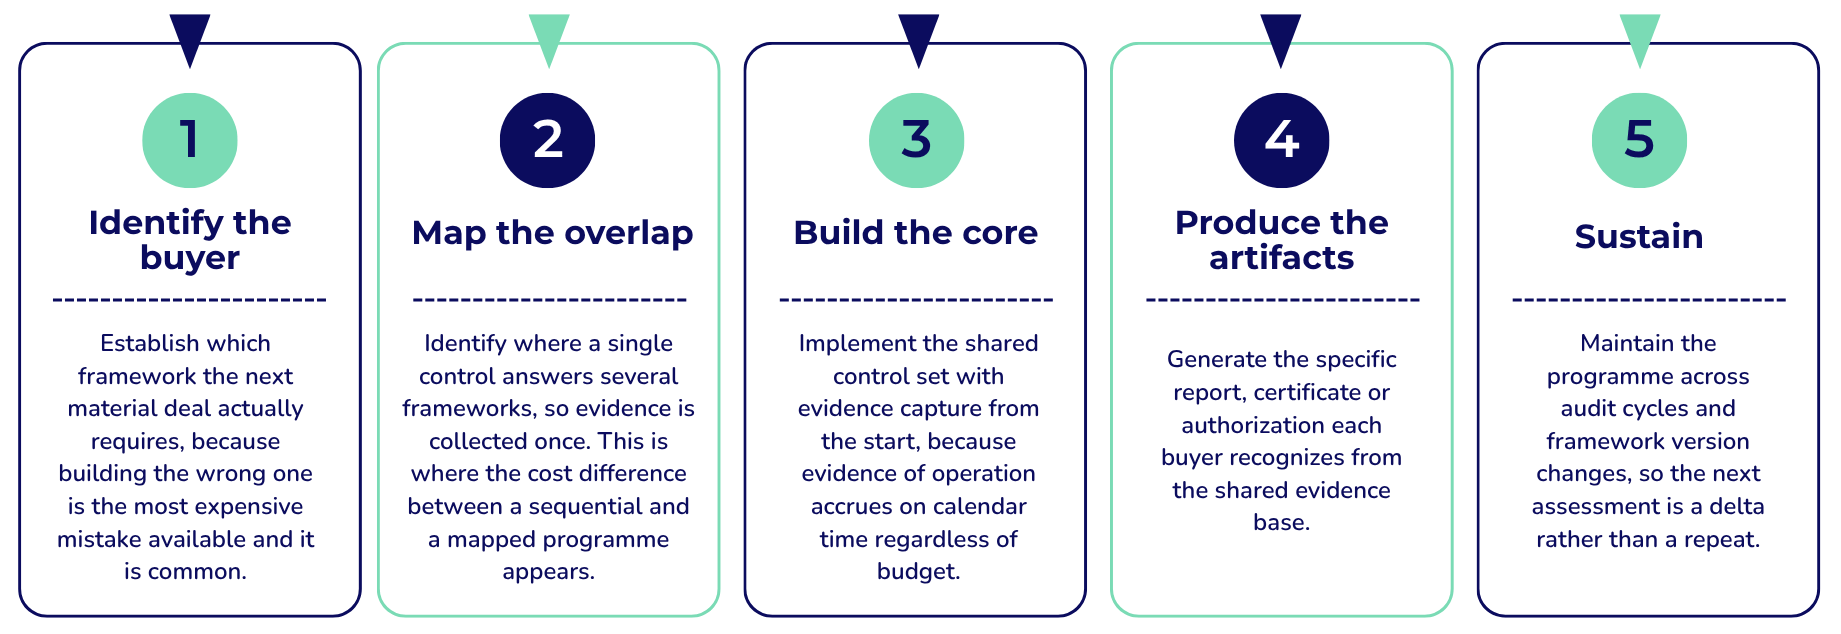
Elevate maps the overlapping controls once, then produces the specific evidence each framework and each buyer requires.
SOC 1 and SOC 2 readiness
Scoping, control design, evidence structure and audit support for the reports enterprise buyers request by name. See the SOC 1 and SOC 2 service pages.
ISO 27001 and ISO 27701
ISMS build or transition to the 2022 edition, and the standalone privacy management system available since the 2025 revision of ISO 27701.
FedRAMP and GovRAMP
Authorization path selection, documentation, 3PAO coordination and continuous monitoring for federal and SLED market access.
ISO 42001 and AI governance
AI management system certification readiness, NIST AI RMF programme build, and EU AI Act classification and high-risk controls for AI-enabled products.
EU CRA readiness
Article 14 reporting capability, vulnerability handling programme, SBOM discipline and the technical documentation for conformity assessment.
Penetration testing
Network, web and API, wireless and physical testing, scoped to satisfy the testing obligations the applicable frameworks carry rather than as a separate exercise.
Privacy programme
GDPR and UK GDPR, CCPA and the state patchwork, plus the website privacy and cookie compliance review that covers consent configuration and opt-out preference signals.
Virtual CISO
For companies without dedicated security leadership, the function that owns the programme between audits rather than only during them.
ENGAGEMENT PHASES
How the work runs
WHO THIS IS FOR
Roles Elevate works with on this standard
Elevate maps the overlapping controls once, then produces the specific evidence each framework and each buyer requires.
CTOs and engineering leaders
CISOs and security leads
Heads of enterprise sales
Compliance and GRC officers
Product managers shipping AI features
GET STARTED
Ready to stop losing deals to security reviews?
Elevate Consult identifies which framework your next buyer actually requires, maps the overlap across everything else on the roadmap, and builds one control set that produces the specific artifact each of them recognizes.
FAQ
Common Questions
🡪 Which framework should a SaaS company start with?
Whichever the next material deal requires. SOC 2 is the default enterprise ask in North America; ISO 27001 travels better internationally and is what European and Asian buyers recognize; FedRAMP or GovRAMP applies if the target market is government. Starting with the framework an internal team prefers rather than the one a buyer specified is the most common and most expensive misstep.
🡪 Do EU obligations apply if we are US-based?
Yes, where the product reaches the EU market. The Cyber Resilience Act applies based on whether a product with digital elements is made available on the EU market, not on where the manufacturer is headquartered. The EU AI Act applies to organizations inside and outside the EU that place AI systems or general-purpose AI models on the EU market or use them there.
🡪 We already have SOC 2. How much carries into ISO 27001?
A substantial amount on the control side, less on the structure side. SOC 2 is an attestation against Trust Services Criteria; ISO 27001 certifies a management system with mandatory internal audit, management review and a Statement of Applicability. The controls transfer; the management system scaffolding usually has to be built.
🡪 Does our product need CRA compliance?
If it is a product with digital elements made available on the EU market, yes. That covers software and hardware including remote data processing solutions and components sold separately. The reporting obligations under Article 14 have applied since 11 September 2026 and reach products already on the market. Full conformity assessment and CE marking are due by 11 December 2027.
🡪 When does ISO 42001 matter for a technology company?
When enterprise buyers start asking how AI features are governed, which is now routine in security reviews for AI-enabled products. It is the only accredited certification for an AI management system. Note that the certificate is only worth the accreditation behind the issuing body, and ISO/IEC 42006:2025 now governs that accreditation.
🡪 How do we avoid building the same control five times?
Map the frameworks against each other before collecting any evidence. Most of the overlap sits in access control, logging, change management, vendor management and incident response, which means one well-documented control answers several requirements. The saving comes from the mapping discipline rather than from the tooling.