Cyber Security Compliance · Banking Cybersecurity
Cyber Risk Assessment Services
Threat Inventory, Inherent and Residual Risk, and a Treatment Plan You Can Fund
Almost every compliance framework requires a documented risk assessment, and almost every organization produces something that does not satisfy one. A vulnerability scan is not a risk assessment. A control list is not a risk assessment. What auditors and regulators test for is a structured evaluation that identifies threats to specific assets, scores likelihood and impact, calculates risk before and after controls, and produces treatment decisions someone owned. Elevate Consult conducts that assessment against NIST SP 800-30, tailored to your operating environment.
2026 UPDATE
Where the requirement comes from
It is a named requirement in most frameworks you already carry
ISO/IEC 27001 requires an information security risk assessment process under Clause 6.1.2. The HIPAA Security Rule requires it at 45 CFR 164.308(a)(1)(ii)(A), which is the single most cited deficiency in OCR enforcement. The FTC Safeguards Rule requires a written risk assessment that every safeguard decision must trace back to. CMMC and NIST SP 800-171 require it. FedRAMP requires it. PCI DSS requires targeted risk analyses.
One assessment can satisfy several
The frameworks differ on documentation format and review cadence, not on the underlying discipline. An assessment scoped against every applicable requirement from the start answers several obligations; one scoped for a single framework usually has to be redone for the next.
It is periodic, not a project
Every framework that requires the assessment also requires it to be current. An assessment filed after completion and revisited a year later by reflex fails the same test it passed originally, because the environment moved and the document did not.
The output is a decision, not a score
A risk rating with no treatment decision attached is an observation. What an assessor tests is whether the organization decided to modify, retain, avoid, or share each risk, and whether someone owned that decision.
What a cyber risk assessment is
A structured evaluation, not a scan
A cyber risk assessment is a structured process that identifies and quantifies risks related to information and communication technology. Those risks arise from internal vulnerabilities, external threats, and environmental factors, and they attach to specific assets rather than to the organization in general.
The process analyzes each element to determine inherent and residual risk while aligning with, or improving, the organization’s overall risk management methodology. That lets an organization make informed decisions about security investment, policy change, and treatment strategy, and it improves both security posture and compliance position at the same time.
Key components
Threats tied to assets, scored against context
he approach combines industry standards with client-specific considerations rather than applying a generic template. The components below are what make the output defensible.
Threat inventory
Tied to your assets
A structured inventory identifying threats relevant to your specific assets, drawn from industry threat intelligence and categorized by likelihood and impact, so the assessment prioritizes plausible high-impact threats for your sector rather than a generic list.
Asset Category Values
Criticality, assigned at scoping
Assets carry a category value reflecting their criticality to the business. Two systems with the same vulnerability do not carry the same risk, and this is where that distinction enters the calculation.
Threat Impact Factors
Severity and probability
The factor accounts for the potential severity of a threat and its probability, and combines with the asset category value to produce inherent risk.
Inherent risk
Before controls
The initial risk profile calculated from Threat Impact Factors and Asset Category Values, representing exposure before existing controls are considered.
Residual risk
After controls
Control effectiveness scores applied to inherent risk, reflecting the security posture that actually exists rather than the one the control inventory implies.
Treatment decisions
Modify, retain, avoid, share
Each risk carries a decision and an owner. This is the part auditors test and the part most internally produced assessments leave blank.
Our methodology
Aligned to NIST SP 800-30
The process follows the NIST SP 800-30 risk management framework and is customized to the organization’s operating environment.
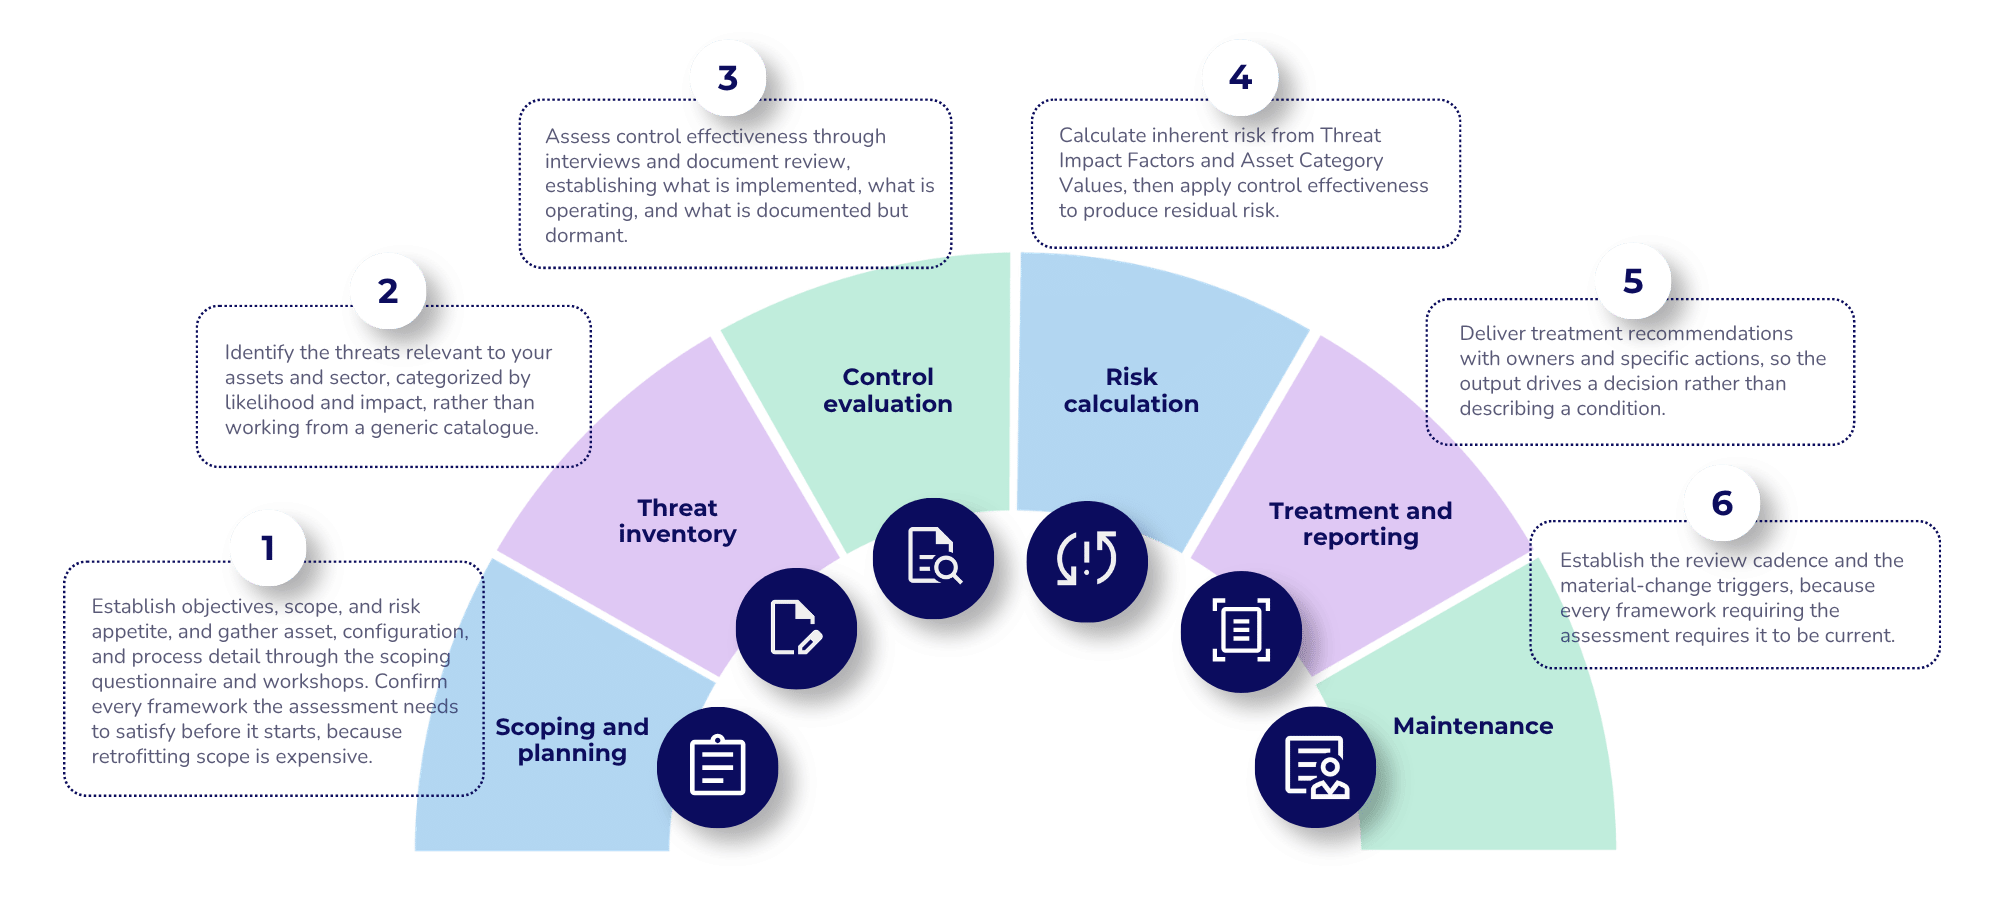
Scoping and planning
Objective definition establishing the scope and aligning it to your risk appetite and compliance requirements, plus a custom inventory and scoping questionnaire gathering detail on assets, configurations, and processes. Scoping workshops so the assessment reflects your actual environment, critical assets, and business objectives.
Control evaluation
Detailed interviews and document reviews assessing control effectiveness across the scope, identifying gaps and establishing where risk is genuinely being mitigated rather than assumed to be.
Threat likelihood and impact scoring
Qualitative scoring of probability and potential damage, calibrated to both industry standards and your organizational context, so the ratings mean something specific rather than defaulting to medium.
Inherent and residual risk calculation
Threat Impact Factors and Asset Category Values producing the initial profile, then control effectiveness scores producing residual risk.
Reporting and recommendations
Tailored treatment recommendations across modification, retention, avoidance, and sharing, with specific actions covering technology change, policy revision, and procedural improvement.
Multi-framework alignment
Scope the assessment against every framework that requires one, so a single exercise satisfies ISO 27001, SOC 2, HIPAA, the Safeguards Rule, CMMC, or FedRAMP rather than being repeated per obligation.
ENGAGEMENT PHASES
How the work runs
WHO THIS IS FOR
Roles Elevate works with on this standard
GET STARTED
Ready to produce an assessment that holds up?
Elevate Consult conducts the risk assessment against NIST SP 800-30, scoped to satisfy every framework that requires one, and delivers treatment decisions with owners rather than a risk rating with nothing attached to it.
FAQ
Common Questions
Which frameworks require a risk assessment?
Most of the ones organizations already carry. ISO/IEC 27001 requires an information security risk assessment process under Clause 6.1.2. The HIPAA Security Rule requires it at 45 CFR 164.308(a)(1)(ii)(A). The FTC Safeguards Rule requires a written risk assessment that every safeguard must trace back to. CMMC and NIST SP 800-171 require it, as does FedRAMP. SOC 2 auditors expect it as evidence of the risk assessment criteria.
Is a vulnerability scan a risk assessment?
No, and treating one as the other is the most common reason an internally produced assessment fails review. A scan identifies technical weaknesses and assigns severity from a database. A risk assessment identifies threats to specific assets, scores likelihood and impact in your context, calculates risk before and after controls, and produces treatment decisions with owners. The scan is an input to the assessment.
What is the difference between inherent and residual risk?
Inherent risk is exposure before existing controls are considered, calculated here from Threat Impact Factors and Asset Category Values. Residual risk applies control effectiveness scores to that figure, reflecting the posture that actually exists. The gap between the two is what the control environment is buying you, and it is the number that should drive investment decisions.
Can one assessment satisfy several frameworks?
Usually, if it is scoped that way from the start. The frameworks differ on documentation format and review cadence rather than on the underlying discipline. An assessment scoped for a single framework and later presented for another generally fails on scope or on documentation format rather than on the analysis itself, so establishing every applicable requirement before beginning is what makes reuse possible.
How often should it be updated?
At least annually, and whenever a material change occurs in systems, data, service providers, or the threat environment. Every framework that requires the assessment also requires it to be current, and an assessment that describes an environment that no longer exists fails the same test it originally passed.
What does the report actually contain?
A threat inventory tied to your assets, control effectiveness findings, inherent and residual risk per risk scenario, and treatment recommendations across modification, retention, avoidance, and sharing, with specific actions covering technology, policy, and procedure. The treatment decisions and their owners are the part an assessor tests and the part most internal assessments omit.