Cyber Security Compliance · HITRUST
HITRUST Certification Services
e1, i1, r2 and AI Security Assurance Readiness
Two things decide a HITRUST project and neither is in most published guidance. The scoring threshold is applied per domain, not to the overall average, so a single weak domain produces a validated report rather than a certification even when the aggregate looks healthy. And HITRUST retires CSF versions for new assessments on a published schedule, so a project that drifts can find its target version closed. New e1, i1 and rapid assessments moved to CSF v11.8.0 on 7 May 2026. Elevate Consult manages both, from scoping through validated assessment and quality assurance.
2026 UPDATE
What decides a HITRUST outcome
Certification is won or lost per domain
Every assessment domain has to reach the required rating. A single weak domain produces a validated report rather than a certification, even where the overall average looks comfortable. Programs that manage to an average score rather than to the weakest domain are managing the wrong number.
CSF versions close on a schedule
HITRUST retires versions for new assessments on published dates. New e1, i1 and rapid assessments moved to CSF v11.8.0 on 7 May 2026. A readiness project that slips can find its intended version unavailable, which forces a delta review and additional assessor work. Confirm the current version at scoping, not at submission.
AI assurance is now part of the portfolio
HITRUST offers AI security and AI risk management assurance, and neither is a standalone assessment: both are combined with an underlying e1, i1 or r2 certification. The AI security certification carries a higher control maturity threshold than the AI risk management one, so organizations should scope the AI factor at the start rather than adding it later.
Inheritance reduces the work where it applies
Organizations can inherit controls from certified cloud service providers, and a substantial share of the AI security requirements are at least partially inheritable where the AI service provider participates in the HITRUST external inheritance program. Establishing what is inheritable before the readiness assessment changes the size of the project.
The three types are products, not steps
e1, i1 and r2 are separate assessments with different scope, rigor and validity, not a progression an organization must climb. The right answer usually comes from the customer requirement rather than from an internal maturity ambition.
What HITRUST is
A certifiable framework that harmonizes others
The HITRUST CSF integrates security, privacy and regulatory requirements into a single scalable framework, mapping to authoritative sources including HIPAA, ISO 27001, NIST SP 800-53 and others. The value is that one assessment answers several questions a customer or regulator would otherwise ask separately.
The framework is organized into control categories, control objectives and assessment domains, and the domain structure is what the certification threshold is applied against.
The Security Rule requires administrative, physical and technical safeguards. The Privacy Rule governs use and disclosure. The Breach Notification Rule sets what happens when protection fails. HITECH expanded enforcement, including authority for state attorneys general to bring civil actions
The three assessment types
Scope, rigor and validity differ
Choosing the type is the first decision and it should follow the customer requirement. Health systems and payers frequently specify the assessment type in their vendor requirements, and delivering an e1 where an i1 was specified satisfies nobody.
e1 (Essential)
Around 44 requirement statements
Foundational cyber hygiene covering the highest priority requirements including access control, multi-factor authentication, encryption, incident response and patch management. Scored on implementation maturity rather than the full PRISMA model. Valid for one year.
i1 (Implemented)
Around 182 requirement
statements
The e1 statements plus broader leading practices addressing a wider range of active threats. No risk-based scoping, but a rapid recertification option streamlines annual renewal. Scored on implementation maturity. Valid for one year.
r2 (Risk-based)
Typically 300 to 400 statements
Uses the i1 requirements as a baseline and tailors additional requirements through risk-based scoping. Scored across the full five PRISMA maturity levels: policy, procedure, implemented, measured and managed. Two year cycle with an interim assessment, which makes it a continuous programme rather than an annual event.
AI security certification
Combined, not standalone
Added to an underlying e1, i1 or r2 through the Security for AI Systems compliance factor, available from CSF v11.4.0. Carries its own control maturity threshold, higher than the AI risk management product.
AI risk management
Combined, not standalone
The companion AI assurance product with a lower maturity threshold, also dependent on the underlying certification path.
Inheritance
Reduces scope where available
Controls can be inherited from certified cloud service providers, and a majority of AI security requirements are at least partially inheritable where the AI service provider participates in the external inheritance program.
Our approach
Gap analysis, risk analysis, remediation, sustainment
Elevate works from OCR’s own audit protocols and the HHS and CMS guidance, rather than from a generic security checklist relabeled for healthcare.
Gap analysis
Security Rule, Breach Notification Rule and Privacy Rule gap analysis against the mandated standards, using OCR audit protocols alongside CMS and HHS guidance.
Security risk analysis
Conducted against the nine essential elements, aligned to NIST SP 800-30 and NIST SP 800-66 Revision 2, correlated with applicable state and federal requirements beyond HIPAA itself.
Customized action plans
A compliance roadmap sized to the organization’s environment and operating reality, sequenced so the most enforced gaps close first.
Staff training
In-person and remote training covering current HIPAA and HITECH obligations, aimed at the human error that drives a substantial share of reportable incidents.
Business associate management
Review of business associate agreements and, increasingly, verification that associates have actually implemented the safeguards they agreed to, which the proposed rule would make explicit.
Implementation and monitoring
Support implementing safeguards and ongoing monitoring, including readiness work against the proposed Security Rule requirements that would be hardest to build under a 240 day clock.
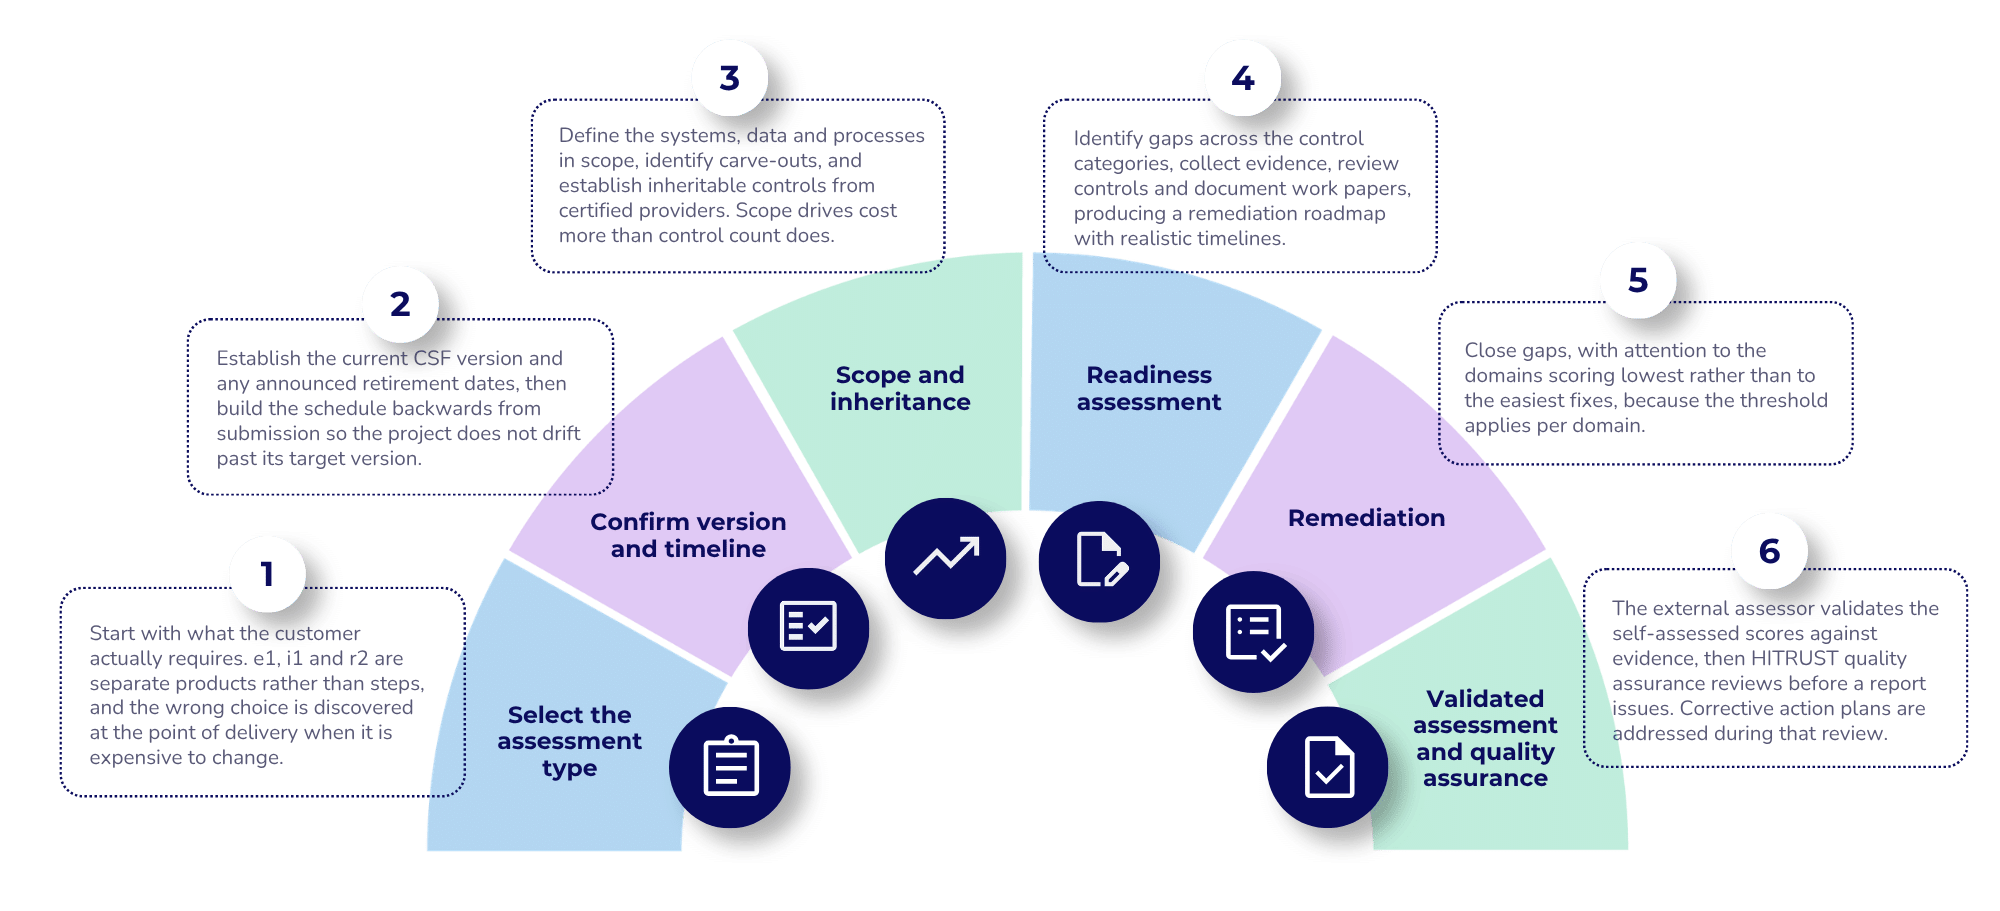
ENGAGEMENT PHASES
How the work runs
WHO THIS IS FOR
Roles Elevate works with on this standard
GET STARTED
Ready to scope your HITRUST path?
Whether the driver is a health system vendor requirement specifying e1, i1 or r2, or an AI assurance question from a customer, Elevate Consult scopes the assessment, manages the domain scores that decide the outcome, and supports the validated assessment through quality assurance.
FAQ
Common Questions
What is the difference between e1, i1 and r2?
They are separate assessment products rather than stages. The e1 covers around 44 requirement statements focused on foundational cyber hygiene and is valid for one year. The i1 covers around 182 statements, adding broader leading practices, also valid for one year with a rapid recertification option. The r2 uses the i1 requirements as a baseline and tailors additional requirements through risk-based scoping, typically reaching 300 to 400 statements, on a two year cycle with an interim assessment.
How is a HITRUST assessment scored?
The r2 evaluates controls across the five PRISMA maturity levels: policy, procedure, implemented, measured and managed. The e1 and i1 focus on implementation maturity rather than the full model. Critically, the threshold is applied per assessment domain. A single domain below the required rating produces a validated report rather than a certification even when the overall average looks healthy, which is why domain-level tracking matters more than the aggregate score.
Which CSF version applies to our assessment?
The current one at the time the assessment object is created. HITRUST retires versions for new assessments on a published schedule, and new e1, i1 and rapid assessments moved to CSF v11.8.0 on 7 May 2026. Confirm the version and any announced deadlines at scoping rather than at submission, because a project that drifts past a retirement date requires a delta review and additional assessor work.
Does HITRUST cover AI?
Yes. Organizations can inherit controls from certified cloud service providers, and for AI security requirements a majority are at least partially inheritable where the AI service provider participates in the HITRUST external inheritance program. Establishing what is inheritable before the readiness assessment materially changes the size of the project, so it belongs in scoping rather than in remediation.
Can we reuse work from a certified cloud provider?
Yes. Organizations can inherit controls from certified cloud service providers, and for AI security requirements a majority are at least partially inheritable where the AI service provider participates in the HITRUST external inheritance program. Establishing what is inheritable before the readiness assessment materially changes the size of the project, so it belongs in scoping rather than in remediation.
Can we do the assessment ourselves?
Readiness work can be done internally or with an advisor, but the validated assessment must be performed by a HITRUST approved external assessor and is then quality assured by HITRUST before a report is issued. Elevate works as the advisor through readiness, remediation and assessor collaboration, which keeps the assessor independent while the organization has someone on its side of the table.