Organizations are rapidly embracing artificial intelligence – 72% now use AI in at least one business function, a significant jump from 55% last year. The world’s first international standard for ...
ISO 27001 and SOC 2 are two of the most prominent frameworks businesses rely on today for information security. ISO 27001 enjoys global recognition as a detailed approach to information ...
CMMC 2 compliance has become mandatory for defense contractors, yet a report reveals that only 1% of defense contractors are ready for their CMMC audits. Every executive in the defense ...
The Defense Industrial Base (DIB) cybersecurity system relies on specialized assessors to confirm compliance through the CMMC AB ecosystem. C3PAOs, or Certified Third-Party Assessment Organizations, are the exclusive entities that ...
The Department of Defense has finalized CMMC requirements under 32 CFR Part 170, setting November 10, 2025 as the official deadline. Defense contractors need to start preparing right away. Every ...
The CMMC 2.0 levels underwent substantial simplification with the revised framework’s release in October 2024. The original five-tier model transformed into three complete compliance levels. This change marks a crucial ...
Teams that can’t explain their data’s origin, changes, or results face AI systems that simply don’t work. This vulnerability destroys trust and makes AI applications less effective in industries of ...
The market for AI governance tools is expanding quickly as organizations face mounting pressure to manage artificial intelligence responsibly. The regulatory backdrop is the main driver. In the European Union, ...
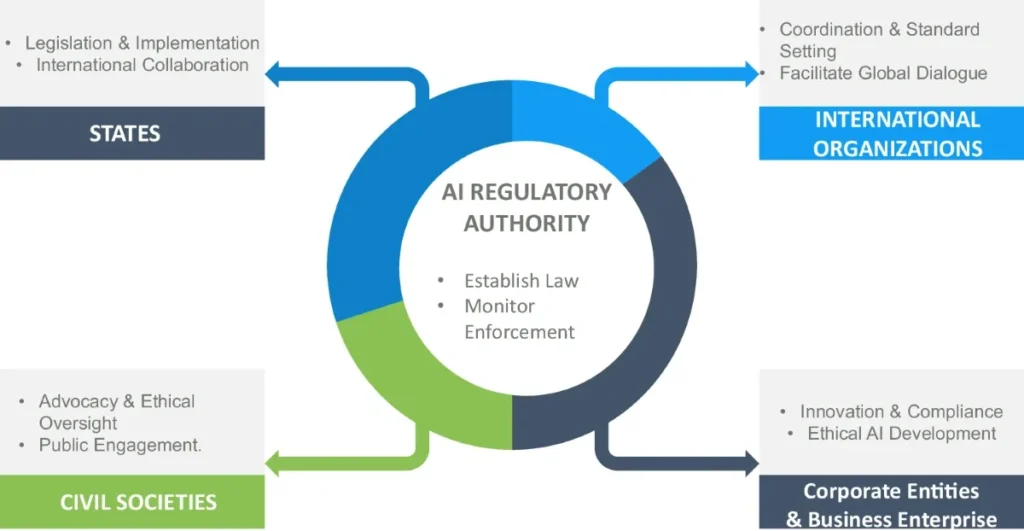
AI governance is the set of frameworks, policies and controls that determine who answers for an AI system when it causes harm, and in 2026 the answer to that question ...
AI governance matters more than ever as technology advances faster in organizations worldwide. Knowledge workers have embraced AI tools, with over 70% using them weekly. Yet only 30% of organizations ...