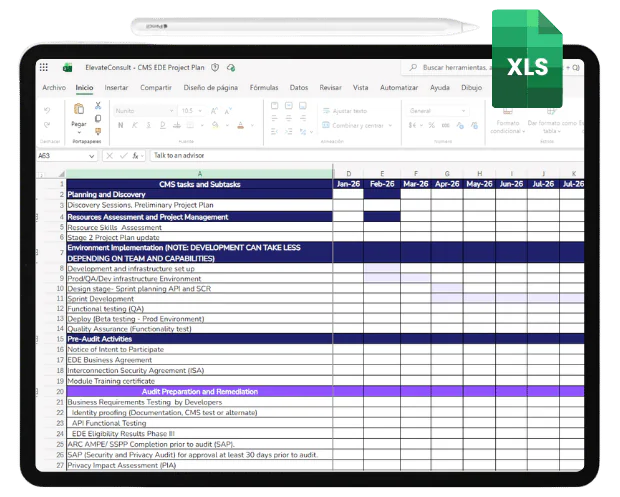
The complete CMS EDE project plan and audit timeline.
One editable workbook: every phase from discovery to open enrollment, the CMS submission document checklist, and the 36 EDE API functions your build must pass.
8
+16
36
Editable
WHAT IS INSIDE
The whole CMS EDE path in one place.
The reference organizes the Class A requirements of FedRAMP 20x so a cloud service provider can see what to demonstrate and where each item traces back to.
Full phase-by-phase timeline
Eight phases mapped across a monthly timeline, from discovery and build to the audit, submission, and open enrollment.
The CMS submission checklist
The security and privacy documents CMS requires for the package, as a readiness checklist you can assign and track.
The 36 EDE API functions
Every Marketplace API function your build must implement and test, grouped by area, so nothing is missed in scoping.
Editable, not a static PDF
A workbook you adapt to your target year and team, so it becomes your plan, not a document you read once.
Three steps to a realistic CMS EDE schedule
Download the workbook
Enter your work email and get the plan instantly, including the cover and the how-to-use guide.
Adapt it to your program
Set your target year, tune the durations to your team, and work backward from the CMS submission window.
Book a no-cost readiness call
Have an Elevate advisor pressure-test your plan and show you where the security and privacy gaps are.
Elevate CMS EDE Project Plan
The same planning workbook Elevate uses to scope Enhanced Direct Enrollment engagements, ready for you to adapt.
- Eight-phase timeline from discovery to open enrollment
- The CMS package document checklist
- All 36 Marketplace API functions
- Cover and how-to-use guide included
WHAT IS INSIDE
Eight phases and the documents CMS expects.
The eight phases
- Planning and discovery
- Environment implementation and build
- Pre-audit activities
- Audit preparation and remediation
- Audit and package preparation
- Audit submission
- Package approval and corrections
- Open enrollment authorization
The CMS package documents
- System Security and Privacy Plan (SSPP)
- Security and Privacy Assessment Report (SAR)
- Plan of Actions and Milestones (POA&M)
- Penetration test and vulnerability scans
- Privacy Impact Assessment (PIA)
- Incident Response and Contingency plans
- Interconnection Security Agreement (ISA)
- Section 508 accessibility testing
BUILT BY A SECURITY AND PRIVACY AUDIT TEAM
The EDE package is a security and privacy audit. That is what Elevate does.
Most of the CMS EDE submission is a security and privacy audit and its evidence: the SSPP, the SAR, the POA&M, penetration testing, and months of vulnerability scans. That is the core of Elevate’s practice, not an adjacent service.
This plan reflects how Elevate scopes and sequences that work in real engagements, so the timeline you build is grounded in the artifacts an assessor will actually ask for.
Download it, adapt it, and if you want a second set of eyes, an advisor will walk your plan with you at no cost.
+18
Years in cybersecurity and compliance
+500
Clients served across industries
+500
+100%
Do not guess your CMS EDE timeline.
Download the plan, map your phases, and let an Elevate advisor tell you where the security and privacy work will actually take the longest.


QUESTIONS
Frequently Asked Questions
What is CMS Enhanced Direct Enrollment (EDE) Phase III?
CMS Enhanced Direct Enrollment (EDE) is a pathway that lets approved partners host the full Marketplace eligibility and enrollment experience on their own platform. Phase III is the most advanced tier, covering the complete application, eligibility, plan shopping, and enrollment flow. Reaching it requires a development effort plus a CMS security and privacy audit.
What does the CMS EDE audit submission package include?
The package centers on a security and privacy audit and its evidence: a System Security and Privacy Plan (SSPP), a Security and Privacy Assessment Report (SAR), a Plan of Actions and Milestones (POA&M), a penetration test, vulnerability scans, a Privacy Impact Assessment, Incident Response and Contingency plans, agreements such as the Interconnection Security Agreement (ISA), and Section 508 accessibility testing.
How long does CMS EDE Phase III authorization take?
It depends on your starting security posture, team size, and how much of the platform you build versus reuse. The plan breaks the work into phases so you can build a realistic schedule backward from the CMS submission window and open enrollment, rather than committing to a single number up front.
What is a FedRAMP 20x Class A certification?
Class A is one of the certification classes in the FedRAMP 20x model. The Class A requirements are a defined set of Key Security Indicators and FedRAMP Requirements rules. The Elevate FedRAMP 20x Class A KSI Reference organizes those requirements in one place so a provider can see what to demonstrate for Class A.
How is FedRAMP 20x different from FedRAMP Rev 5?
FedRAMP Rev 5 produces a documented package against NIST SP 800-53 Rev 5, including a System Security Plan and an assessor report. FedRAMP 20x shifts to Key Security Indicators proven with automated evidence, and submits packages as machine-readable files rather than as a document. The 20x KSIs still trace back to recognized security fundamentals.
What is inside the Elevate CMS EDE Project Plan?
An editable workbook with a phase-by-phase timeline from discovery through open enrollment, a checklist of the documents CMS requires for the package, and the 36 Marketplace API functions your build must implement and test. It also includes a cover and a how-to-use guide explaining the color legend and how to read the plan.
Is the Elevate CMS EDE Project Plan an official CMS document?
No. It is a working aid built by Elevate Consult to help you plan, not an official CMS submission or a determination of readiness. Durations and dates are illustrative and must be confirmed against current CMS EDE program guidance. It is not legal or compliance advice.