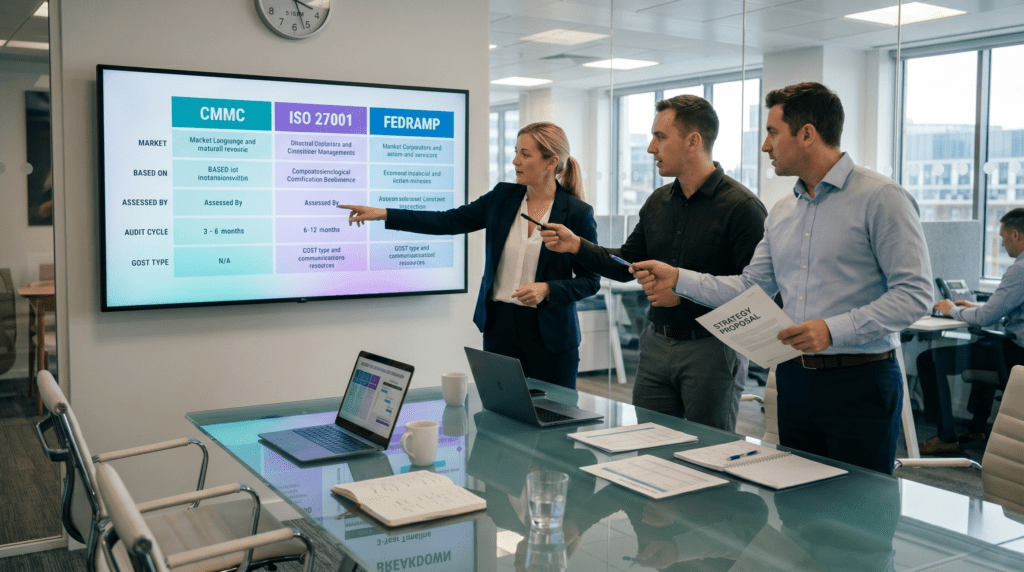
Companies pursuing federal or enterprise business quickly run into a wall of acronyms, and the most common question is which of the major cybersecurity compliance frameworks they actually need. CMMC, ...
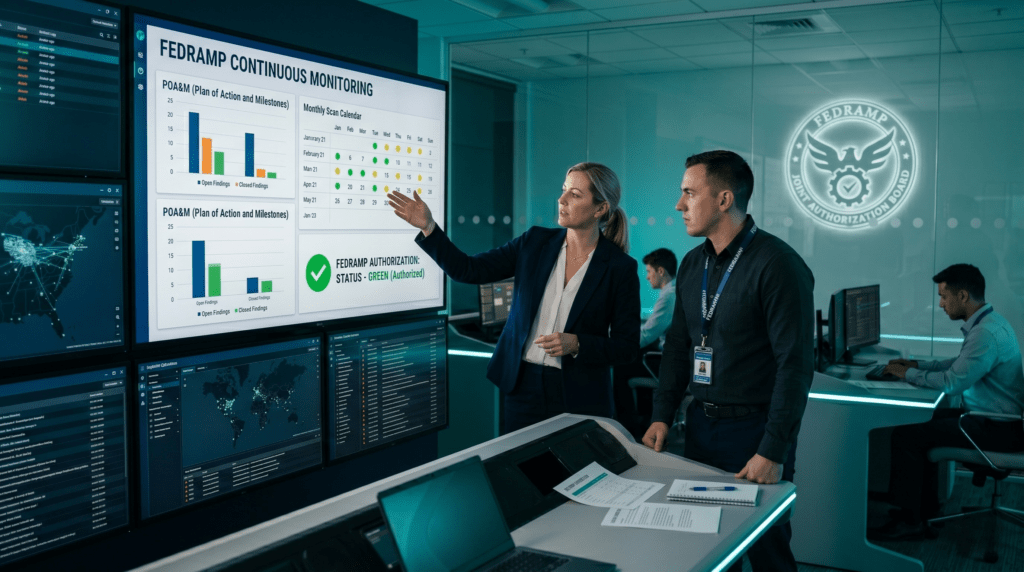
Earning a FedRAMP Authorization to Operate is a milestone, but it is the start of the work, not the end of it. FedRAMP continuous monitoring is the ongoing discipline that ...
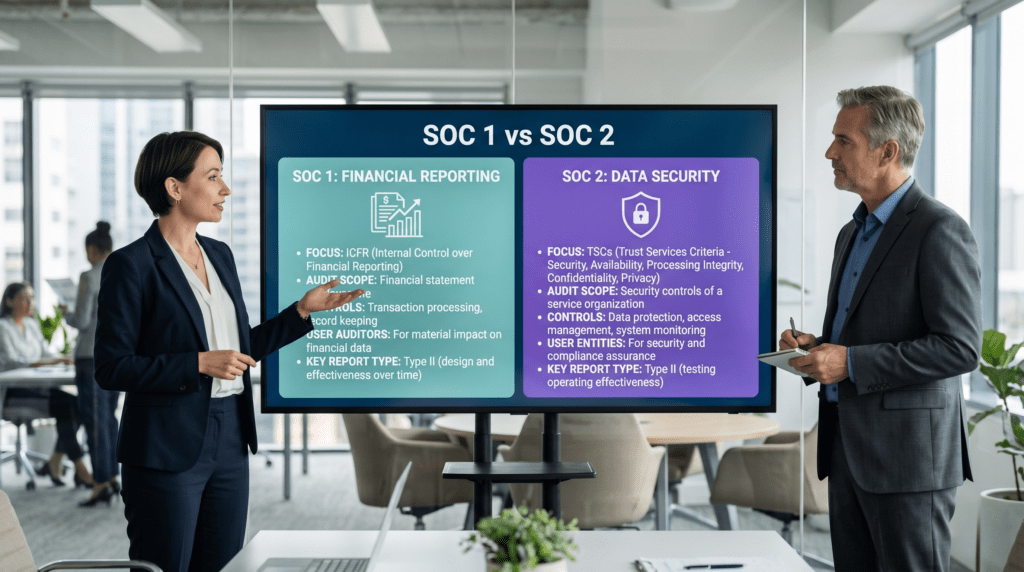
When a customer or partner asks for “a SOC report,” they could mean one of two very different things, and confusing them wastes time and money. SOC 1 vs SOC ...
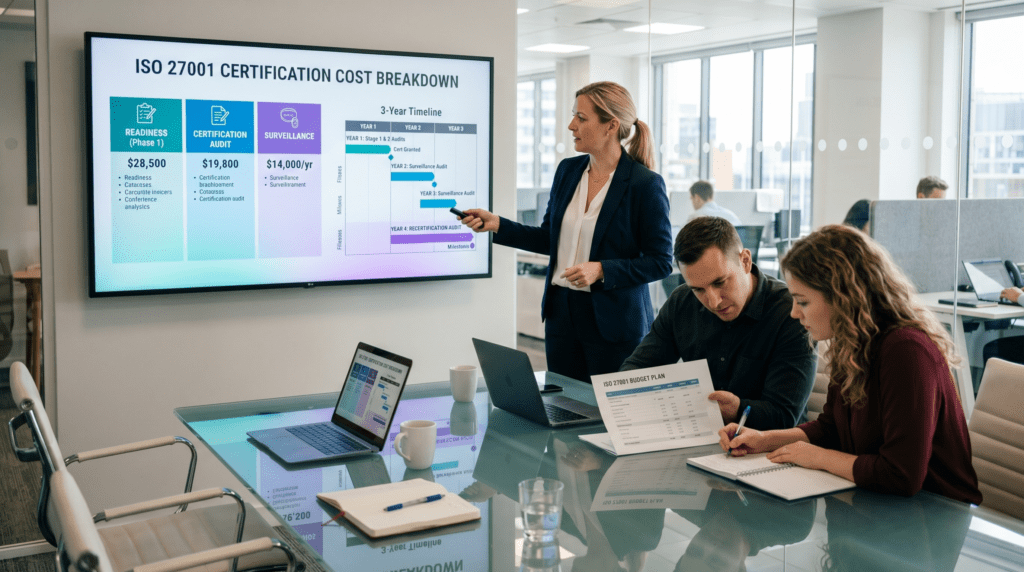
One of the first questions any company asks before pursuing the standard is what ISO 27001 certification cost actually looks like, and the honest answer is that it depends on ...
Companies that handle customer data or process transactions on behalf of their clients often need a SOC report, and many discover they need help getting there. SOC 2 consulting exists ...
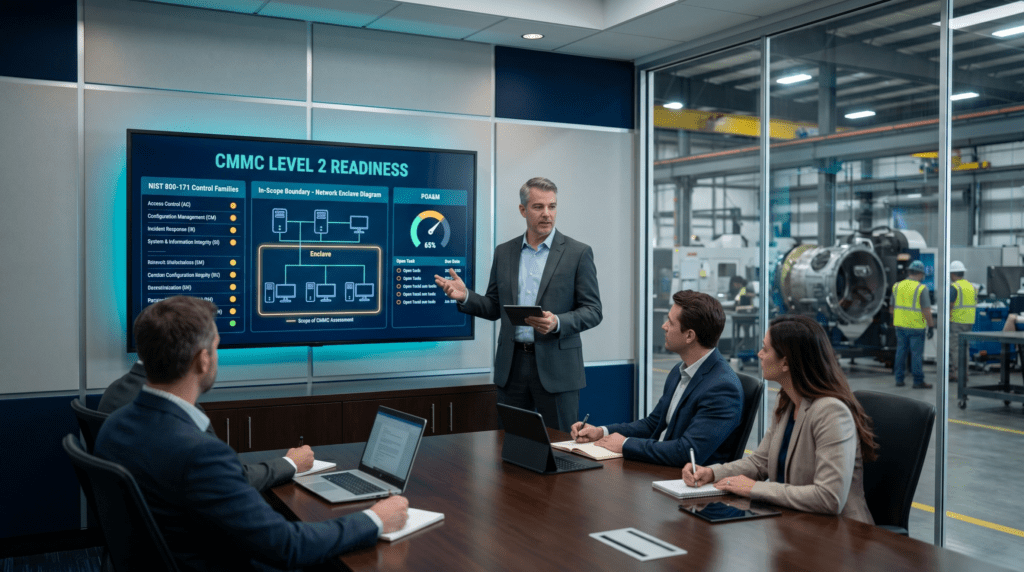
For defense contractors that handle controlled unclassified information, CMMC Level 2 is now a condition of doing business with the Department of War, and most organizations cannot get there alone. ...
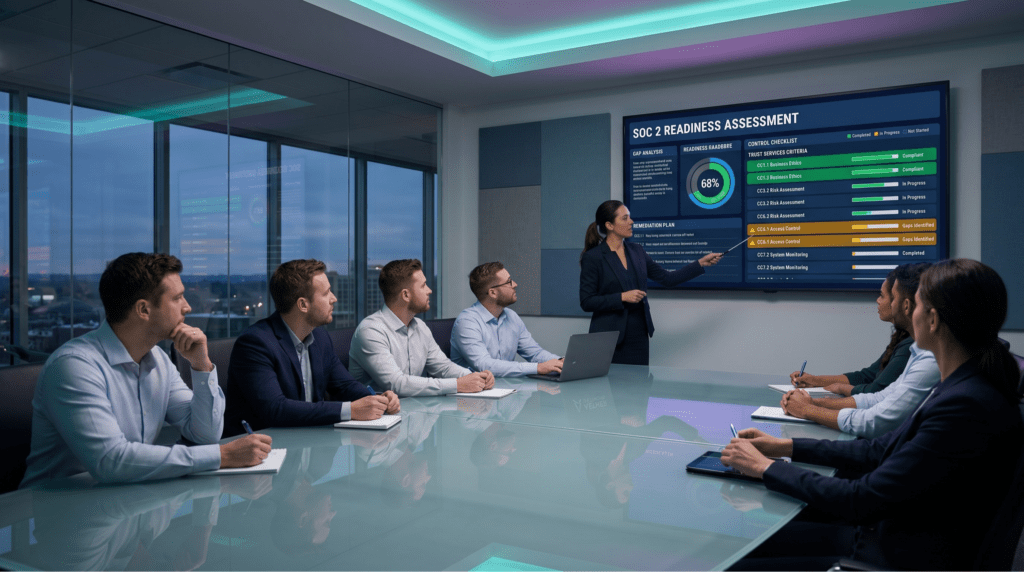
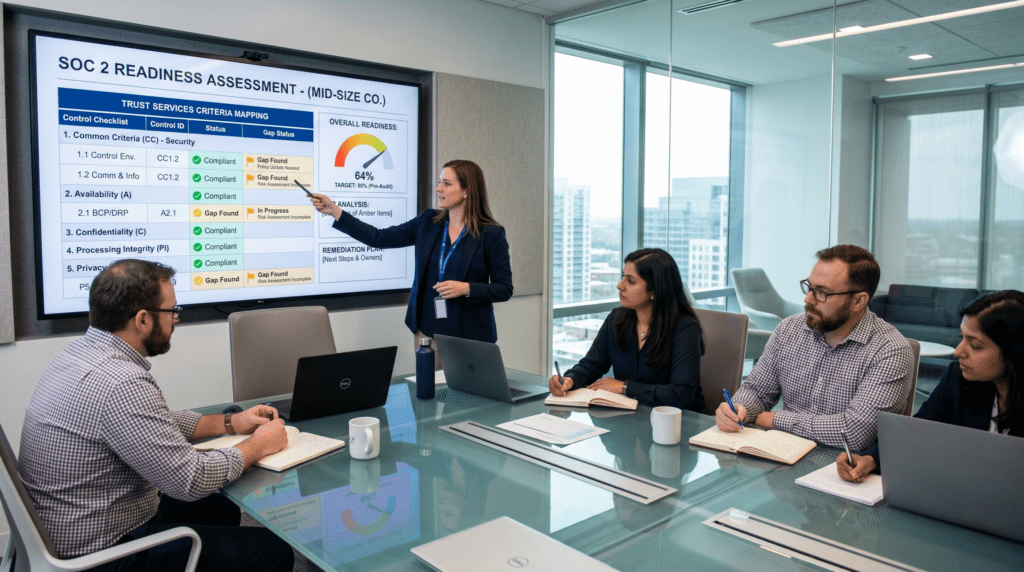
A SOC 2 readiness assessment is the step that decides whether the formal audit goes smoothly or turns into an expensive scramble. It is the gap analysis that happens before ...
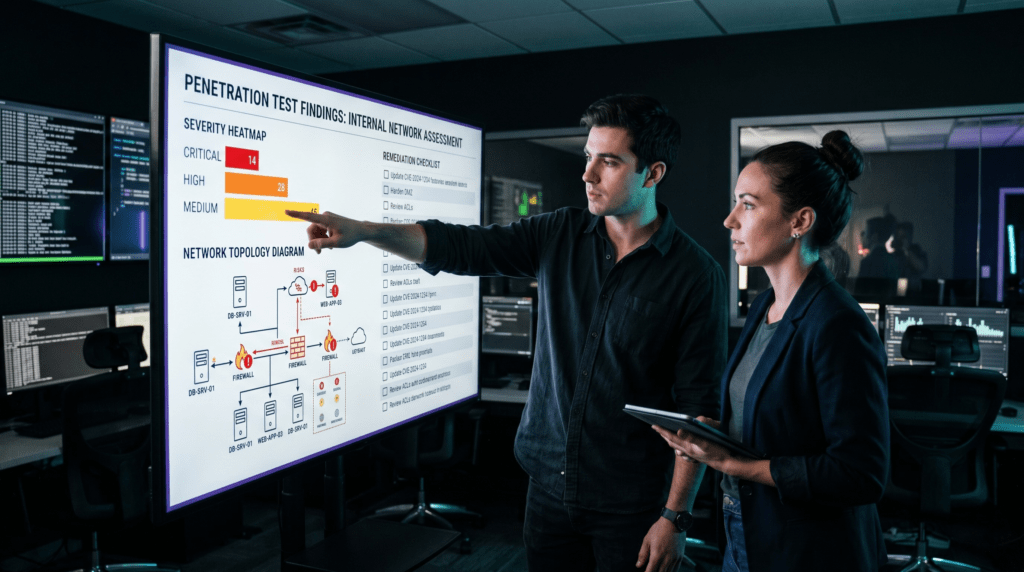
Choosing among penetration testing companies is harder than it looks, because the term covers everything from a deep, manual adversarial assessment to an automated scan dressed up in a polished ...
For most B2B startups, SOC 2 stops being optional the moment a serious enterprise prospect sends a security questionnaire. The deal is on the table, the buyer’s security team wants ...
AI governance software could unlock between $200 billion and $240 billion in annual value for the global banking sector alone. Generative AI is changing the way companies handle risk and ...