FedRAMP 20x • CR2026
FedRAMP 20x Class A KSI Reference
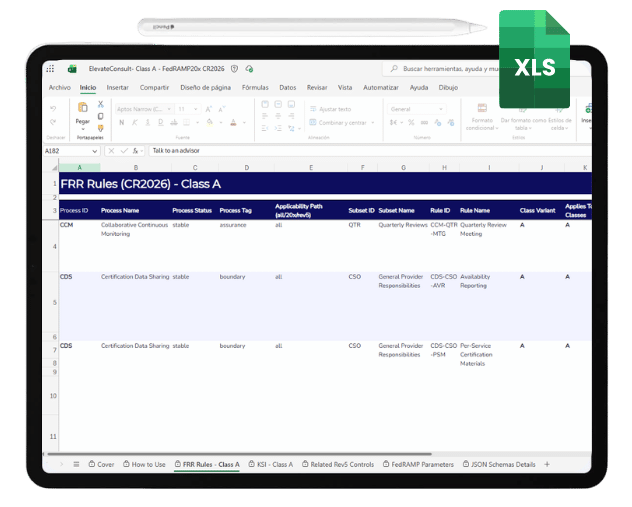
The Class A requirements of FedRAMP 20x in one place: the Key Security Indicators, their NIST 800-53 Rev 5 mappings, the FedRAMP Requirements rules, and the parameters. Built by Elevate’s FedRAMP practice from the CR2026 ruleset.
XLSX • CR2026 ruleset • No-cost download
7
6
46
66
WHAT IS INSIDE
Everything a Class A package needs to account for, in one document.
The reference organizes the Class A requirements of FedRAMP 20x so a cloud service provider can see what to demonstrate and where each item traces back to.
7
Class A Key Security Indicators
The 7 indicators across 6 families that a provider demonstrates for a Class A certification, with the capability statement for each.
66
Related NIST 800-53 Rev 5 controls
The referenced controls with FedRAMP guidance, provided for reference and lineage, not as separate requirements to satisfy one by one.
46
FedRAMP Requirements (FRR) rules
The FRR rules across 11 processes, each marked MUST, MUST NOT, SHOULD, or MAY, so the force of every obligation is clear.
+
FedRAMP parameters
FedRAMP-defined values and guidance for specific controls, such as phishing-resistant multifactor authentication.
The Key Security Indicators are mapped to NIST 800-53 Rev 5 for reference only. Unlike Rev 5, there is no requirement to meet the intent of every individual control. The mapping is guidance that helps a provider decide how much information to include in its certification package.
WHY IT MATTERS
FedRAMP 20x changed what a provider has to prove.
The Rev 5 path asks a provider to document hundreds of controls one by one. FedRAMP 20x replaces that with Key Security Indicators, a smaller set of security capabilities proven with automated, machine-readable evidence.
For a provider planning a Class A certification, the first hard question is scope: which requirements apply, and how much evidence is enough. Guessing wide wastes months. Guessing narrow fails the package. This reference gives the provider the Class A picture in one place, drawn from the CR2026 ruleset.
🡶 See the Class A scope at a glance. The indicators, rules, and parameters that apply to a Class A certification, without reading the full ruleset.
🡶 Understand the Rev 5 relationship. Each KSI shows its 800-53 mapping, so a team coming from Rev 5 can see the lineage without treating every control as a separate requirement.
🡶 Judge how much to include. The mapping and the force language help a provider decide how much information belongs in the package.
🡶 Start the conversation with evidence. The reference is the diagnosis. An Elevate advisor helps turn it into a package.
Download the FedRAMP 20x Class A KSI Reference
Get the PDF and keep it next to your certification planning. Built from the CR2026 ruleset by Elevate’s FedRAMP practice.
- 7 Class A Key Security Indicators
- NIST 800-53 Rev 5 mappings for reference
- 46 FedRAMP Requirements rules
- FedRAMP parameters and force language
Get FedRAMP 20x certification guidance
Have the reference and want a read on your Class A scope? An Elevate advisor will walk through where your service stands and what a package would take.
QUESTIONS
FedRAMP 20x, in plain terms
What is FedRAMP 20x?
FedRAMP 20x is a modernized FedRAMP authorization path for cloud service providers. Instead of documenting hundreds of NIST 800-53 controls one by one, a provider demonstrates a set of Key Security Indicators with automated, machine-readable evidence. The current requirements are defined by the CR2026 ruleset.
What are Key Security Indicators (KSIs) in FedRAMP 20x?
Key Security Indicators are the requirement model for FedRAMP 20x. Rather than listing controls to document, each KSI states a security capability the provider must demonstrate and continuously validate. The Elevate FedRAMP 20x Class A KSI Reference lists the indicators that apply to a Class A certification, grouped by family.
Does FedRAMP 20x still use NIST 800-53 controls?
The KSIs are mapped to NIST SP 800-53 Rev 5 controls for reference. Unlike the Rev 5 path, there is no requirement to meet the intent of every individual control. The mapping is guidance that helps a provider decide how much information to include in its certification package.
What is a FedRAMP 20x Class A certification?
Class A is one of the certification classes in the FedRAMP 20x model. The Class A requirements are a defined set of Key Security Indicators and FedRAMP Requirements rules. The Elevate FedRAMP 20x Class A KSI Reference organizes those requirements in one place so a provider can see what to demonstrate for Class A.
How is FedRAMP 20x different from FedRAMP Rev 5?
FedRAMP Rev 5 produces a documented package against NIST SP 800-53 Rev 5, including a System Security Plan and an assessor report. FedRAMP 20x shifts to Key Security Indicators proven with automated evidence, and submits packages as machine-readable files rather than as a document. The 20x KSIs still trace back to recognized security fundamentals.
Is the Class A Reference an official FedRAMP submission?
No. The reference is a working aid. Official FedRAMP 20x packages are submitted as machine-readable files, not as a document. Requirement values are version-sensitive and should be confirmed against the current CR2026 ruleset. The reference is not legal or compliance advice.